
Zum Hauptinhalt springen
tsecurity.de LIVE
Echtzeit-Radar & Feeds
Alle RSS Feeds
👥 Community & Social
Sichere ProgrammierungWhat's one small dev habit that made a big difference for you?(20.09.2026 um 08:10 Uhr)
Sichere ProgrammierungI Built Shree AI OS — A Deterministic AI Runtime for Java 21(20.09.2026 um 08:20 Uhr)
Sichere ProgrammierungSaddle-Stitch PDF Imposition: Why Page Counts Must Be Multiples of 4(20.09.2026 um 08:20 Uhr)
Sichere Programmierungfvpn - Lightweight CLI VPN Client for FastestVPN on Linux(20.09.2026 um 08:20 Uhr)
Sichere ProgrammierungMy Monitoring Cron Never Ran Once. crontab -l Showed It Fine.(20.09.2026 um 08:49 Uhr)
IT Security ToolsBrowserBox v19.0.3(20.09.2026 um 08:30 Uhr)
IT Security NachrichtenHackerangriff auf Smart Locks: Diese Schwachstellen sollte jeder kennen(20.09.2026 um 07:00 Uhr)
Sichere ProgrammierungWhat's one small dev habit that made a big difference for you?(20.09.2026 um 08:10 Uhr)
Sichere ProgrammierungI Built Shree AI OS — A Deterministic AI Runtime for Java 21(20.09.2026 um 08:20 Uhr)
Sichere ProgrammierungSaddle-Stitch PDF Imposition: Why Page Counts Must Be Multiples of 4(20.09.2026 um 08:20 Uhr)
Sichere Programmierungfvpn - Lightweight CLI VPN Client for FastestVPN on Linux(20.09.2026 um 08:20 Uhr)
Sichere ProgrammierungMy Monitoring Cron Never Ran Once. crontab -l Showed It Fine.(20.09.2026 um 08:49 Uhr)
IT Security ToolsBrowserBox v19.0.3(20.09.2026 um 08:30 Uhr)
IT Security NachrichtenHackerangriff auf Smart Locks: Diese Schwachstellen sollte jeder kennen(20.09.2026 um 07:00 Uhr)
Intelligence View
⚡ tsecurity.de Intelligence

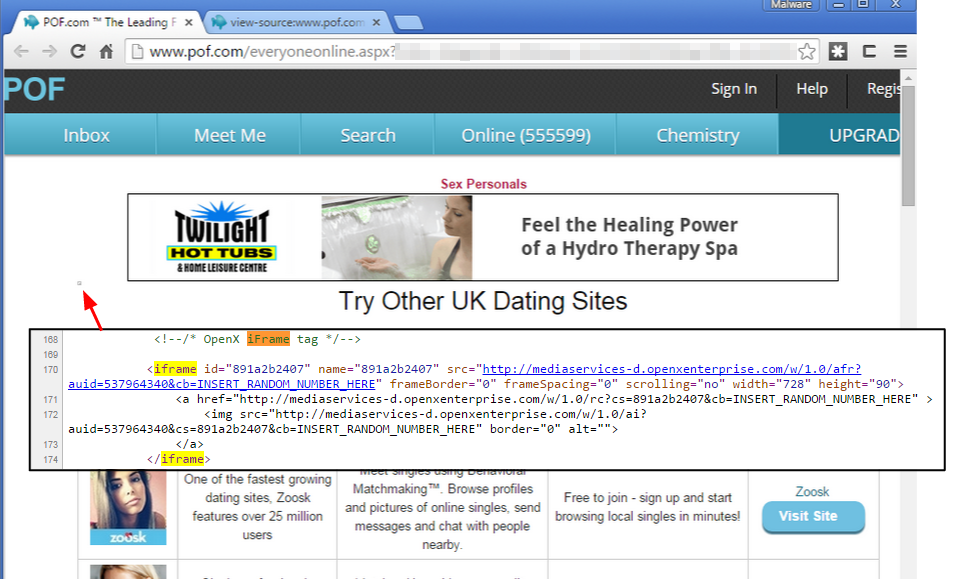
Researchers detect Malvertising in PlentyOfFish

Photo Courtesy: Malwarebytes

Researchers from Malwarebytes Unpacked, a security firm, have detected a malvertising, which derived from “malicious advertising" uses online advertising to spread malware and it involves malware-laden advertisements into legitimate online advertising websites, in the PlentyOfFish, a Vancouver-based online dating service which makes money from advertising.

The researcher have warned the users not to click on the adverts as they are automatically targeted by using an attack that detects if their computer can be infected (via outdated software), and launches directly that way.

Soon after the flaw detected, they have contacted the company concerned to make them aware of this issue.

According to the researchers, the attack chain uses the Google URL shortener goo.gl as intermediary to load the Nuclear exploit kit.

“While we see this mechanism quite frequently within our telemetry, it is particularly difficult to reproduce it in a lab environment,” the researcher wrote in a blogpost. The ad network involved in the malvertising campaign (ad.360yield.com) was familiar and it turns out that we had observed it in a rare attack captured by our honeypots just one day prior.”

The sample was collected from the Tinba banking Trojan. Given that the time frame of both attacks and that the ad network involved is the same, chances are high that pof[dot]com dropped that Trojan as well.

According to a news report published in The Register, the attack against PlentyOfFish comes against the backdrop of the fallout from the data dump by hackers who breached cheaters’ hook-up website Ashley Madison, and the earlier attack against AdultFriendFinder.

 There’s nothing to link the three attacks directly, however it’s fair to say that dating and adult hook-up websites are very much in the firing line of hackers, so extra precautions ought to be applied.
Ähnliche Beiträge
🔍 Verwandte News

Auch interessante Nachrichten Researchers detect Malvertising in PlentyOfFish

Thematisch verwandte Begriffe: Researchers, detect, Malvertising, PlentyOfFish · 6 Treffer

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Zum Aktualisieren ziehen
ZERO-DAY CVE-2026-93987 | rclone versions 1.56.0 through 1.75.0 contain a path traversal vulnerabi…
Advisory →
TTS Reader • tsecurity.de Voice
tsecurity.de Icon
tsecurity.de App
Offline-Lesen, Eilmeldungen & 0ms Ladezeit

Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.

Nächster Beitrag
Themen-Radar & Intelligence Matrix
Echtzeit-Taxonomie nach Angriffsvektoren & Plattformen
Community Radar & Live Chat
Sentinel Bot online • Live-Stream
Dein Cluster: Security Explorer
Match:
lädt…
Verbindung zum Community-Stream wird aufgebaut...
Bearbeitungsmodus — Senden überschreibt deine Nachricht
Community-Puls — was gerade passiert
lädt…
Aktivitäten deiner Analysten
lädt…
Neues Thema oder Eilmeldung einreichen

Reiche interessante Links, Zero-Days oder Debatten ein. Die Community entscheidet per Upvote über die Veröffentlichung.

Heiß diskutierte Einreichungen
🔖 Gespeicherte Artikel
📂 Keine gespeicherten Artikel vorhanden.
Zurück Ziehen Vor
Links: vorheriger Artikel Rechts: nächster Artikel unten: schließen
News NIS-2 Frühwarnung Tier-1 Intel ⏱️ 3 Min vor 10 Min
Artikeldaten werden geladen...

Zurück: vorheriger Vor: nächster
↗ Original-Quelle
Social Reaktionen Deine Reaktion zählt
Einstufung & Relevanz-Poll 0 Stimmen
In sozialen Netzwerken teilen 1-Klick