
Zum Hauptinhalt springen
tsecurity.de LIVE
Echtzeit-Radar & Feeds
Alle RSS Feeds
👥 Community & Social
Sichere ProgrammierungKI half beim Finden: iOS 27 schließt mehr als 100 Sicherheitslücken(21.09.2026 um 06:00 Uhr)
Sichere ProgrammierungWhat Is Rowhammer? How Can Repeated Memory Access Flip Bits in RAM?(21.09.2026 um 07:12 Uhr)
Sichere Programmierungnpm publish Ignores .gitignore: The .npmignore Override Rule(21.09.2026 um 07:15 Uhr)
Sichere ProgrammierungAphelion Editor - A free node-based video / VFX editor(21.09.2026 um 07:21 Uhr)
Sichere ProgrammierungGovernance Attack Surface Review: OKX(21.09.2026 um 07:31 Uhr)
Sichere ProgrammierungJSM Portal Request Create Property Panel Submit(21.09.2026 um 07:34 Uhr)
Reverse Engineeringsearch instructions assembly easy (X86,RISCV,AARCH64,etc)(20.09.2026 um 15:44 Uhr)
Sichere ProgrammierungKI half beim Finden: iOS 27 schließt mehr als 100 Sicherheitslücken(21.09.2026 um 06:00 Uhr)
Sichere ProgrammierungWhat Is Rowhammer? How Can Repeated Memory Access Flip Bits in RAM?(21.09.2026 um 07:12 Uhr)
Sichere Programmierungnpm publish Ignores .gitignore: The .npmignore Override Rule(21.09.2026 um 07:15 Uhr)
Sichere ProgrammierungAphelion Editor - A free node-based video / VFX editor(21.09.2026 um 07:21 Uhr)
Sichere ProgrammierungGovernance Attack Surface Review: OKX(21.09.2026 um 07:31 Uhr)
Sichere ProgrammierungJSM Portal Request Create Property Panel Submit(21.09.2026 um 07:34 Uhr)
Reverse Engineeringsearch instructions assembly easy (X86,RISCV,AARCH64,etc)(20.09.2026 um 15:44 Uhr)
Intelligence View
⚡ tsecurity.de Intelligence

User Mode Hook Scanner (Alpha)

Reagiere als Erste:r — dein Feedback zählt!
I finally decided to write my first security tool based on an idea I had for advanced hook detection, I couldn't find any evidence of the method being used so I based a tool around it. It's still a working progress but I'm posting so I can get some feedback early on (Currently only x86 systems are supported, but this shouldn't be an issue as most researchers are running 32-bit VMs).
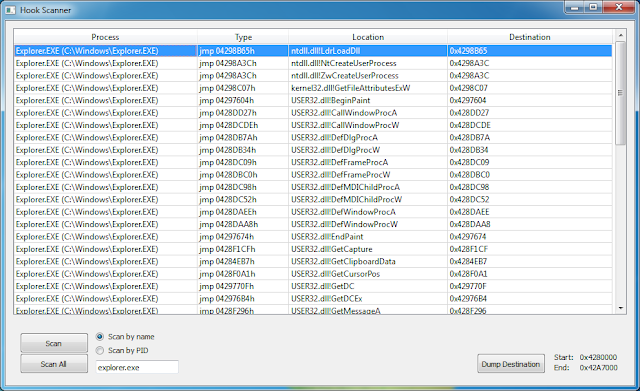


Advanced Scanning

The scanner will iterate the export table for the following system modules: ntdll.dll, kernel32.dll, kernelbase.dll, user32.dll, ws2_32.dll, and wininet.dll. Like a conventional scanner it will go through each instruction of the exported function, comparing it against a clean version of the dll which has been loaded from the disk. Normally at this point a hook scanner would either report the modification or check to see if it's a jump or call, but I've decided to take an extra step towards detecting obscure hooks.

Function Emulation
If any modification is found at any point within the function body, the scanner will use my basic x86 emulator to begin emulating the function, while tracing push, pop, mov, lea, jmp, call, and ret instructions. The emulator will try to determine if control flow is altered by the modified instructions and if so, which instruction redirects execution and to where.

The purpose of the emulator is to detect more obscure hooks as well as accurately determine the destination of the hook, beyond resolving basic jump and call instructions. A good example of where this is applicable is on hooks placed by carberp within the native call stubs of ntdll.

Consider this example call stub:
mov eax, 0xAA
mov edx, 0x7FFE0300
call dword ptr [edx]
retn 0x10
This function does not use a relative call, instead it moves a pointer into the edx register and performs an absolute indirect call with it. Carberp replaces the address moved into the edx register, resulting in redirecting the call to an arbitrary location, and not showing up in hook scanners searching for jmp/call hooks. More advanced hook scanners will log any modifications; however, the user would then have to disassemble the modified function and determine the destination address of the hook, which my engine does automatically (if it fails to resolve the location or detect a control transfer, the modification will still be logged for further investigation).

Destination Dumping

Most rootkits hook by injecting their code (usually shellcode or a PE file) into the target process, hooks are then set to point to locations within the injected code. If the tool is successfully able to work out the destination of a hook, it will query the page it points to and then map out all pages allocated with the same base address. Using this information it is possible to dump the rootkit's entire shellcode, injected PE or DLL, even if it spans multiple pages. 

Conclusion

Again, this is a working progress and I can't guarantee the current version won't be a huge steaming pile of crap. please email any feedback/issues to [email protected] or leave a comment on this post.

Here's a demo video to prove it does at least work on my system:


Download Link: https://www.malwaretech.net/downloads/HookScanner.rar
Ähnliche Beiträge
🔍 Verwandte News

Ähnliche Beiträge zu User Mode Hook Scanner (Alpha)

Thematisch verwandte Begriffe: User, Mode, Hook, Scanner · 6 Treffer

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Zum Aktualisieren ziehen
ZERO-DAY CVE-2026-94111 | Tencent BrowserSkill through 0.3.0 contains an authentication bypass vul…
Advisory →
TTS Reader • tsecurity.de Voice
tsecurity.de Icon
tsecurity.de App
Offline-Lesen, Eilmeldungen & 0ms Ladezeit

Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.

Nächster Beitrag
Themen-Radar & Intelligence Matrix
Echtzeit-Taxonomie nach Angriffsvektoren & Plattformen

tsecurity.de Live Threat Radar

🔴 LIVE RADAR
MONITORING
AKTIV
CVE-DATENBANK
LIVE
🔍
Community Radar & Live Chat
Sentinel Bot online • Live-Stream
Dein Cluster: Security Explorer
Match:
lädt…
Verbindung zum Community-Stream wird aufgebaut...
Bearbeitungsmodus — Senden überschreibt deine Nachricht
Community-Puls — was gerade passiert
lädt…
Aktivitäten deiner Analysten
lädt…
Neues Thema oder Eilmeldung einreichen

Reiche interessante Links, Zero-Days oder Debatten ein. Die Community entscheidet per Upvote über die Veröffentlichung.

Heiß diskutierte Einreichungen
🔖 Gespeicherte Artikel
📂 Keine gespeicherten Artikel vorhanden.
Zurück Ziehen Vor
Links: vorheriger Artikel Rechts: nächster Artikel unten: schließen
News NIS-2 Frühwarnung Tier-1 Intel ⏱️ 3 Min vor 10 Min
Artikeldaten werden geladen...

Zurück: vorheriger Vor: nächster
↗ Original-Quelle
Social Reaktionen Deine Reaktion zählt
Einstufung & Relevanz-Poll 0 Stimmen
In sozialen Netzwerken teilen 1-Klick