
Zum Hauptinhalt springen
Echtzeit-Radar & Feeds
Alle RSS Feeds ➔
👥 Community & Social
YouTube Security VideosGoogle Cloud Tech: Harness engineering and context curation(30.09.2026 um 01:00 Uhr)
•
YouTube Security VideosMicrosoft Developer: Tools your agent can actually trust(30.09.2026 um 00:55 Uhr)
••
Sicherheitslücken (CVE)CVE-2020-9711 | Adobe Acrobat Reader File out-of-bounds (apsb20-48)(30.09.2026 um 01:08 Uhr)
••
Sicherheitslücken (CVE)CVE-2020-9713 | Adobe Acrobat Reader File out-of-bounds (apsb20-48)(30.09.2026 um 01:08 Uhr)
••
Sicherheitslücken (CVE)CVE-2025-64152 | Apache IoTDB up to 1.3.5/2.0.6 path traversal(30.09.2026 um 01:08 Uhr)
•
Sicherheitslücken (CVE)CVE-2025-55017 | Apache IoTDB up to 1.3.5/2.0.5 path traversal(30.09.2026 um 01:08 Uhr)
•
Sichere ProgrammierungWSL2 disk keeps growing? Here's how to shrink it(30.09.2026 um 01:15 Uhr)
•
Intelligence View
⚡ tsecurity.de Intelligence

Bell Canada website hacked with POST-based SQL Injection vulnerability

Few days back, Nullcrew hackers hacked into Bell Canada website and leaked thousands of customer data.Bell Canada confirmed Sunday that usernames and passwords of 22,421 and five valid credit card numbers have been leaked by hackers.  …

0
↗ Quelle (ehackingnews.com)
Reagiere als Erste:r — dein Feedback zählt!
Few days back, Nullcrew hackers hacked into Bell Canada website and leaked thousands of customer data.

Bell Canada confirmed Sunday that usernames and passwords of 22,421 and five valid credit card numbers have been leaked by hackers.  However, the organization points finger at Third-party saying the leak "results from illegal hacking of an Ottawa-based third-party supplier's information technology system".

Bell claims its own network wasn't affected by this breach.  Bell has disabled all passwords and notifying all affected users.  They are currently working with law enforcement and government security officials to investigate the matter.

"Quite a laughable claim, Bell actually knows of the breach, they knew the vulnerable section of the website for two weeks."In a response to the Bell's claim, hackers said in their twitter account.

The screenshot provided to DataBreaches shows that the hackers had a chat with Bell Support team.

Nullcrew chatting with Bell support team

Hackers said a POST based SQL Injection vulnerability resides in the password recovery page of Bell's sub-domain( https://protectionmanagement.bell.ca/passwordrecovery_1.asp)
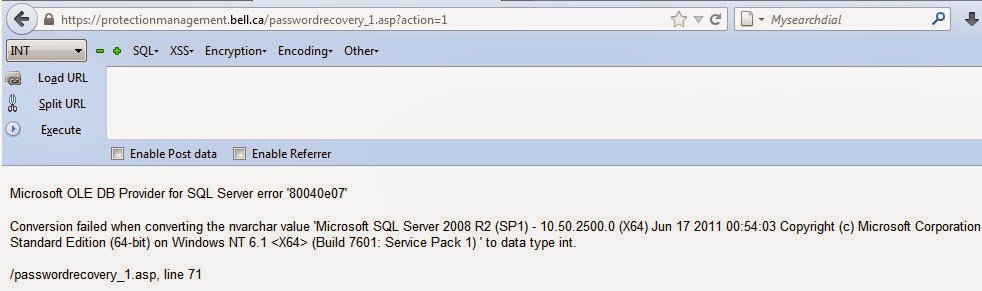
Post-based SQL Injection in Bell Canada

2. Cyber Threat Intelligence & Forensik

CTI Threat Relationship Graph4 Knoten / 3 Relationen
CVE / Incident Software MITRE ATT&CK CWE Weakness IoC
MITRE ATT&CK Matrix Navigator 14 Taktiken
1 belegte TechnikenLive-Mapping
Reconnaissance
Resource Development
Initial Access
Execution
Persistence
Privilege Escalation
Defense Evasion
Credential Access
Discovery
Lateral Movement
Collection
Command and Control
Exfiltration
Impact
Ähnliche Beiträge
🔍 Verwandte News

Auch interessante Nachrichten Bell Canada website hacked with POST-based SQL Injection vulnerability

Thematisch verwandte Begriffe: Bell, Canada, website, hacked · 6 Treffer

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

💬 Kommentare werden geladen…
Zum Aktualisieren ziehen
ZERO-DAY CVE-2026-71189 | An attacker can construct a request that, if issued by another applicati…
Advisory →
tsecurity.de Icon
Offline-Lesen, Eilmeldungen & 0ms Ladezeit

Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.

Nächster Beitrag