
Zum Hauptinhalt springen
Echtzeit-Radar & Feeds
Alle RSS Feeds ➔
👥 Community & Social
YouTube Security VideosNutanix advances legacy and AI app management with AMD(01.10.2026 um 16:00 Uhr)
•
YouTube Security VideosPC-WELT: 32 TB SSD-Speicher in der HMX 6!(01.10.2026 um 16:15 Uhr)
••••
Videos & KonferenzenPC-WELT: 32 TB SSD-Speicher in der HMX 6!(01.10.2026 um 16:15 Uhr)
••
Sicherheitslücken (CVE)USN-8857-1: KCoreAddons vulnerability(01.10.2026 um 12:48 Uhr)
•••
Intelligence View
⚡ tsecurity.de Intelligence

DarkLoadLibrary - LoadLibrary For Offensive Operations

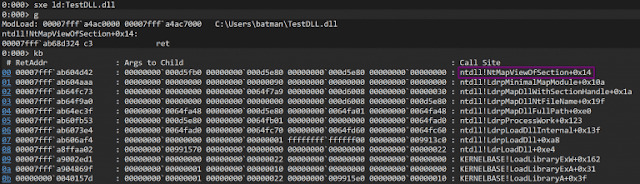
LoadLibrary for offensive operations. How does is work?https://www.mdsec.co.uk/2021/06/bypassing-image-load-kernel-callbacks/UsageDARKMODULE DarkModule =…

Beitrag
0
Seite
0
↗ Quelle (feedproxy.google.com)
Social ReaktionenReagiere als Erste:r — dein Feedback zählt!


LoadLibrary for offensive operations.


How does is work?

https://www.mdsec.co.uk/2021/06/bypassing-image-load-kernel-callbacks/


Usage
DARKMODULE DarkModule = DarkLoadLibrary(
LOAD_LOCAL_FILE, // control flags
L"TestDLL.dll", // local dll path, if loading from disk
NULL, // DLL Buffer to load from if loading from memory
0, // dll size if loading from memory
NULL // dll name if loaded from memory
);

Control Flags:
  • LOAD_LOCAL_FILE - Load a DLL from the file system.
  • LOAD_MEMORY - Load a DLL from a buffer.
  • NO_LINK - Don't link this module to the PEB, just execute it.

DLL Path:

This can be any path that CreateFileW will open.


DLL Buffer:

This argument is only needed when LOAD_MEMORY is set. In that case this argument should be the buffer containing the DLL.


DLL Size:

This argument is only needed when LOAD_MEMORY is set. In that case this argument should be the size of the buffer containing the DLL.


DLL Name:

This argument is only needed when LOAD_MEMORY is set. In that case this argument should be the name which the DLL should be set in the PEB under.


Considerations

The windows loader is very complex and can handle all the edge case's and intricacies of loading DLLs. There are going to be edge case's which I have not had the time to discover, reverse engineer and implement. So there's going to be DLLs that this loader simply will not work with.

That being said I plan on making this loader as complete as possible, so please open issue's for DLLs that are not correctly loaded.


Ähnliche Beiträge
🔍 Verwandte News

Auch interessante Nachrichten DarkLoadLibrary - LoadLibrary For Offensive Operations

Thematisch verwandte Begriffe: DarkLoadLibrary, LoadLibrary, Offensive, Operations · 6 Treffer

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

💬 Kommentare werden geladen…
Zum Aktualisieren ziehen
tsecurity.de Icon
Offline-Lesen, Eilmeldungen & 0ms Ladezeit

Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.

Nächster Beitrag