Zum Hauptinhalt springen
Echtzeit-Radar & Feeds
Alle RSS Feeds ➔
👥 Community & Social
IT Security ToolsHashcatRosetta(02.10.2026 um 19:23 Uhr)
•
IT Security NachrichtenThe legal questions raised by agentic AI hacks(02.10.2026 um 19:47 Uhr)
••
Sicherheitslücken (CVE)FortiMail zero-day exploited in attacks as CISA urges immediate patching(02.10.2026 um 19:28 Uhr)
•
IT Security NachrichtenNew infosec products of the week: October 2, 2026(02.10.2026 um 06:00 Uhr)
•
IT Security NachrichtenAI agents keep access to company data after their work is done(02.10.2026 um 06:30 Uhr)
••
Malware / Trojaner / VirenAndroid 17 makes it harder for spyware to cover its tracks(02.10.2026 um 07:30 Uhr)
•
IT Security NachrichtenCriminal recruiters want people on your payroll(02.10.2026 um 08:00 Uhr)
•
Sicherheitslücken (CVE)Critical FortiMail zero-day exploited in the wild (CVE-2026-104286)(02.10.2026 um 10:50 Uhr)
•
Intelligence View
⚡ tsecurity.de Intelligence

VirusTotal cheat sheet makes it easy to search for specific results
VirusTotal cheat sheet makes it easy to search for specific results Post Views: 1 Premium Content Subscribe to Patreon to watch this episode. Reading Time: 3…

Beitrag
0
Seite
0
↗ Quelle (blackhatethicalhacking.com)
Social ReaktionenReagiere als Erste:r — dein Feedback zählt!


VirusTotal cheat sheet makes it easy to search for specific results


Premium Content


Patreon


Subscribe to Patreon to watch this episode.


Reading Time: 3 Minutes


VirusTotal has published a cheat sheet to help researchers create queries leading to more specific results from the malware intelligence platform.


File search modifiers can assist with refining the output but the cheat sheet shows how they can be combined in real-world scenarios to find particular data.


See Also: So you want to be a hacker?
Complete Offensive Security and Ethical Hacking Course


More targeted searches


In a blog post on Monday, Google security engineer Alexey Firsh provides examples of how the cheat sheet can be used to find files connected to certain entities, groups of activities, documents, networks, and non-Windows malware samples.


Using a specific ‘entity’ search modifier, analysts can look for files according to IP addresses, domains, URLs, or files. The plan is to also include VirusTotal collections in this collection of modifiers.
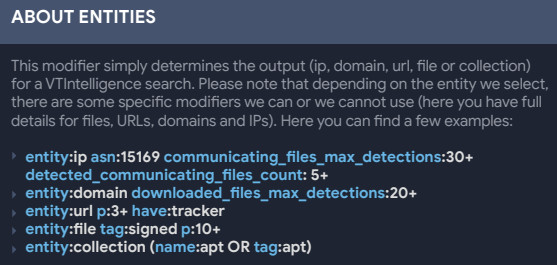


VirusTotal modifiers for entity search
VirusTotal cheat sheet – modifiers for ‘entity’ search


To help researchers follow the tracks of a threat actor, Firsh notes that researchers can combine the name of the malware family or the campaign with the verdict of antivirus engines on VirusTotal.


This method is well-suited for detecting advanced attackers and would uncover related data in collections curated by various users of the VirusTotal platform.
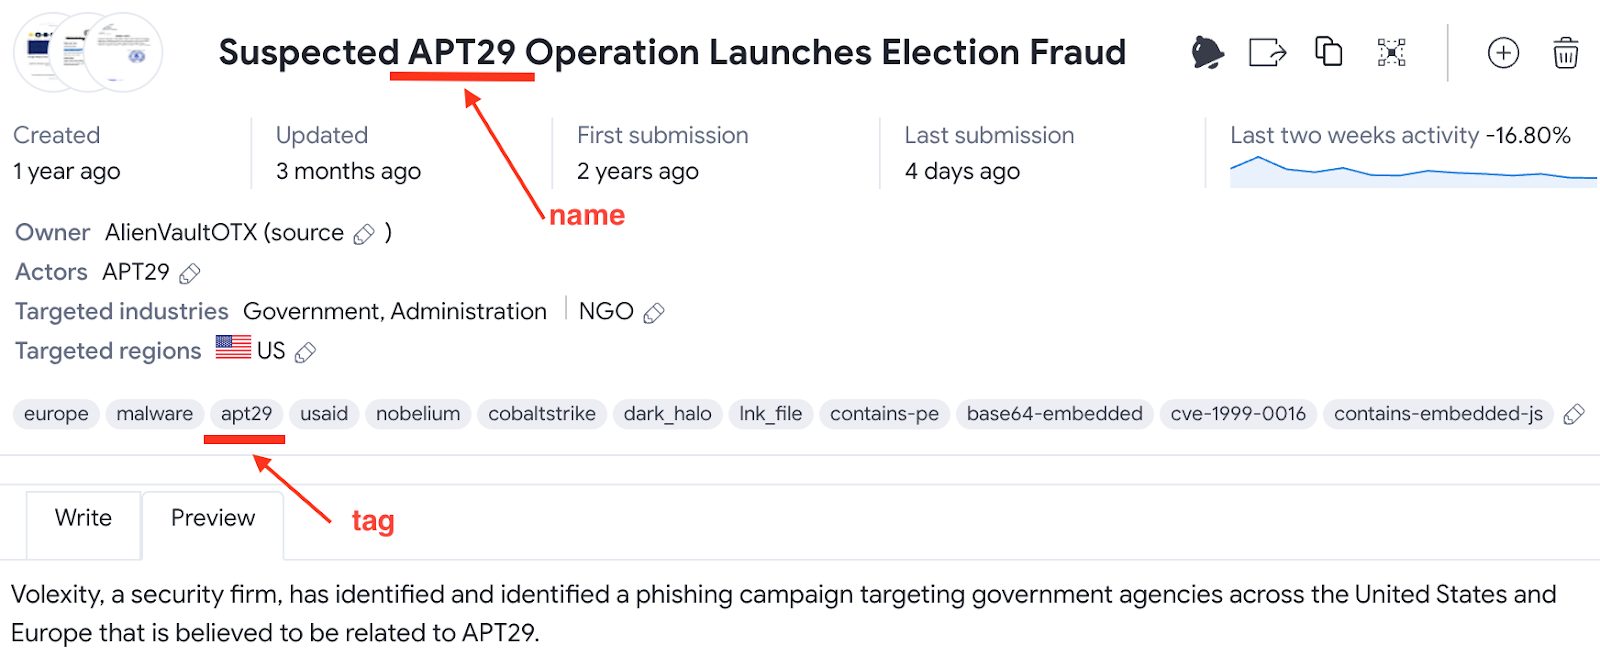


VirusTotal cheat sheet - finding specific group activities
VirusTotal cheat sheet – finding specific group activities


The search can be narrowed down or mixed with queries based on crowdsourced rules (YARA, IDS, Sigma).
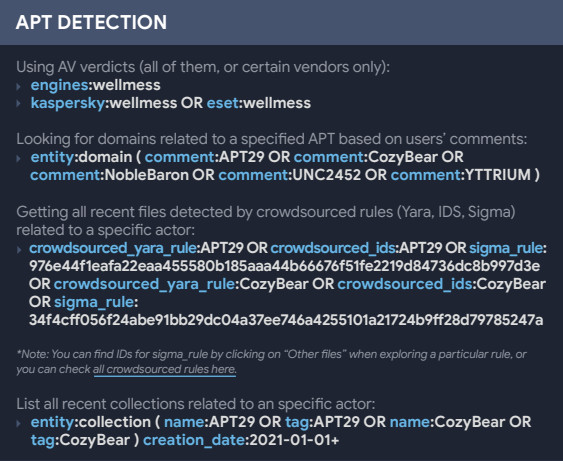


VirusTotal cheat sheet - detecting APT activity
VirusTotal cheat sheet – detecting APT activity


VirusTotal’s cheat sheet covers examples of real-life cases where file search modifiers filter data signed by specific vendors and emails from a certain server that have an attachment or not.


Researchers can also use keywords that allow finding files for other operating systems than Windows, like Android, macOS, and Symbian.


For Android, the samples are processed using the open-source Androguard tool for looking inside the packages, including code strings, manifest entities, and certificate signatures.


A relatively new feature is looking for explicit package names. However, this works only with files indexed starting March 2022.


VirusTotal’s cheat sheet (PDF) is just three pages at the moment but it packs multiple categories of keyword combinations to find malicious or suspicious files.


It can also be a shortcut to link malware to operations from known and unknown actors or to uncover new and lurking threats.


VirusTotal plans to update the cheat sheet with fresh options that would make searching intelligence on the platform easier, quicker, and more targeted.


Are u a security researcher? Or a company that writes articles or write ups about Cyber Security, Offensive Security (related to information security in general) that match with our specific audience and is worth sharing?


If you want to express your idea in an article contact us here for a quote: [email protected]


Source: bleepingcomputer.com


Source Link


Merch


The post VirusTotal cheat sheet makes it easy to search for specific results first appeared on Black Hat Ethical Hacking.
🔍 CTI & Forensik

Cyber Threat Intelligence & Forensik

ATT&CK-Navigator · IoC-Radar · Exploit-Belege
MITRE ATT&CK Matrix Navigator
Enterprise-Matrix · nur belegte Techniken
14 Taktiken
2 belegte Techniken
T1486TA0040 · Impact
Data Encrypted for Impact
Mitigation: M1053 Data Backup & Offline Isolation
Quelle: Kontext-Klassifikation des Artikeltextes
T1190TA0001 · Initial Access
Exploit Public-Facing Application
Mitigation: M1042 Network Segmentation & WAF Rule Enforcement
Quelle: Kontext-Klassifikation des Artikeltextes
Reconnaissance
Resource Development
Initial Access
Execution
Persistence
Privilege Escalation
Defense Evasion
Credential Access
Discovery
Lateral Movement
Collection
Command and Control
Exfiltration
Impact
CTI Threat Relationship Graph
Akteure · Techniken · Beziehungen
7 Knoten · 6 Relationen
CVE / Incident Threat Actor Software MITRE ATT&CK CWE Weakness IoC
Ähnliche Beiträge
🔍 Verwandte News

Auch interessante Nachrichten VirusTotal cheat sheet makes it easy to search for specific results

Thematisch verwandte Begriffe: VirusTotal, cheat, sheet, makes · 6 Treffer

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

💬 Kommentare werden geladen…
Zum Aktualisieren ziehen
tsecurity.de Icon
Offline-Lesen, Eilmeldungen & 0ms Ladezeit

Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.

Nächster Beitrag