Zum Hauptinhalt springen
tsecurity.de LIVE
Echtzeit-Radar & Feeds
Alle RSS Feeds
👥 Community & Social
Intelligence View
⚡ tsecurity.de Intelligence

Mandiant’s Twitter Account Hijacked in Cryptocurrency Scam
Mandiant’s Twitter Account Hijacked in Cryptocurrency Scam Post Views: 2 …

0
↗ Quelle (blackhatethicalhacking.com)
Reagiere als Erste:r — dein Feedback zählt!


Mandiant’s Twitter Account Hijacked in Cryptocurrency Scam


Join our Patreon Channel and Gain access to 70+ Exclusive Walkthrough Videos.


Patreon


Reading Time: 3 Minutes


The Twitter account of Mandiant, an American cybersecurity firm and Google subsidiary, was hijacked earlier today to promote a cryptocurrency scam impersonating the Phantom crypto wallet.


A spokesperson for Mandiant informed BleepingComputer that they are aware of the incident and are actively working to resolve the issue.


Upon gaining control, the attacker renamed the account to @phantomsolw and used it to promote a fraudulent website posing as the Phantom crypto wallet. The website claimed to offer free $PHNTM tokens as part of an airdrop.
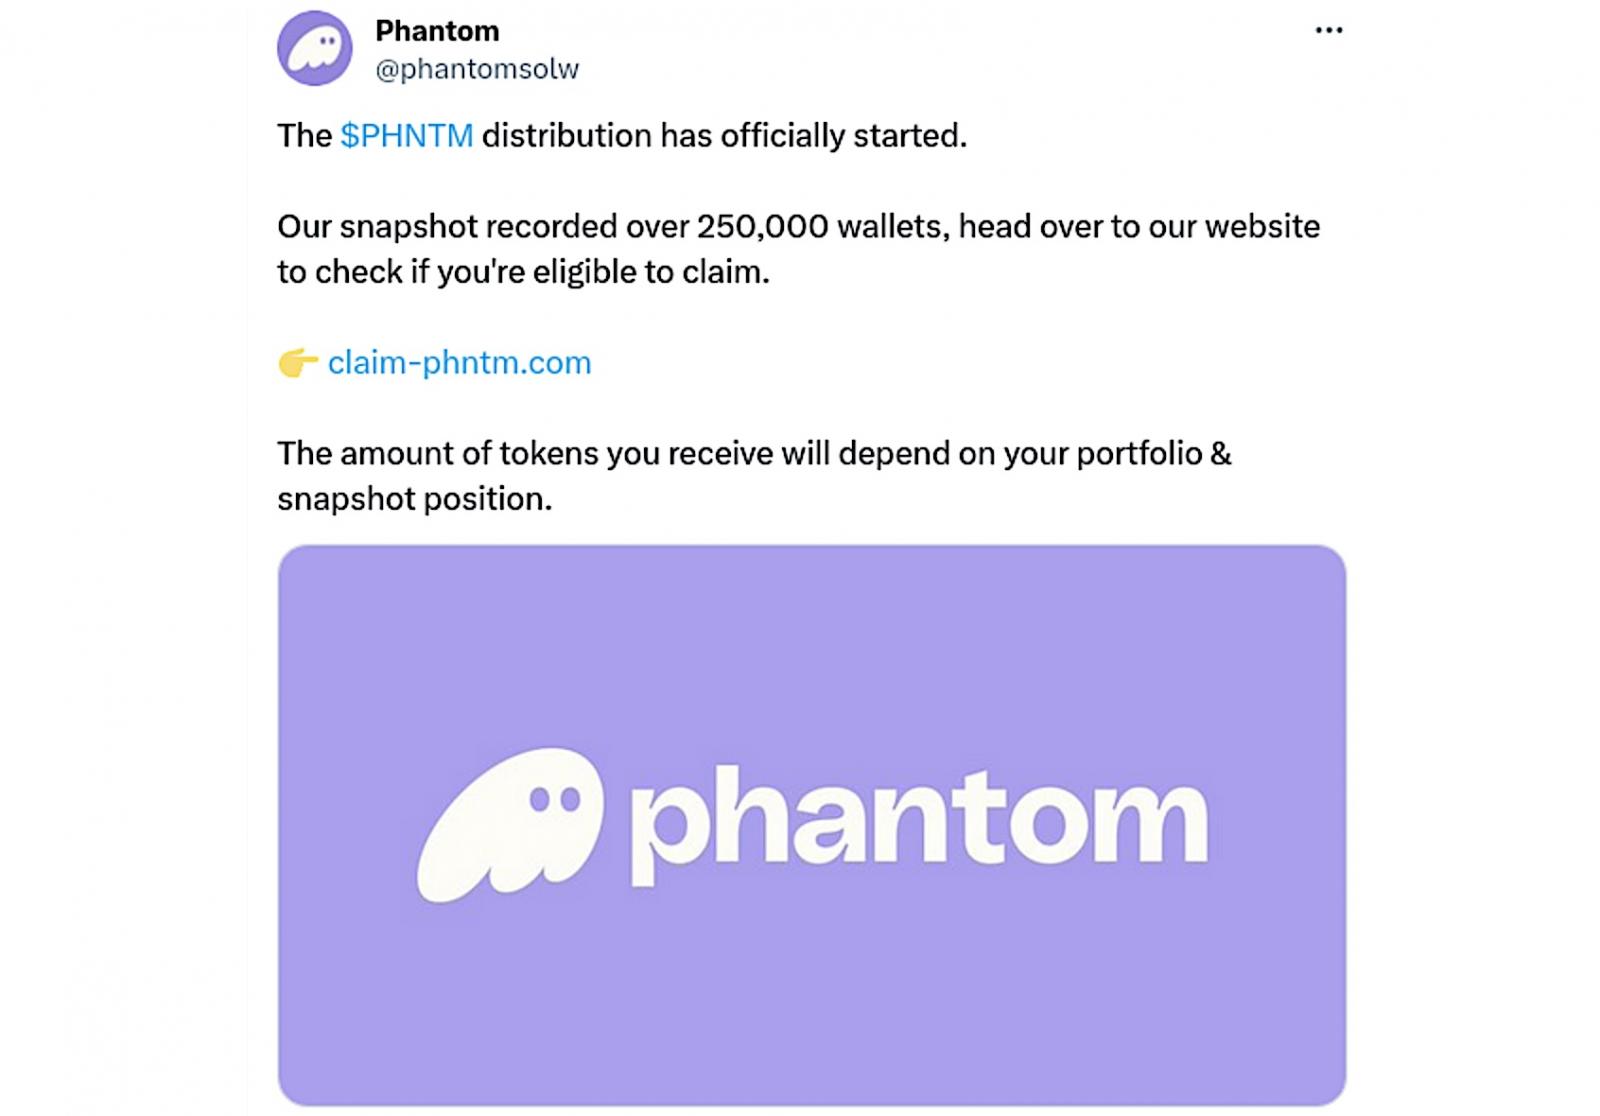


Mandiant crypto-scam tweet


Crypto-scam tweet (MalwareHunterTeam)


See Also: So, you want to be a hacker?

Offensive Security, Bug Bounty Courses


Discover your weakest link. Be proactive, not reactive. Cybercriminals need just one flaw to strike.


BleepingComputer conducted tests and found that clicking the ‘Claim Airdrop’ button on the fake website, without having the Phantom wallet installed, redirected users to the legitimate site, where they were prompted to install it. Once installed, the fake wallet attempted to drain the targets’ cryptocurrency wallets.
However, the legitimate Phantom Wallet issued a warning, labeling the scam website as malicious and unsafe.


The threat actor behind the attack has since deleted the scam tweet and is now using the account to taunt Mandiant. The original Mandiant Twitter handle, @mandiant, currently displays an error message stating, “This account doesn’t exist. Try searching for another.”
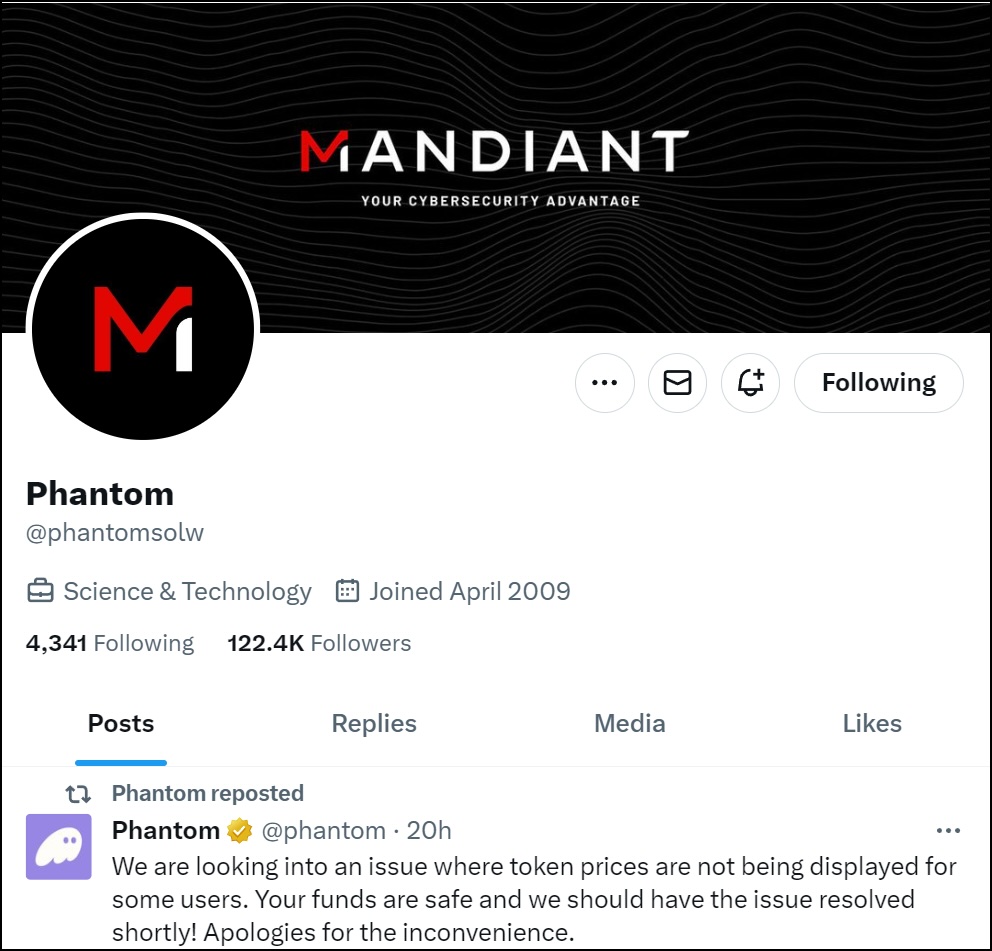


Hijacked Mandiant Twitter account


In an update, Mandiant informed BleepingComputer that they have regained control of the account and are working on restoring it.

However, due to Twitter restrictions on changing names too often, the username is still renamed to ‘@phantomsolw’ at the time of this update.


Are u a security researcher? Or a company that writes articles or write ups about Cyber Security, Offensive Security (related to information security in general) that match with our specific audience and is worth sharing?


If you want to express your idea in an article contact us here for a quote: [email protected]


Source: bleepingcomputer.com


Source Link


Merch


Offensive Security & Ethical Hacking Course


Begin the learning curve of hacking now!


Information Security Solutions


Find out how Pentesting Services can help you.


Join our Community


The post Mandiant’s Twitter Account Hijacked in Cryptocurrency Scam first appeared on Black Hat Ethical Hacking.
Ähnliche Beiträge
🔍 Verwandte News

Auch interessante Nachrichten Mandiant’s Twitter Account Hijacked in Cryptocurrency Scam

Thematisch verwandte Begriffe: Mandiants, Twitter, Account, Hijacked · 6 Treffer

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Zum Aktualisieren ziehen
ZERO-DAY Kritische Sicherheitsmeldung
Advisory →
TTS Reader • tsecurity.de Voice
tsecurity.de Icon
tsecurity.de App
Offline-Lesen, Eilmeldungen & 0ms Ladezeit

Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.

Nächster Beitrag
Themen-Radar & Intelligence Matrix
Echtzeit-Taxonomie nach Angriffsvektoren & Plattformen

tsecurity.de Live Threat Radar

🔴 LIVE RADAR
MONITORING
AKTIV
CVE-DATENBANK
LIVE
🔍
Community Radar & Live Chat
Sentinel Bot online • Live-Stream
Dein Cluster: Security Explorer
Match:
lädt…
Verbindung zum Community-Stream wird aufgebaut...
Bearbeitungsmodus — Senden überschreibt deine Nachricht
Community-Puls — was gerade passiert
lädt…
Aktivitäten deiner Analysten
lädt…
Neues Thema oder Eilmeldung einreichen

Reiche interessante Links, Zero-Days oder Debatten ein. Die Community entscheidet per Upvote über die Veröffentlichung.

Heiß diskutierte Einreichungen
🔖 Gespeicherte Artikel
📂 Keine gespeicherten Artikel vorhanden.
Zurück Ziehen Vor
Links: vorheriger Artikel Rechts: nächster Artikel unten: schließen
News NIS-2 Frühwarnung Tier-1 Intel ⏱️ 3 Min vor 10 Min
Artikeldaten werden geladen...

Zurück: vorheriger Vor: nächster
↗ Original-Quelle
Social Reaktionen Deine Reaktion zählt
Einstufung & Relevanz-Poll 0 Stimmen
In sozialen Netzwerken teilen 1-Klick