Outlook – Microsoft Patches Critical Flaw Leaking NTLM Passwords
Join our
A recently addressed security flaw in Microsoft Outlook posed a potential risk of unauthorized access to NT LAN Manager (NTLM) v2 hashed passwords. Tracked as CVE-2023-35636 with a CVSS score of 6.5, Microsoft resolved the issue as part of its December 2023 Patch Tuesday updates.
Exploitation of this vulnerability involves the calendar-sharing function in Outlook. In a scenario where an attacker could convince a user to open a specifically crafted file, the flaw could be triggered, potentially exposing NTLM v2 hashed passwords. This could occur through phishing emails containing malicious links or deceptive instant messages.
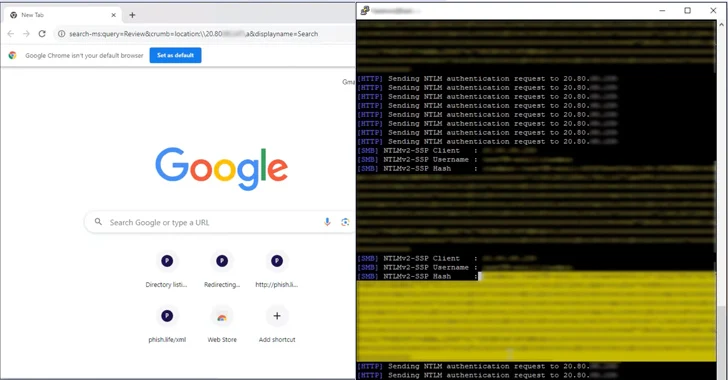
varonis.com
The vulnerability,
Discover your weakest link. Be proactive, not reactive. Cybercriminals need just one flaw to strike.
Trending:
Are u a security researcher? Or a company that writes articles or write ups about Cyber Security, Offensive Security (related to information security in general) that match with our specific audience and is worth sharing?
If you want to express your idea in an article contact us here for a quote: [email protected]
Source: thehackernews.com
Community-Analysen & Experten-Meinungen 0
Verwandte Story-Cluster & Quellen (Vektor-KI)
 Ähnliche Beiträge
Auch interessante Nachrichten Outlook – Microsoft Patches Critical Flaw Leaking NTLM Passwords
Thematisch verwandte Begriffe: Outlook, Microsoft, Patches, Critical · 6 Treffer
Protect Kubernetes Services with OAuth2 Proxy, Gateway API, Traefik, and Pocket ID
The best n8n fix I found this month was boring: lower your agent concurrency settings before touching the prompt
President Trump Called Nvidia’s Jensen Huang About A.I. Slowdown
N.Y.C. Council Members Call for More Restrictions on Tech in Schools
Videos werden geladen ...
Beiträge werden geladen ...
Videos werden geladen ...
Beiträge werden geladen ...
Videos werden geladen ...
Beiträge werden geladen ...
Videos werden geladen ...
Beiträge werden geladen ...
Videos werden geladen ...
🔖 Gespeicherte Artikel
tsecurity.de App
Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.
Community Radar & Live Chat
Aktivitäten deiner Analysten
Neues Thema oder Eilmeldung einreichen
Reiche interessante Links, Zero-Days oder Debatten ein. Die Community entscheidet per Upvote über die Veröffentlichung.
SOCIAL SHARE CARD GENERATOR