Zum Hauptinhalt springen
Echtzeit-Radar & Feeds
Alle RSS Feeds ➔
👥 Community & Social
••
IT Security NachrichtenStop Talking About A.I. Like a Human(01.10.2026 um 11:01 Uhr)
•
IT Security NachrichtenQueensland Cybersecurity Department Loses $809,000 in Cyberattack(01.10.2026 um 11:00 Uhr)
•
IT Security NachrichtenEurope’s Police Chiefs Face Growing Threat of AI-Driven Crime(01.10.2026 um 11:01 Uhr)
••
IT Security NachrichtenWhy AI agents are like the dog that pushed kids into the Seine(01.10.2026 um 11:00 Uhr)
••••••
IT Security NachrichtenStop Talking About A.I. Like a Human(01.10.2026 um 11:01 Uhr)
•
IT Security NachrichtenQueensland Cybersecurity Department Loses $809,000 in Cyberattack(01.10.2026 um 11:00 Uhr)
•
IT Security NachrichtenEurope’s Police Chiefs Face Growing Threat of AI-Driven Crime(01.10.2026 um 11:01 Uhr)
••
IT Security NachrichtenWhy AI agents are like the dog that pushed kids into the Seine(01.10.2026 um 11:00 Uhr)
••••
Intelligence View
⚡ tsecurity.de Intelligence

Darcula: The New Phishing-as-a-Service Targeting Android and iPhone Users Worldwide

Darcula: The New Phishing-as-a-Service Targeting Android and iPhone Users Worldwide Post Views: 42 Join our Patreon Channel and Gain access to 70+ Exclusive…

Beitrag
0
Seite
0
↗ Quelle (blackhatethicalhacking.com)
Social ReaktionenReagiere als Erste:r — dein Feedback zählt!


Darcula: The New Phishing-as-a-Service Targeting Android and iPhone Users Worldwide


Join our Patreon Channel and Gain access to 70+ Exclusive Walkthrough Videos.


Patreon


Reading Time: 3 Minutes


A sophisticated phishing-as-a-service (PhaaS) operation dubbed ‘Darcula’ has emerged, utilizing over 20,000 domains to impersonate brands and extract credentials from Android and iPhone users across more than 100 countries.


Darcula’s reach extends across various sectors, from postal and financial services to government agencies and telecommunications providers, offering cybercriminals a selection of over 200 templates for their fraudulent activities.
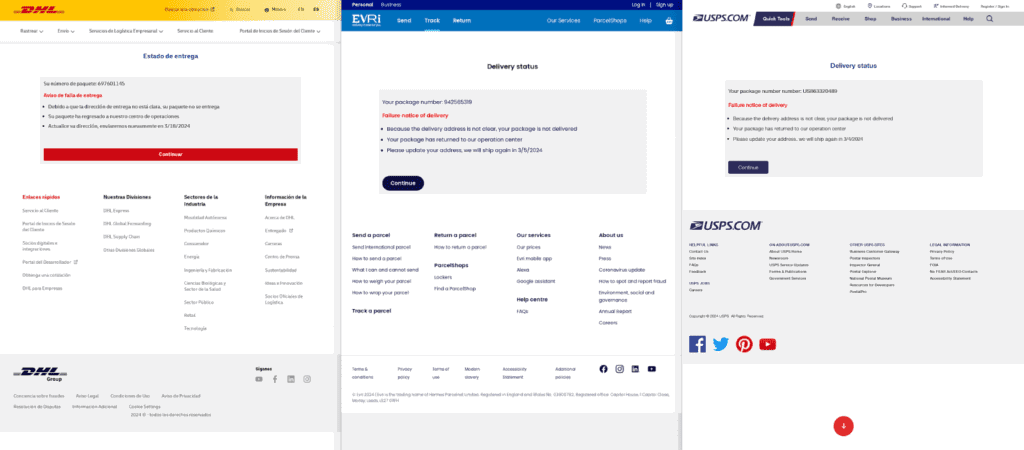

Landing pages available in the Darcula kitLanding pages available in the Darcula kit (Netcraft)


What sets Darcula apart is its utilization of the Rich Communication Services (RCS) protocol, employed by Google Messages, and iMessage instead of traditional SMS for delivering phishing messages to targets.


Initially brought to light by security researcher Oshri Kalfon last summer, Darcula has gained traction in the cybercrime community, being implicated in several notable phishing incidents, including scams affecting users in the UK and package fraud schemes mimicking the United States Postal Service (USPS).


See Also: So, you want to be a hacker?

Offensive Security, Bug Bounty Courses


Unlike conventional phishing methods, Darcula leverages modern technologies like JavaScript, React, Docker, and Harbor, allowing for seamless updates and feature enhancements without the need for clients to reinstall phishing kits.


Featuring 200 phishing templates localized for various countries, Darcula’s landing pages are meticulously crafted, incorporating authentic language, logos, and content tailored to specific regions.


The platform streamlines the setup process for fraudsters, enabling them to select a brand to impersonate and deploy the corresponding phishing site and management dashboard within a Docker environment.


Darcula primarily utilizes “.top” and “.com” top-level domains for hosting its purpose-registered domains, with approximately one-third of these domains being supported by Cloudflare.


In a departure from SMS-based tactics, Darcula leverages RCS (Android) and iMessage (iOS) to deliver phishing messages to victims, capitalizing on the perceived legitimacy and enhanced security features offered by these protocols.


RCS message sent from DarculaRCS message sent from Darcula (Netcraft)


2. Cyber Threat Intelligence & Forensik

CTI Threat Relationship Graph4 Knoten / 3 Relationen
CVE / Incident Software MITRE ATT&CK CWE Weakness IoC
MITRE ATT&CK Matrix Navigator 14 Taktiken
1 belegte TechnikenLive-Mapping
Reconnaissance
Resource Development
Initial Access
Execution
Persistence
Privilege Escalation
Defense Evasion
Credential Access
Discovery
Lateral Movement
Collection
Command and Control
Exfiltration
Impact
Ähnliche Beiträge
🔍 Verwandte News

Auch interessante Nachrichten Darcula: The New Phishing-as-a-Service Targeting Android and iPhone Users Worldwide

Thematisch verwandte Begriffe: Darcula, PhishingasaService, Targeting, Android · 6 Treffer

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

💬 Kommentare werden geladen…
Zum Aktualisieren ziehen
tsecurity.de Icon
Offline-Lesen, Eilmeldungen & 0ms Ladezeit

Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.

Nächster Beitrag