
Zum Hauptinhalt springen
tsecurity.de LIVE
Echtzeit-Radar & Feeds
Alle RSS Feeds
👥 Community & Social
Sichere Programmierung(d+019) OpenGL(20.09.2026 um 15:51 Uhr)
Sichere ProgrammierungYou Released an App. Now What?(20.09.2026 um 15:52 Uhr)
Sichere Programmierung(d+023) Triangle(20.09.2026 um 15:53 Uhr)
Sichere ProgrammierungHow many coding agents are you using for the same project?(20.09.2026 um 15:57 Uhr)
Sichere ProgrammierungCapyToolkit: 45+ free browser tools, each with a how-to guide(20.09.2026 um 16:00 Uhr)
Sichere ProgrammierungDay-01: Starting My Cybersecurity Journey(20.09.2026 um 16:02 Uhr)
Sichere ProgrammierungWhat crt.sh's Error Pages Taught Me About Retry Logic(20.09.2026 um 16:03 Uhr)
Sichere ProgrammierungI taught my shell to stop me *before* I run `rm -rf /`(20.09.2026 um 16:09 Uhr)
Sichere ProgrammierungTraditional Coding vs Agentic Coding: The Flow State Problem(20.09.2026 um 16:19 Uhr)
Sichere Programmierung(d+019) OpenGL(20.09.2026 um 15:51 Uhr)
Sichere ProgrammierungYou Released an App. Now What?(20.09.2026 um 15:52 Uhr)
Sichere Programmierung(d+023) Triangle(20.09.2026 um 15:53 Uhr)
Sichere ProgrammierungHow many coding agents are you using for the same project?(20.09.2026 um 15:57 Uhr)
Sichere ProgrammierungCapyToolkit: 45+ free browser tools, each with a how-to guide(20.09.2026 um 16:00 Uhr)
Sichere ProgrammierungDay-01: Starting My Cybersecurity Journey(20.09.2026 um 16:02 Uhr)
Sichere ProgrammierungWhat crt.sh's Error Pages Taught Me About Retry Logic(20.09.2026 um 16:03 Uhr)
Sichere ProgrammierungI taught my shell to stop me *before* I run `rm -rf /`(20.09.2026 um 16:09 Uhr)
Sichere ProgrammierungTraditional Coding vs Agentic Coding: The Flow State Problem(20.09.2026 um 16:19 Uhr)
Intelligence View
⚡ tsecurity.de Intelligence

SQL Injection (SQLi) Vulnerabilities in WordPress: Prevention Tips

Reagiere als Erste:r — dein Feedback zählt!

Understanding SQL Injection (SQLi) in WordPress and How to Protect Your Site

SQL Injection (SQLi) remains a common security vulnerability that allows attackers to manipulate databases by injecting malicious SQL queries. For WordPress sites, SQLi is especially concerning as it can lead to unauthorized access to sensitive data. In this guide, we’ll walk through the basics of SQL Injection, how it affects WordPress and practical ways to protect your site.

SQL Injection (SQLi) Vulnerabilities in WordPress: Prevention Tips

What is SQL Injection in WordPress?

In simple terms, SQL Injection occurs when an attacker is able to insert or "inject" SQL code into a query, potentially giving them access to the database. In WordPress, this is particularly dangerous as attackers could gain access to user data, modify content, or even take full control of the site.

Real-World Example of SQL Injection Attack in WordPress

Imagine a WordPress contact form where users enter information to be stored in the database. If the form isn’t properly validated, a malicious user could input SQL commands rather than normal data, executing unintended actions in the database.

How to Identify SQLi Vulnerabilities in WordPress

Check Forms and Input Fields: SQLi attacks often exploit forms, login fields, and search boxes.
Use Security Plugins: WordPress offers a range of security plugins that scan for vulnerabilities, including SQL Injection.
Run Automated Security Checks: Our free tool, Website Security Checker, allows you to identify SQL Injection and other vulnerabilities effortlessly.
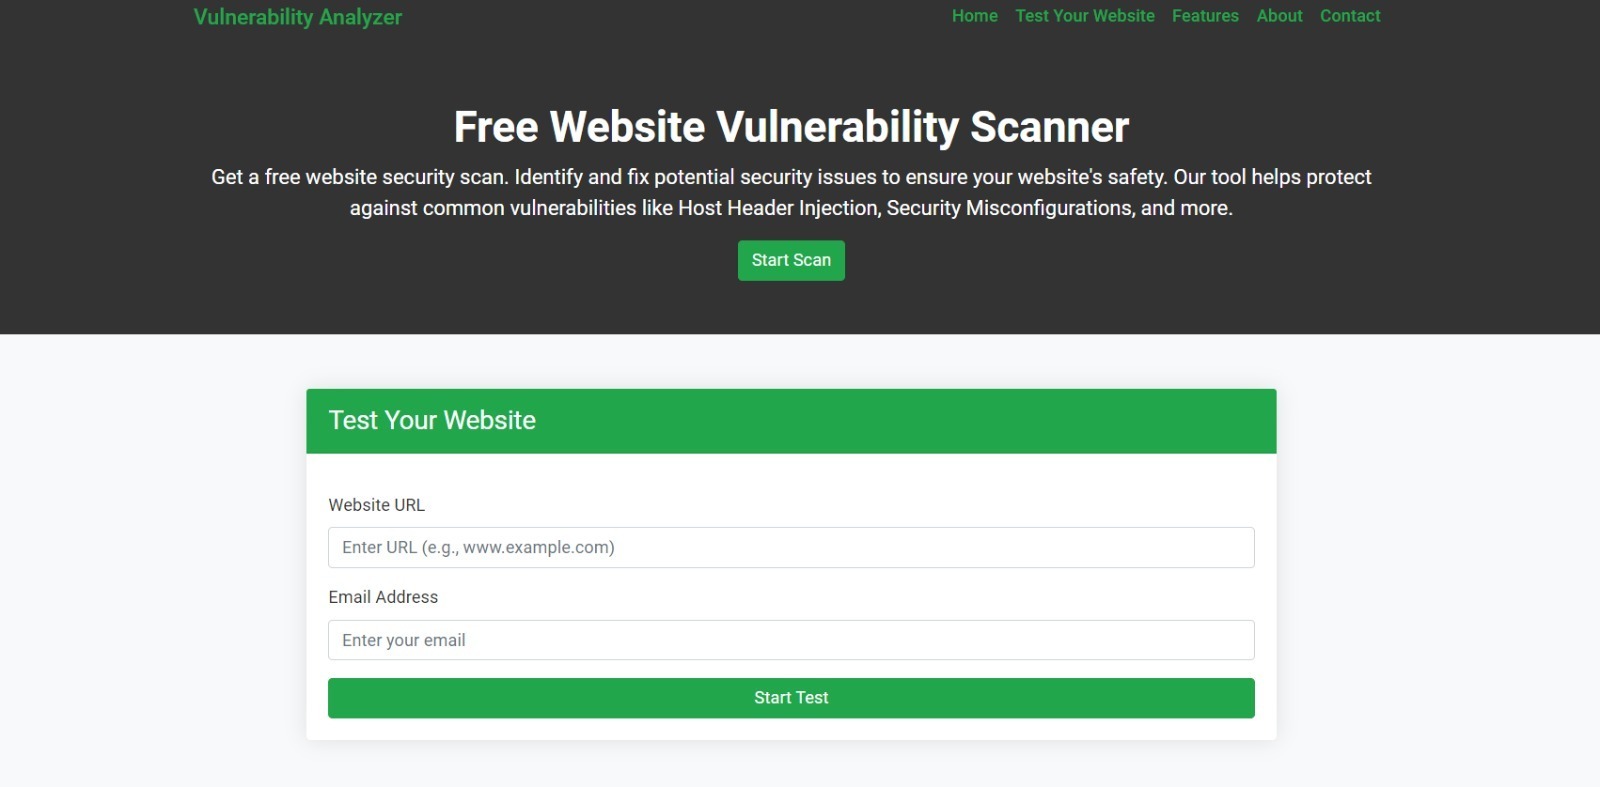
![Screenshot of the Website Security Checker tool homepage at https://free.pentesttesting.com/](https://dev-to-uploads.s3.amazonaws.com/uploads/articles/t467ehklch4mmy13xvvq.jpeg)

This tool helps check your site for SQLi and other security risks.

Example of Code Vulnerable to SQL Injection in WordPress

php
// Vulnerable code
$user_id = $_GET['user_id'];
$result = $wpdb->get_results("SELECT * FROM wp_users WHERE ID = $user_id");
The code above is vulnerable to SQL Injection as it directly uses user input in an SQL query without proper validation or sanitization.

Safe Code with Prepared Statements
To prevent SQLi, always use prepared statements:

php
// Secure code
$user_id = $_GET['user_id'];
$result = $wpdb->get_results($wpdb->prepare("SELECT * FROM wp_users WHERE ID = %d", $user_id));
By using $wpdb->prepare(), you ensure that the input is sanitized, mitigating SQLi risks.

Additional Steps to Secure WordPress Against SQL Injection

Update Regularly: Keep your WordPress version, themes, and plugins updated.
Limit User Permissions: Restrict database access only to essential users.
Use a Web Application Firewall (WAF): This adds an extra layer of protection by filtering malicious traffic.

Screenshot of a vulnerability assessment report generated by our free tool, showing potential SQL Injection risks identified.

Why Regular Security Audits Matter

SQL Injection attacks can be devastating, compromising data and site functionality. Regularly using tools like the Website Security Checker can help you stay proactive and identify vulnerabilities before attackers do.

Conclusion

Protecting your WordPress site from SQL Injection vulnerabilities is crucial. With the right coding practices, security plugins, and regular use of security check tools, you can significantly reduce the risk of SQL Injection. Start by scanning your site today with our free Website Security Checker to spot and fix any existing vulnerabilities.

Ähnliche Beiträge
🔍 Verwandte News

Auch interessante Nachrichten SQL Injection (SQLi) Vulnerabilities in WordPress: Prevention Tips

Thematisch verwandte Begriffe: Injection, SQLi, Vulnerabilities, WordPress · 6 Treffer

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Zum Aktualisieren ziehen
ZERO-DAY CVE-2026-93956 | A flaw has been found in olivier-ls PHP-FTS up to 1.1.2. Affected by thi…
Advisory →
TTS Reader • tsecurity.de Voice
tsecurity.de Icon
tsecurity.de App
Offline-Lesen, Eilmeldungen & 0ms Ladezeit

Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.

Nächster Beitrag
Themen-Radar & Intelligence Matrix
Echtzeit-Taxonomie nach Angriffsvektoren & Plattformen
Community Radar & Live Chat
Sentinel Bot online • Live-Stream
Dein Cluster: Security Explorer
Match:
lädt…
Verbindung zum Community-Stream wird aufgebaut...
Bearbeitungsmodus — Senden überschreibt deine Nachricht
Community-Puls — was gerade passiert
lädt…
Aktivitäten deiner Analysten
lädt…
Neues Thema oder Eilmeldung einreichen

Reiche interessante Links, Zero-Days oder Debatten ein. Die Community entscheidet per Upvote über die Veröffentlichung.

Heiß diskutierte Einreichungen
🔖 Gespeicherte Artikel
📂 Keine gespeicherten Artikel vorhanden.
Zurück Ziehen Vor
Links: vorheriger Artikel Rechts: nächster Artikel unten: schließen
News NIS-2 Frühwarnung Tier-1 Intel ⏱️ 3 Min vor 10 Min
Artikeldaten werden geladen...

Zurück: vorheriger Vor: nächster
↗ Original-Quelle
Social Reaktionen Deine Reaktion zählt
Einstufung & Relevanz-Poll 0 Stimmen
In sozialen Netzwerken teilen 1-Klick