



Terraform State Isolation: Workspace
Isolating state files ensures that changes to one part of your infrastructure does not affect another. Terraform offers two primary methods for state isolation: Layout-based Isolation and Workspace-based Isolation. In this blog post, we’ll focus on Workspace-based Isolation, providing examples to demonstrate its capabilities.
Why Is State Isolation Important?
Terraform uses a state file to track the real-world infrastructure it manages. Sharing a single state file across unrelated resources or environments can lead to issues such as:
Accidental Changes: Modifying unrelated infrastructure when applying changes.
Concurrency Issues: Overwriting state files when multiple users or automation pipelines work simultaneously.
Poor Separation of Concerns: Difficulty managing environments like development, staging, and production.
State isolation avoids these problems by segmenting state files for different components or environments.
Workspace-Based Isolation
Workspaces allow Terraform to maintain multiple state files for a single configuration by associating each workspace with its own state.

Example: Single Configuration with Workspaces
terraform_job/

└── main.tf
main.tf:
provider "aws" {

 region = "us-east-1"

}


resource "aws_s3_bucket" "terraform_state" {

 bucket = "otu-bucket-state"

 # Prevent accidental deletion of this S3 bucket

 lifecycle {

 prevent_destroy = false

 }

}


# Enable versioning so you can see the full revision history of your

# state files

resource "aws_s3_bucket_versioning" "enabled" {

 bucket = aws_s3_bucket.terraform_state.id

 versioning_configuration {

 status = "Enabled"

 }

}


# Enable server-side encryption by default

resource "aws_s3_bucket_server_side_encryption_configuration" "default" {

 bucket = aws_s3_bucket.terraform_state.id

 rule {

 apply_server_side_encryption_by_default {

 sse_algorithm = "AES256"

 }

 }

}


# Explicitly block all public access to the S3 bucket

resource "aws_s3_bucket_public_access_block" "public_access" {

 bucket = aws_s3_bucket.terraform_state.id

 block_public_acls = true

 block_public_policy = true

 ignore_public_acls = true

 restrict_public_buckets = true

}


resource "aws_dynamodb_table" "terraform_locks" {

 name = "state-lock"

 billing_mode = "PAY_PER_REQUEST"

 hash_key = "LockID"

 attribute {

 name = "LockID"

 type = "S"

 }

}

terraform {

 backend "s3" {

 # Replace this with your bucket name!

 bucket = "otu-bucket-state"

 key = "workspaces-example/terraform.tfstate"

 region = "us-east-1"

 # Replace this with your DynamoDB table name!

 dynamodb_table = "state-lock"

 encrypt = true

 }

}


output "s3_bucket_arn" {

 value = aws_s3_bucket.terraform_state.arn

 description = "The ARN of the S3 bucket"

}

output "dynamodb_table_name" {

 value = aws_dynamodb_table.terraform_locks.name

 description = "The name of the DynamoDB table"

}

resource "aws_instance" "example" {

ami = "ami-0e86e20dae9224db8"

instance_type = "t2.micro"

}
Managing Workspaces
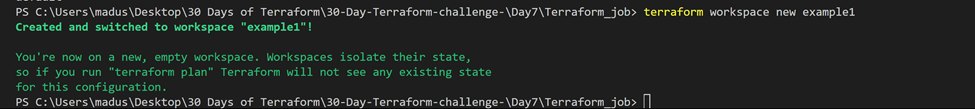
You can create and switch between workspaces using Terraform commands:
# Create workspaces
terraform workspace new example1
terraform workspace new example2
# Switch to a workspace
terraform workspace select example1
# Apply changes to the current workspace
terraform apply
Terraform creates a new EC2 instance different from the one in the default namespace because the state files in each workspace are isolated from one another. Since we’re now in the example1 workspace, Terraform will only make use of the state file from the example1 workspace. and doesn't recognize that the EC2 instance has already been created in the default workspace.

In this example:
- The
example1workspace uses the state fileexample1/terraform.tfstate. - The
example2workspace uses the state fileexample2/terraform.tfstate.

Clean Up
To avoid unnecessary charges, delete the bucket by destroying the infrastructure:
terraform destroy
Type yes when prompted.
Advantages of Workspace-Based Isolation
Single Configuration: Simplifies management by keeping configurations centralized.
Dynamic Backend Configurations: Automatically handles state files based on the active workspace.
Environment-Specific Variables: Easily manage variables unique to each environment using workspace-specific settings.
Challenges of Workspace-Based Isolation
Workspace Context: Requires users to verify the active workspace before applying changes to avoid accidental updates.
Limited Use Cases: Workspaces are less suited for isolating completely unrelated infrastructure components.
Best Practices for Using Workspaces
Set Clear Naming Conventions: Use consistent naming for workspaces (e.g.,dev,staging,prod) to avoid confusion.
Leverage Variables: Use workspace names in variable definitions to manage environment-specific configurations dynamically.
Automate Workspace Selection: Use scripts or CI/CD pipelines to automate workspace selection for specific environments.
Monitor State Files: Ensure that state files for each workspace are regularly backed up and monitored for concurrency issues.
When to Use Workspace-Based Isolation
Workspace-based isolation is ideal for:
- Managing environments (e.g.,
dev,staging,prod) that share similar infrastructure. - Centralizing configurations for easier maintenance.
- Reducing redundancy while maintaining isolated state files.
Conclusion
Workspace-based isolation offers a flexible way to manage multiple environments with a shared Terraform configuration. By associating each workspace with its own state file, you can ensure environment-specific changes without interference. While it requires careful workspace management, its dynamic nature makes it a powerful tool for modern infrastructure teams.
Let us know how you’re using Terraform workspaces in your projects! Happy Terraforming!