



Introduction
In the vast realm of network security, tools like hping3 serve as both magnifying glasses and stethoscopes, allowing us to inspect and understand the intricate workings of network communications.
While its capabilities are extensive, this blog aims to simplify its core functionalities for beginners. Each command is explained with a real-world analogy and paired with visual prompts, so you can truly grasp what's happening behind the scenes.
1. ICMP Ping Scan
hping3 -1 10.0.0.25
Explanation: Sends an ICMP echo request to check if a host is reachable, like the classic ping command.
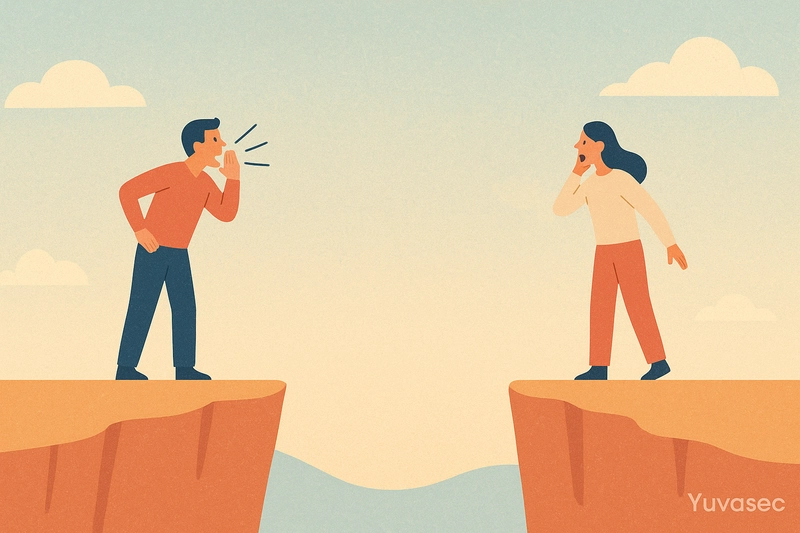
Example: Imagine shouting across a canyon to see if someone is on the other side. If they shout back, you know they're there.
2. ACK Scan on Port 80
hping3 -A 10.0.0.25 -p 80
Explanation: Sends a TCP with the ACK flag set to port 80 of the target to determine if a host is alive, especially useful when ICMP is blocked.
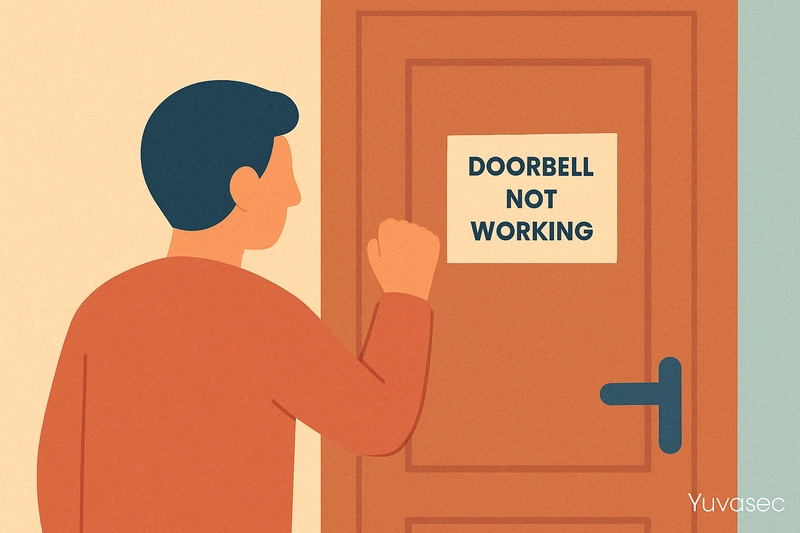
Example: Like knocking on a door in a building where doorbells don’t work. If someone responds, you know they’re home.
3. UDP Scan on Port 80
hping3 -2 10.0.0.25 -p 80
Explanation: Sends a UDP packet; if the port is closed, it replies with an ICMP error; if open, it stays silent.
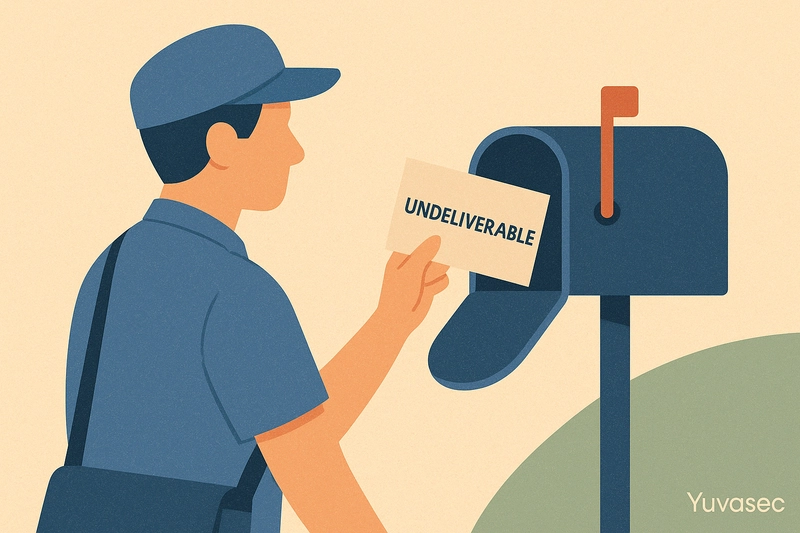
Example: It's like sending a letter without a return address. If the recipient doesn't exist, the post office returns it. If they do, you hear nothing back.
4. Collecting Initial Sequence Numbers (ISNs)
hping3 192.168.1.103 -Q -p 139 -s
Explanation: This collects TCP sequence numbers from the target, which can be used to predict future sequences—a technique sometimes used in advanced attacks.
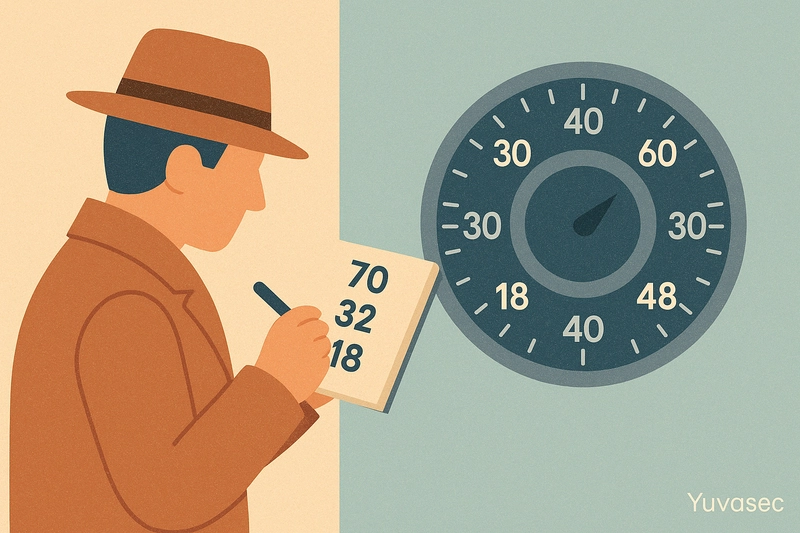
Example: Imagine observing the pattern of a safe’s combination to guess the next number.
5. SYN Scan on Port Range 50–60
hping3 -8 50-60 -S 10.0.0.25 -V
Explanation: Performs a SYN scan across a port range to see which ports are open.
Example: It's akin to trying multiple keys on a door to see which one unlocks it.
6. Listening for HTTP Signatures
hping3 -9 HTTP -I eth0
Explanation: This sets hping3 to listen mode on interface eth0, capturing packets containing the "HTTP" signature..
Example: Like tuning a radio to a specific frequency to catch your favorite show.
7. Traceroute Using hping3
hping3 --traceroute -V -1 10.0.0.25
Explanation: This command mimics the traditional traceroute tool by showing the path taken by packets to reach a destination. It helps identify the routers the packet passes through.
Example: Like a treasure map showing all the checkpoints to reach the gold.
8. SYN Flood Attack Simulation (For Educational Use Only)
hping3 -c 10000 -d 120 -S -w 64 -p 80 --flood --rand-source 10.0.0.25
Explanation: This sends thousands of SYN packets rapidly to simulate a SYN flood—used in DoS attacks. While this is a malicious technique if done on real servers, it’s important to understand how attackers think.
Example: It's like prank calling someone a thousand times from different numbers. They get overwhelmed and can't answer real calls anymore.
⚠️ Warning: This should only ever be practiced in a legal lab environment with permission. Never use this on live systems.
9. Send Custom TCP Packets
hping3 -S -p 80 -a 1.2.3.4 10.0.0.25
Explanation: This sends a SYN packet to port 80 and spoofs the source IP address. It's used in testing how systems react to spoofed traffic.
Example: Like writing a letter and signing it with someone else’s name to see how the recipient reacts. Not ethical in the real world—but useful in a lab.
10. Firewalking (Detecting Firewall Rules)
Concept: By carefully crafting packets, hping3 can help figure out which ports are allowed through a firewall.
Example: Imagine testing a security guard by pretending to be someone important and seeing which doors you can walk through.
Pro Tips for Practice
- Use TryHackMe’s AttackBox or HTB Pwnbox to run hping3 safely.
- Pair hping3 with Wireshark and analyze the packet flows.
- Create a local virtual lab (e.g., VirtualBox with Kali + Metasploitable2).
- Try replicating each anecdote as a hands-on exercise!
Summary Table: hping3 Commands & Concepts
| Command | Concept | Example |
|---|---|---|
-1 | ICMP ping | Shouting across a canyon |
-A | ACK scan | Knocking on a door |
-2 | UDP scan | Sending a letter without reply |
-Q | ISN collection | Cracking a safe |
-8 50-60 | Port scan | Trying multiple keys |
-9 HTTP | Listen for signature | Tuning a radio |
--traceroute | Path mapping | Following a treasure map |
--flood | SYN flood test | Prank calls overload |
-a | IP spoofing | Sending a fake letter |
TTL tuning | Firewalking | Testing security gates |
✨ Conclusion
hping3 might sound like a hacker's tool, but it's really just a sophisticated way to talk to computers and ask, “Hey, are you there? Can I come in?” Like a curious explorer, you can use it to safely navigate the world of networks—learning how systems communicate, how they’re protected, and where potential weaknesses may lie.
Just like learning to ride a bike, the more you play with these commands in a safe environment, the more balanced and confident you become in your cybersecurity journey.
SOCIAL SHARE CARD GENERATOR