
Zum Hauptinhalt springen
tsecurity.de LIVE
Echtzeit-Radar & Feeds
Alle RSS Feeds
👥 Community & Social
Malware / Trojaner / Viren3 Cyber Threats That Defined the Summer of 2026(24.09.2026 um 16:44 Uhr)
IT Security NachrichtenMeta testet menschliche Assistenten für Muse(24.09.2026 um 17:09 Uhr)
IT Security NachrichtenTui Airlines nehmen Vertriebsplattform von Airxelerate in Betrieb(24.09.2026 um 13:32 Uhr)
Malware / Trojaner / Viren3 Cyber Threats That Defined the Summer of 2026(24.09.2026 um 16:44 Uhr)
IT Security NachrichtenMeta testet menschliche Assistenten für Muse(24.09.2026 um 17:09 Uhr)
IT Security NachrichtenTui Airlines nehmen Vertriebsplattform von Airxelerate in Betrieb(24.09.2026 um 13:32 Uhr)
Intelligence View
⚡ tsecurity.de Intelligence

Linux Security Showdown: When Alice, Bob, and Carol Invade /project/shared

Ever wonder what happens when three users walk into a directory? No, this isn't the start of a joke—it’s your next real-world RHEL 9 project! Today, we’ll create a secure multi-user file collaboration system using Linux permissions, ACLs, …

0
↗ Quelle (dev.to)
Reagiere als Erste:r — dein Feedback zählt!

Ever wonder what happens when three users walk into a directory? No, this isn't the start of a joke—it’s your next real-world RHEL 9 project!


Today, we’ll create a secure multi-user file collaboration system using Linux permissions, ACLs, setgid, and the sticky bit—because letting users roam free is chaos, and chaos is for developers, not sysadmins.


So grab your sudo powers and let’s lock this place down.


📚 Table of Contents


  • Meet the Cast

  • Act 1: Forming the Cult, I Mean, Group

  • Act 2: The Sacred Temple of /project/shared

  • Act 3: The Trash Trap with Sticky Business

  • Act 4: The ACL Tribunal

  • Act 5: Testing the Drama

  • Curtain Call: What Did We Learn?

  • Why RealWorld Projects Matter


Meet the Cast


Alice – Project lead. Bossy. Needs full access.


Bob – The “helpful” teammate who thinks he knows more than he does.


Carol – Just here to do her job and avoid drama


Act 1: Forming the Cult, I Mean, Group


We’ll start by creating a secret club called projectteam.
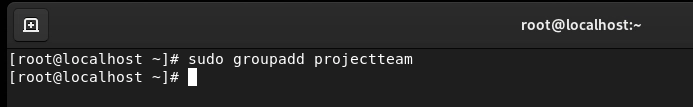


Image description


Now, let’s rope in our trio:


Image description


Yes, -m gives them a home. We’re not monsters.


Act 2: The Sacred Temple of /project/shared


Create a shared space where they can collaborate—or clash.


Image description


Let’s break that down:


Only the owner (root) and projectteam can access.


The setgid (2) ensures anything created in here carries the group like a family curse.


Image description


Act 3: The Trash Trap with Sticky Business


What’s a shared space without a trash folder for your mistakes?


Image description


This folder is special:


  • Everyone can drop files in.


  • Only the file owner (or root) can delete them.


  • Perfect for passive-aggressive document deletions.


Image description


Act 4: The ACL Tribunal


Now it’s time to set the rules of engagement.


Alice gets full control (obviously)


Bob and Carol get read/execute access. Sorry, Bob.


Image description


Act 5: Testing the Drama


Switch to each user and try to stir up trouble.


Image description


Carol? She’s fine. She’ll behave


Curtain Call: What Did We Learn?


  • Setgid makes files inherit group ownership.


  • Sticky bit keeps people from deleting each other’s trash.


  • ACLs allow for fine-tuned control over who does what.


  • Bob should not be trusted with write access. Ever.


And just like that, you’ve built a secure, real-world shared collaboration system in RHEL 9—while fending off chaos, ego, and accidental deletions.


Why RealWorld Projects Matter


Working through hands-on projects like this isn’t just fun—it’s foundational.


Real-world scenarios in RHEL 9 give you the kind of practical experience that job interviews, certification exams, and production environments expect.


You move beyond memorizing commands and start understanding how, when, and why to use them. Plus, nothing beats the confidence that comes from knowing you’ve already solved problems like the ones companies face every day.

CTI Threat Relationship Graph2 Knoten / 1 Relationen
CVE / Incident Software MITRE ATT&CK CWE Weakness IoC
SOC Incident Playbook: Vulnerability Remediation & Verification
title: Detect Exploitation - Linux Security Showdown: When Alice, Bob, and Carol Invade /project/shared
id: 6476832a-f63f-4bca-a707-8f0367a7aeee
status: experimental
description: Automatisch generierte SIEM-Erkennungsregel basierend auf CTI Intelligence
references:
  - https://tsecurity.de/
author: iShareStuff CTI Automated Detection Engine
date: 2026-09-24
logsource:
  category: network_connection
  product: any
detection:
  selection:
      CommandLine|contains:
        - 'exploit'
  condition: selection
falsepositives:
  - Legitime administrative Zugriffe oder Penetrationstests
level: high
tags:
  - attack.initial_access
rule CTI_Threat_Indicator {
    meta:
        author = "iShareStuff CTI Automated Detection Engine"
        date = "2026-09-24"
        description = "YARA Signature for "
    strings:
        $str = "Linux Security Showdown: When " ascii wide
    condition:
        any of them
}
tsecurity.de Cognitive Threat RAG
Fokus-Vektor:

Kognitive Analyse für identifizierte Bedrohung: Erhöhte Bedrohungslage im Bereich Linux Security Showdown: When Alice, Bob.... Basierend auf 368k Vektor-Korrelationen werden sofortige Isolationsmaßnahmen für betroffene Endpunkte empfohlen.

🛡️ Angriffsfläche & Exposure

Netzwerk/Remote-Zugriff ohne Vorauthentifizierung möglich.

Empfohlene Sofortmaßnahmen
  • 1. Perimeter-Inspektion: Relevante Portfreigaben und exponierte Endpunkte unverzüglich scannen.
  • 2. Patch-Applikation: Hersteller-Hotfix einspielen oder betroffene Daemons in isolierte DMZ-Segmente überführen.
  • 3. Telemetrie & EDR-Alerts: Prozessaufrufe und Child-Processes auf anomale Shell-Spawns überwachen.
🔗 Semantisch verwandte Zero-Days MariaDB 11.7 VEC
Ähnliche Beiträge
🔍 Verwandte News

Auch interessante Nachrichten Linux Security Showdown: When Alice, Bob, and Carol Invade /project/shared

Thematisch verwandte Begriffe: Linux, Security, Showdown, When · 6 Treffer

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Zum Aktualisieren ziehen
ZERO-DAY CVE-2026-97360 | HFS2 version 2.4.0 and earlier contains an unauthenticated arbitrary fil…
Advisory →
TTS Reader • tsecurity.de Voice
tsecurity.de Icon
tsecurity.de App
Offline-Lesen, Eilmeldungen & 0ms Ladezeit

Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.

Nächster Beitrag
Themen-Radar & Intelligence Matrix
Echtzeit-Taxonomie nach Angriffsvektoren & Plattformen

tsecurity.de Live Threat Radar

🔴 LIVE RADAR
MONITORING
AKTIV
CVE-DATENBANK
LIVE
🔍
Community Radar & Live Chat
Sentinel Bot online • Live-Stream
Dein Cluster: Security Explorer
Match:
lädt…
Verbindung zum Community-Stream wird aufgebaut...
Bearbeitungsmodus — Senden überschreibt deine Nachricht
Community-Puls — was gerade passiert
lädt…
Aktivitäten deiner Analysten
lädt…
Neues Thema oder Eilmeldung einreichen

Reiche interessante Links, Zero-Days oder Debatten ein. Die Community entscheidet per Upvote über die Veröffentlichung.

Heiß diskutierte Einreichungen
🔖 Gespeicherte Artikel
📂 Keine gespeicherten Artikel vorhanden.
Zurück Ziehen Vor
Links: vorheriger Artikel Rechts: nächster Artikel unten: schließen
News NIS-2 Frühwarnung Tier-1 Intel TTP ⏱️ 3 Min vor 10 Min
Artikeldaten werden geladen...

Zurück: vorheriger Vor: nächster
↗ Original-Quelle
Social Reaktionen Deine Reaktion zählt
Einstufung & Relevanz-Poll 0 Stimmen
In sozialen Netzwerken teilen 1-Klick