
Zum Hauptinhalt springen
tsecurity.de LIVE
Echtzeit-Radar & Feeds
Alle RSS Feeds
👥 Community & Social
Sichere ProgrammierungWhat is Programming And How i can Enjoy it?(24.09.2026 um 11:54 Uhr)
Sichere ProgrammierungYou Don't Need Adobe Commerce Cloud to Survive Black Friday(24.09.2026 um 11:55 Uhr)
Malware / Trojaner / VirenBeyond Lazarus: Organization of DPRK cyber capabilities(24.09.2026 um 11:59 Uhr)
Malware / Trojaner / VirenBeyond Lazarus: Organization of DPRK Cyber Capabilities(24.09.2026 um 11:59 Uhr)
Malware / Trojaner / VirenThe fake worker threat and the rise of human infiltration(24.09.2026 um 11:59 Uhr)
Malware / Trojaner / VirenPolinRider Spreads Through Compromised GitHub Accounts and Packagist(24.09.2026 um 11:59 Uhr)
Malware / Trojaner / VirenWeaselBiscuit Strips BeaverTail and OtterCookie Down to Essentials(24.09.2026 um 11:59 Uhr)
Sichere ProgrammierungWhat is Programming And How i can Enjoy it?(24.09.2026 um 11:54 Uhr)
Sichere ProgrammierungYou Don't Need Adobe Commerce Cloud to Survive Black Friday(24.09.2026 um 11:55 Uhr)
Malware / Trojaner / VirenBeyond Lazarus: Organization of DPRK cyber capabilities(24.09.2026 um 11:59 Uhr)
Malware / Trojaner / VirenBeyond Lazarus: Organization of DPRK Cyber Capabilities(24.09.2026 um 11:59 Uhr)
Malware / Trojaner / VirenThe fake worker threat and the rise of human infiltration(24.09.2026 um 11:59 Uhr)
Malware / Trojaner / VirenPolinRider Spreads Through Compromised GitHub Accounts and Packagist(24.09.2026 um 11:59 Uhr)
Malware / Trojaner / VirenWeaselBiscuit Strips BeaverTail and OtterCookie Down to Essentials(24.09.2026 um 11:59 Uhr)
Intelligence View
⚡ tsecurity.de Intelligence

AWS Serverless: Build a Custom IAM Policy for Lambda CI/CD with SAM and GitHub – Part 2

In my previous article, I explained how to create a CICD pipeline to build and deploy a simple lambda function integrated with API Gateway using AWS SAM and GitHub. Please make sure you've reviewed this article on this CI/CD topic (link…

0
↗ Quelle (dev.to)
Reagiere als Erste:r — dein Feedback zählt!

In my previous article, I explained how to create a CICD pipeline to build and deploy a simple lambda function integrated with API Gateway using AWS SAM and GitHub.


Please make sure you've reviewed this article on this CI/CD topic (link below). I won’t repeat that content here, but understanding it is essential for following along with the custom policy setup in this article.


https://dev.to/bhatiagirish/aws-serverless-build-a-cicd-pipeline-for-lambda-and-api-gateway-using-sam-and-github-part-1-313b


While building this solution, I temporarily assigned broad permissions such as full access to services like S3, CloudFormation, Lambda and API Gateway.


Assigning these full access permission is against the principle of least privilege that means grant only the specific permissions required.


In this article, I will focus on replacing these broad permissions with a custom fine grained IAM policy that only grants the permissions required by this pipeline.


This approach aligns with AWS security best practices and the principle of least privilege helping reduce security risks and improve overall security posture of the AWS environment.


Let's look at the architecture diagram!
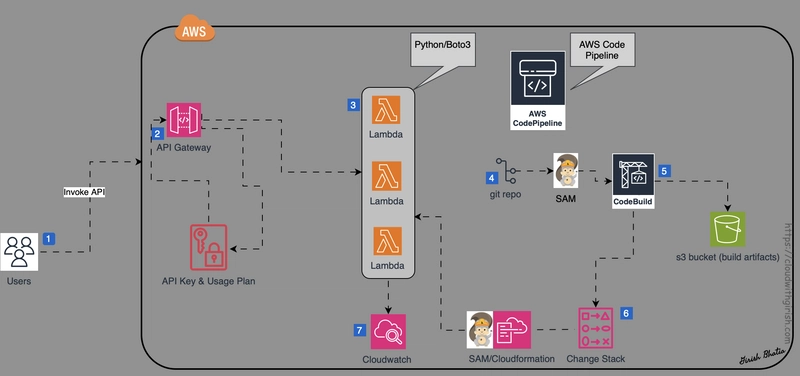


Image arch


Why Use a Custom Policy?


Using custom policies for CICD pipelines offers several advantages for enterprises. Principle of least privilege is an important factor for overall security posture. By implementing the principle of least privilege, you can significantly improve your security posture and operational efficiency.


Custom policies can help in several areas including:


Limit potential impact if credentials are ever compromised


  • Example: Restrict S3 access to only the specific bucket used for SAM deployment artifacts rather than allowing wildcard access to all buckets.

  • Example: Limit CloudFormation permissions to only the named stack used for deploying the Lambda and API resources.


Awareness of what permissions their automation requires


  • Example: Allow updates to specific Lambda functions, but restrict permission to create or delete unrelated AWS resources like DynamoDB or IAM roles.

  • Example: Permit API Gateway stage deployments only to defined stages like dev, test or permission to specific methods like Get and Post


Prevent unintended resource creation or deletion


  • Example: Deny s3:DeleteBucket and cloudformation:DeleteStack to avoid accidental loss of critical deployment artifacts or stacks.


Support document and demonstrate security control required for compliance


  • Example: Create IAM policies that clearly define allowed actions (like lambda:UpdateFunctionCode, apigateway:POST, cloudformation:DescribeStacks) and map directly to each pipeline step.

  • Example: Provide audit-ready IAM documentation showing that the CI/CD pipeline operates with least privilege.


Review Custom Policy


Below is an example of a custom IAM policy tailored for a CI/CD pipeline that deploys a Lambda function and API Gateway using AWS SAM. This pipeline is triggered by a code push to a GitHub repository and uses AWS CodePipeline and CodeBuild to build and deploy the serverless application.


The policy grants only the necessary permissions to interact with Lambda, API Gateway, S3, and CloudFormation, following the principle of least privilege.
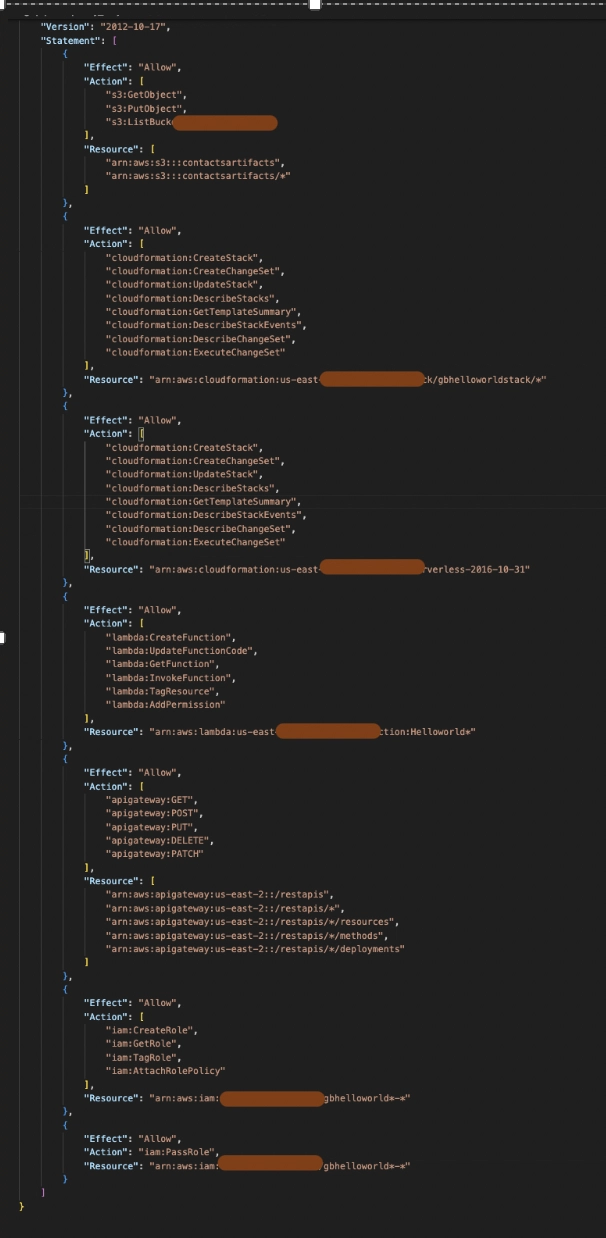


Image custpolicy


Once this policy is drafted, attach it to the role for the code build/code pipeline.


Push a code change to Git Repo


Let’s make a change to the Lambda function and commit the updated code to the Git repository.


Once the changes are pushed, this will automatically trigger the AWS Code Pipeline.
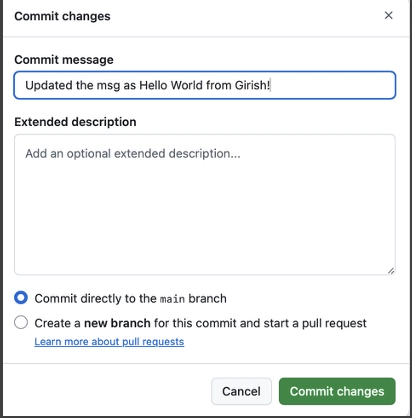


Image codepushed


After the pipeline starts, we’ll review the build and deployment stages to confirm the updated function is successfully redeployed.


You can see that the pipeline automatically triggered the Source and Build stages, both of which completed successfully!
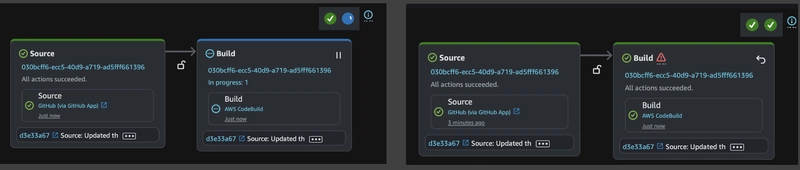


Image pipeline


Validate by Invoking the deployed function and API


Since the pipeline has successfully completed, the updated Lambda function and API have been deployed. Let's validate again using Postman.


Image postman2


You should now see the updated message returned by the Lambda function through the API endpoint, confirming that the changes were successfully deployed.


Review S3 bucket for Code artifact


You can also review the S3 bucket where AWS Code Pipeline stores the build artifacts generated during the pipeline execution.
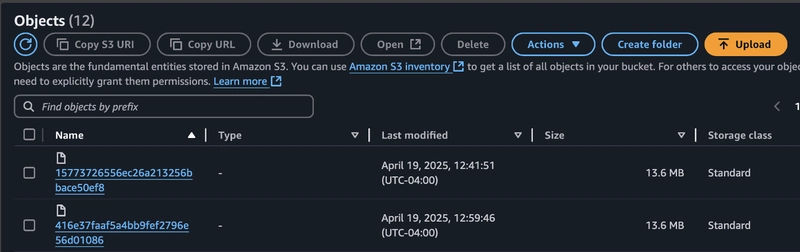


Image s3artifacts


Review Cloud Watch log


The Lambda function is integrated with CloudWatch, and a dedicated log group is automatically created.


You can view the logs by navigating to the function’s log group in the CloudWatch Logs section of the AWS Console.


Image cwlogs


Cleanup - Delete resources


Once you’ve completed this exercise, make sure to delete all the resources created to avoid unnecessary charges that could impact your overall cloud cost and budget.


In particular, remember to delete the following:


  • The AWS Code Pipeline

  • The CodeBuild project

  • Any S3 buckets used for artifacts (if not reused elsewhere)

  • The Lambda function, API Gateway, and associated CloudWatch log groups

  • IAM roles created for the pipeline and build process (if they’re not reused)


Conclusion


In this article, I demonstrated how to build a custom IAM policy for a Lambda CI/CD pipeline using AWS SAM and GitHub.


Using a custom policy helps ensure that the Code Pipeline adheres to the principle of least privilege, keeping your AWS resources more secure.


I hope you found this article both helpful and informative!


Thank you for reading!


Watch the video here:


𝒢𝒾𝓇𝒾𝓈𝒽 ℬ𝒽𝒶𝓉𝒾𝒶

𝘈𝘞𝘚 𝘊𝘦𝘳𝘵𝘪𝘧𝘪𝘦𝘥 𝘚𝘰𝘭𝘶𝘵𝘪𝘰𝘯 𝘈𝘳𝘤𝘩𝘪𝘵𝘦𝘤𝘵 & 𝘋𝘦𝘷𝘦𝘭𝘰𝘱𝘦𝘳 𝘈𝘴𝘴𝘰𝘤𝘪𝘢𝘵𝘦

𝘊𝘭𝘰𝘶𝘥 𝘛𝘦𝘤𝘩𝘯𝘰𝘭𝘰𝘨𝘺 𝘌𝘯𝘵𝘩𝘶𝘴𝘪𝘢𝘴

IoC Intelligence (1 Indikatoren)
dev[.]to
CTI Threat Relationship Graph2 Knoten / 1 Relationen
CVE / Incident Software MITRE ATT&CK CWE Weakness IoC
SOC Incident Playbook: Remote Code Execution (RCE) Defense
title: Detect Exploitation - AWS Serverless: Build a Custom IAM Policy for Lambda CI/CD with SAM and GitHub – Part 2
id: ac93c3e4-082c-4da0-9d41-2c6b57ee45b7
status: experimental
description: Automatisch generierte SIEM-Erkennungsregel basierend auf CTI Intelligence
references:
  - https://tsecurity.de/
author: iShareStuff CTI Automated Detection Engine
date: 2026-09-24
logsource:
  category: network_connection
  product: any
detection:
  selection:
      DestinationHostname:
        - 'dev.to'
  condition: selection
falsepositives:
  - Legitime administrative Zugriffe oder Penetrationstests
level: high
tags:
  - attack.initial_access
rule CTI_Threat_Indicator {
    meta:
        author = "iShareStuff CTI Automated Detection Engine"
        date = "2026-09-24"
        description = "YARA Signature for "
    strings:
        $str = "AWS Serverless: Build a Custom" ascii wide
    condition:
        any of them
}
tsecurity.de Cognitive Threat RAG
Fokus-Vektor:

Kognitive Analyse für identifizierte Bedrohung: Erhöhte Bedrohungslage im Bereich AWS Serverless: Build a Custom IAM Polic.... Basierend auf 368k Vektor-Korrelationen werden sofortige Isolationsmaßnahmen für betroffene Endpunkte empfohlen.

🛡️ Angriffsfläche & Exposure

Netzwerk/Remote-Zugriff ohne Vorauthentifizierung möglich.

Empfohlene Sofortmaßnahmen
  • 1. Perimeter-Inspektion: Relevante Portfreigaben und exponierte Endpunkte unverzüglich scannen.
  • 2. Patch-Applikation: Hersteller-Hotfix einspielen oder betroffene Daemons in isolierte DMZ-Segmente überführen.
  • 3. Telemetrie & EDR-Alerts: Prozessaufrufe und Child-Processes auf anomale Shell-Spawns überwachen.
🔗 Semantisch verwandte Zero-Days MariaDB 11.7 VEC
Ähnliche Beiträge
🔍 Verwandte News

Auch interessante Nachrichten AWS Serverless: Build a Custom IAM Policy for Lambda CI/CD with SAM and GitHub – Part 2

Thematisch verwandte Begriffe: Serverless, Build, Custom, Policy · 6 Treffer

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Zum Aktualisieren ziehen
ZERO-DAY Kritische Sicherheitsmeldung
Advisory →
TTS Reader • tsecurity.de Voice
tsecurity.de Icon
tsecurity.de App
Offline-Lesen, Eilmeldungen & 0ms Ladezeit

Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.

Nächster Beitrag
Themen-Radar & Intelligence Matrix
Echtzeit-Taxonomie nach Angriffsvektoren & Plattformen

tsecurity.de Live Threat Radar

🔴 LIVE RADAR
MONITORING
AKTIV
CVE-DATENBANK
LIVE
🔍
Community Radar & Live Chat
Sentinel Bot online • Live-Stream
Dein Cluster: Security Explorer
Match:
lädt…
Verbindung zum Community-Stream wird aufgebaut...
Bearbeitungsmodus — Senden überschreibt deine Nachricht
Community-Puls — was gerade passiert
lädt…
Aktivitäten deiner Analysten
lädt…
Neues Thema oder Eilmeldung einreichen

Reiche interessante Links, Zero-Days oder Debatten ein. Die Community entscheidet per Upvote über die Veröffentlichung.

Heiß diskutierte Einreichungen
🔖 Gespeicherte Artikel
📂 Keine gespeicherten Artikel vorhanden.
Zurück Ziehen Vor
Links: vorheriger Artikel Rechts: nächster Artikel unten: schließen
News NIS-2 Frühwarnung Tier-1 Intel TTP ⏱️ 3 Min vor 10 Min
Artikeldaten werden geladen...

Zurück: vorheriger Vor: nächster
↗ Original-Quelle
Social Reaktionen Deine Reaktion zählt
Einstufung & Relevanz-Poll 0 Stimmen
In sozialen Netzwerken teilen 1-Klick