
Zum Hauptinhalt springen
tsecurity.de LIVE
Echtzeit-Radar & Feeds
Alle RSS Feeds
👥 Community & Social
Windows Tipps & SecurityNighthawk M7 Pro im Test: Flexibler, aber teurer 5G-Router(21.09.2026 um 10:30 Uhr)
Sichere ProgrammierungNeue Gmail-Funktion: So sparst du jetzt Zeit bei Einmalcodes(21.09.2026 um 10:00 Uhr)
Sichere ProgrammierungYour GIF exporter is fine — the container is the problem(21.09.2026 um 10:01 Uhr)
Sichere ProgrammierungCSS, Motion, or GSAP? I Choose by Who Owns the Animation(21.09.2026 um 10:12 Uhr)
Windows Tipps & SecurityNighthawk M7 Pro im Test: Flexibler, aber teurer 5G-Router(21.09.2026 um 10:30 Uhr)
Sichere ProgrammierungNeue Gmail-Funktion: So sparst du jetzt Zeit bei Einmalcodes(21.09.2026 um 10:00 Uhr)
Sichere ProgrammierungYour GIF exporter is fine — the container is the problem(21.09.2026 um 10:01 Uhr)
Sichere ProgrammierungCSS, Motion, or GSAP? I Choose by Who Owns the Animation(21.09.2026 um 10:12 Uhr)
Intelligence View
⚡ tsecurity.de Intelligence

🕵️‍♂️ Blog – Auditing & Monitoring Identities in Real Time: Alerting, Logging and Response

Today, we dive into Identity Auditing & Monitoring — one of the most overlooked yet critical layers of identity management. Whether you manage an on-prem Windows Server, a hybrid Azure AD setup, or a Linux Server, monitoring user b…

0
↗ Quelle (dev.to)
Reagiere als Erste:r — dein Feedback zählt!

Today, we dive into Identity Auditing & Monitoring — one of the most overlooked yet critical layers of identity management. Whether you manage an on-prem Windows Server, a hybrid Azure AD setup, or a Linux Server, monitoring user behavior and identity-related events is key to detecting insider threats, policy violations and misconfigurations in real time.


🧠 Why Identity Auditing & Monitoring Matters


  • 🛡️ Security: Track logins, privilege escalations and abnormal behavior.

  • 📜 Compliance: Required for standards like ISO 27001, HIPAA, PCI-DSS, etc.

  • ⏱️ Forensics: Enable investigation of who accessed what and when.

  • 🔔 Alerting: Prevent incidents before they escalate.


🔍 1. Windows Server (Active Directory)

🔑 What to Monitor:


  • Logon/logoff events (Event ID 4624/4634)

  • Account lockouts (4740)

  • Privilege use (4672)

  • Group membership changes (4728/4729)

  • New user creations (4720)


🔧 Tools:


  • Event Viewer: Local and remote audit log inspection.

  • Group Policy: Enable Advanced Audit Policy Configuration.

  • Sysmon + Windows Event Forwarding (WEF): Collect logs centrally.

  • SIEM Tools: Send logs to Splunk, Microsoft Sentinel, or Graylog.


powershell


AuditPol /get /category:Logon/Logoff


📌 Pro Tip:

Use PowerShell with Task Scheduler to email alerts for specific Event IDs.


☁️ 2. Azure Active Directory (Entra ID)

Azure AD includes cloud-native auditing and monitoring features out-of-the-box.


🔍 Key Identity Logs:


  • Sign-in logs: Who logged in, from where, using what method.

  • Audit logs: Password resets, group changes, license assignments.

  • Conditional Access Insights: Policy results and failures.


🔧 Tools:


  • Microsoft Entra Admin Center → Monitoring → Audit Logs & Sign-ins

  • Microsoft Sentinel: Advanced log correlation and threat detection.

  • Graph API / KQL Queries: Automate extraction of specific identity events.


kusto


SigninLogs

| where ResultType != 0

| project UserPrincipalName, IPAddress, Status


🔐 Pro Tip:

Enable Identity Protection to detect risky sign-ins and compromised accounts based on behavior analytics.


🐧 3. Linux Server (LDAP/SSSD Integrated)

🔍 What to Monitor:


  • Login attempts via /var/log/auth.log or /var/log/secure

  • sudo command executions

  • User add/modify/delete events


PAM (Pluggable Authentication Module) failures


🔧 Tools:


  • auditd: Linux Audit Daemon for tracking system calls.

  • Logwatch / Logrotate: Email summaries of suspicious activities.

  • fail2ban: Detect and block brute-force login attempts.

  • Auditbeat + Elastic Stack: For visual dashboards and alerting.


bash


ausearch -m USER_LOGIN,USER_START -ts today


📌 Pro Tip:

Use auditctl rules to track changes to /etc/passwd, /etc/shadow and group files for identity tampering.


📊 Real-Time Monitoring Strategies
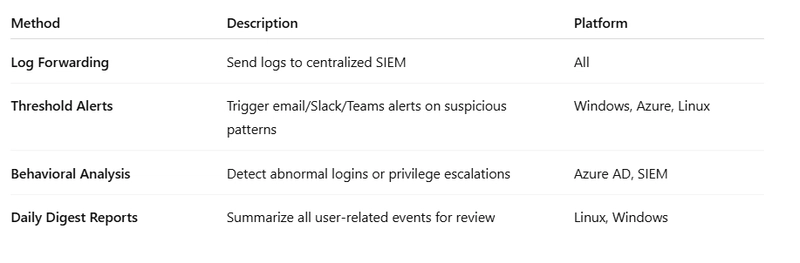


Image description


🛠️ Tools That Make Monitoring Easy


Image description


🧩 Wrapping Up

Effective identity monitoring and auditing isn't optional anymore. Whether you're operating in a hybrid or pure-cloud environment, having visibility and control over identity-related events is essential for:


✅ Proactive security

✅ Policy enforcement

✅ Compliance readiness

✅ Quick incident response


Even if you're a solo developer or a small IT team — start with baseline auditing and automate alerts over time. Trust me — future-you (and your security team) will thank you.

Ähnliche Beiträge
🔍 Verwandte News

Auch interessante Nachrichten 🕵️‍♂️ Blog – Auditing & Monitoring Identities in Real Time: Alerting, Logging and Response

Thematisch verwandte Begriffe: Blog, Auditing, Monitoring, Identities · 6 Treffer

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Zum Aktualisieren ziehen
ZERO-DAY CVE-2026-94030 | A security vulnerability has been detected in SerenityOS up to 3d83e4509…
Advisory →
TTS Reader • tsecurity.de Voice
tsecurity.de Icon
tsecurity.de App
Offline-Lesen, Eilmeldungen & 0ms Ladezeit

Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.

Nächster Beitrag
Themen-Radar & Intelligence Matrix
Echtzeit-Taxonomie nach Angriffsvektoren & Plattformen

tsecurity.de Live Threat Radar

🔴 LIVE RADAR
MONITORING
AKTIV
CVE-DATENBANK
LIVE
🔍
Community Radar & Live Chat
Sentinel Bot online • Live-Stream
Dein Cluster: Security Explorer
Match:
lädt…
Verbindung zum Community-Stream wird aufgebaut...
Bearbeitungsmodus — Senden überschreibt deine Nachricht
Community-Puls — was gerade passiert
lädt…
Aktivitäten deiner Analysten
lädt…
Neues Thema oder Eilmeldung einreichen

Reiche interessante Links, Zero-Days oder Debatten ein. Die Community entscheidet per Upvote über die Veröffentlichung.

Heiß diskutierte Einreichungen
🔖 Gespeicherte Artikel
📂 Keine gespeicherten Artikel vorhanden.
Zurück Ziehen Vor
Links: vorheriger Artikel Rechts: nächster Artikel unten: schließen
News NIS-2 Frühwarnung Tier-1 Intel ⏱️ 3 Min vor 10 Min
Artikeldaten werden geladen...

Zurück: vorheriger Vor: nächster
↗ Original-Quelle
Social Reaktionen Deine Reaktion zählt
Einstufung & Relevanz-Poll 0 Stimmen
In sozialen Netzwerken teilen 1-Klick