
Zum Hauptinhalt springen
Echtzeit-Radar & Feeds
Alle RSS Feeds ➔
👥 Community & Social
•
Sicherheitslücken (CVE)DSA-6530-1 pcre2 - security update(29.09.2026 um 02:00 Uhr)
•
Linux Tipps & HardeningDSA-6529-1 libwebsockets - security update(29.09.2026 um 02:00 Uhr)
•••••••••
Sicherheitslücken (CVE)DSA-6530-1 pcre2 - security update(29.09.2026 um 02:00 Uhr)
•
Linux Tipps & HardeningDSA-6529-1 libwebsockets - security update(29.09.2026 um 02:00 Uhr)
••••••••
Intelligence View
⚡ tsecurity.de Intelligence

Youtube virusbtn: Inside Akira, ransomware's Rust experiment — Ben Herzog, Check Point

Video von Youtube virusbtn auf YouTube: Author: Virus Bulletin - Bewertung: 0x - Views:1 Inside Akira, ransomware's Rust experiment Presented at the VB2025…

HD Video
Inside Akira, ransomware's Rust experiment — Ben Herzog, Check Point
Video abspielen
0
↗ Quelle (youtube.com)
Reagiere als Erste:r — dein Feedback zählt!

Author: Virus Bulletin - Bewertung: 0x - Views:1

Inside Akira, ransomware's Rust experiment


Presented at the VB2025 conference in Berlin, 24 - 26 September 2025.

↓ Slides: N/A

↓ Paper: https://www.virusbulletin.com/uploads/pdf/conference/vb2025/papers/Inside-Akira-ransomwares-Rust-experiment.pdf

→ Details: https://www.virusbulletin.com/conference/vb2025/abstracts/inside-akira-ransomwares-rust-experiment/


✪ PRESENTED BY ✪


• Ben Herzog (Check Point Software Technologies)


✪ ABSTRACT ✪


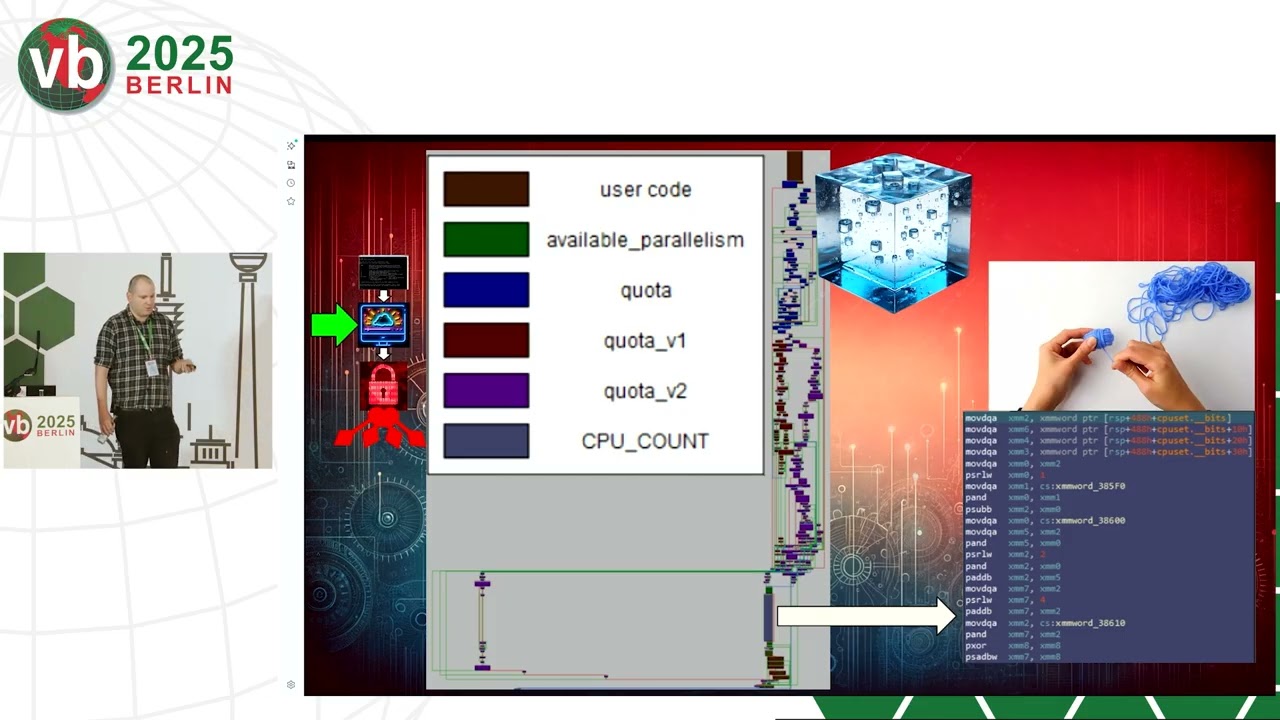
Rust binaries are notoriously resistant to "full RE" that maps the binary functionality end to end. In this research, we do just that – analysing "Akira v2", a Rust-based encryptor circulated by the prolific Akira RaaS group in early 2024. We work through the binary's opaque, sometimes barely documented, built-in types; its aggressively recursive in-lining of library code; and other "surprises" prepared for us by the Rust compiler. We explain in detail how we approached all these obstacles, and how one can methodically cross-reference Rust docs and idioms to understand code that would otherwise be impenetrable. We lay out the binary's structure, control flow, and even some of the original author's design process – and we see how all these factors translate into assembly, sometimes in surprising ways.

2. Cyber Threat Intelligence & Forensik

CTI Threat Relationship Graph5 Knoten / 4 Relationen
CVE / Incident Software MITRE ATT&CK CWE Weakness IoC
MITRE ATT&CK Matrix Navigator 14 Taktiken
1 belegte TechnikenLive-Mapping
Reconnaissance
Resource Development
Initial Access
Execution
Persistence
Privilege Escalation
Defense Evasion
Credential Access
Discovery
Lateral Movement
Collection
Command and Control
Exfiltration
Impact
Ähnliche Beiträge
🔍 Verwandte News

Auch interessante Nachrichten Inside Akira, ransomware's Rust experiment — Ben Herzog, Check Point

Thematisch verwandte Begriffe: Inside, Akira, ransomwares, Rust · 6 Treffer

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

💬 Kommentare werden geladen…
Zum Aktualisieren ziehen
ZERO-DAY CVE-2026-71189 | An attacker can construct a request that, if issued by another applicati…
Advisory →
tsecurity.de Icon
Offline-Lesen, Eilmeldungen & 0ms Ladezeit

Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.

Nächster Beitrag