
Zum Hauptinhalt springen
Echtzeit-Radar & Feeds
Alle RSS Feeds ➔
👥 Community & Social
Windows Tipps & SecurityGrafikkarte vor Überhitzung schützen: So geht’s(25.09.2026 um 08:00 Uhr)
••••••••••
Windows Tipps & SecurityGrafikkarte vor Überhitzung schützen: So geht’s(25.09.2026 um 08:00 Uhr)
••••••••••
Intelligence View
⚡ tsecurity.de Intelligence

I’m 16, broke, and I built a "Cursor for Writers" using Next.js + Groq ($7 budget)

The "Chat" interface is killing our creativity. We have Cursor for coding. It knows our repo, understands our dependencies, and writes code in context. But for writing novels? We are still stuck copy-pasting text into a "Chat" box that…

0
↗ Quelle (dev.to)
Reagiere als Erste:r — dein Feedback zählt!

The "Chat" interface is killing our creativity.


We have Cursor for coding. It knows our repo, understands our dependencies, and writes code in context.


But for writing novels? We are still stuck copy-pasting text into a "Chat" box that forgets the main character's name every 4,000 words.


I couldn't afford a $30/month subscription to enterprise tools. So, I spent my last $7 building my own Agentic IDE on the Groq LPU.


Here is the tech stack, the architecture, and how I solved the "Context Amnesia" problem on a high school student's budget.

🏗️ The Problem: "Context Amnesia"


Standard LLMs have a "Slide Window" memory. If you are writing Chapter 20, the model has likely forgotten the foreshadowing you planted in Chapter 1.


Most "AI Writers" are just wrappers around GPT-4. They treat your novel like a conversation, not a project.


I needed an Agent, not a chatbot.

🛠️ The "Broke" Tech Stack ($7/mo)


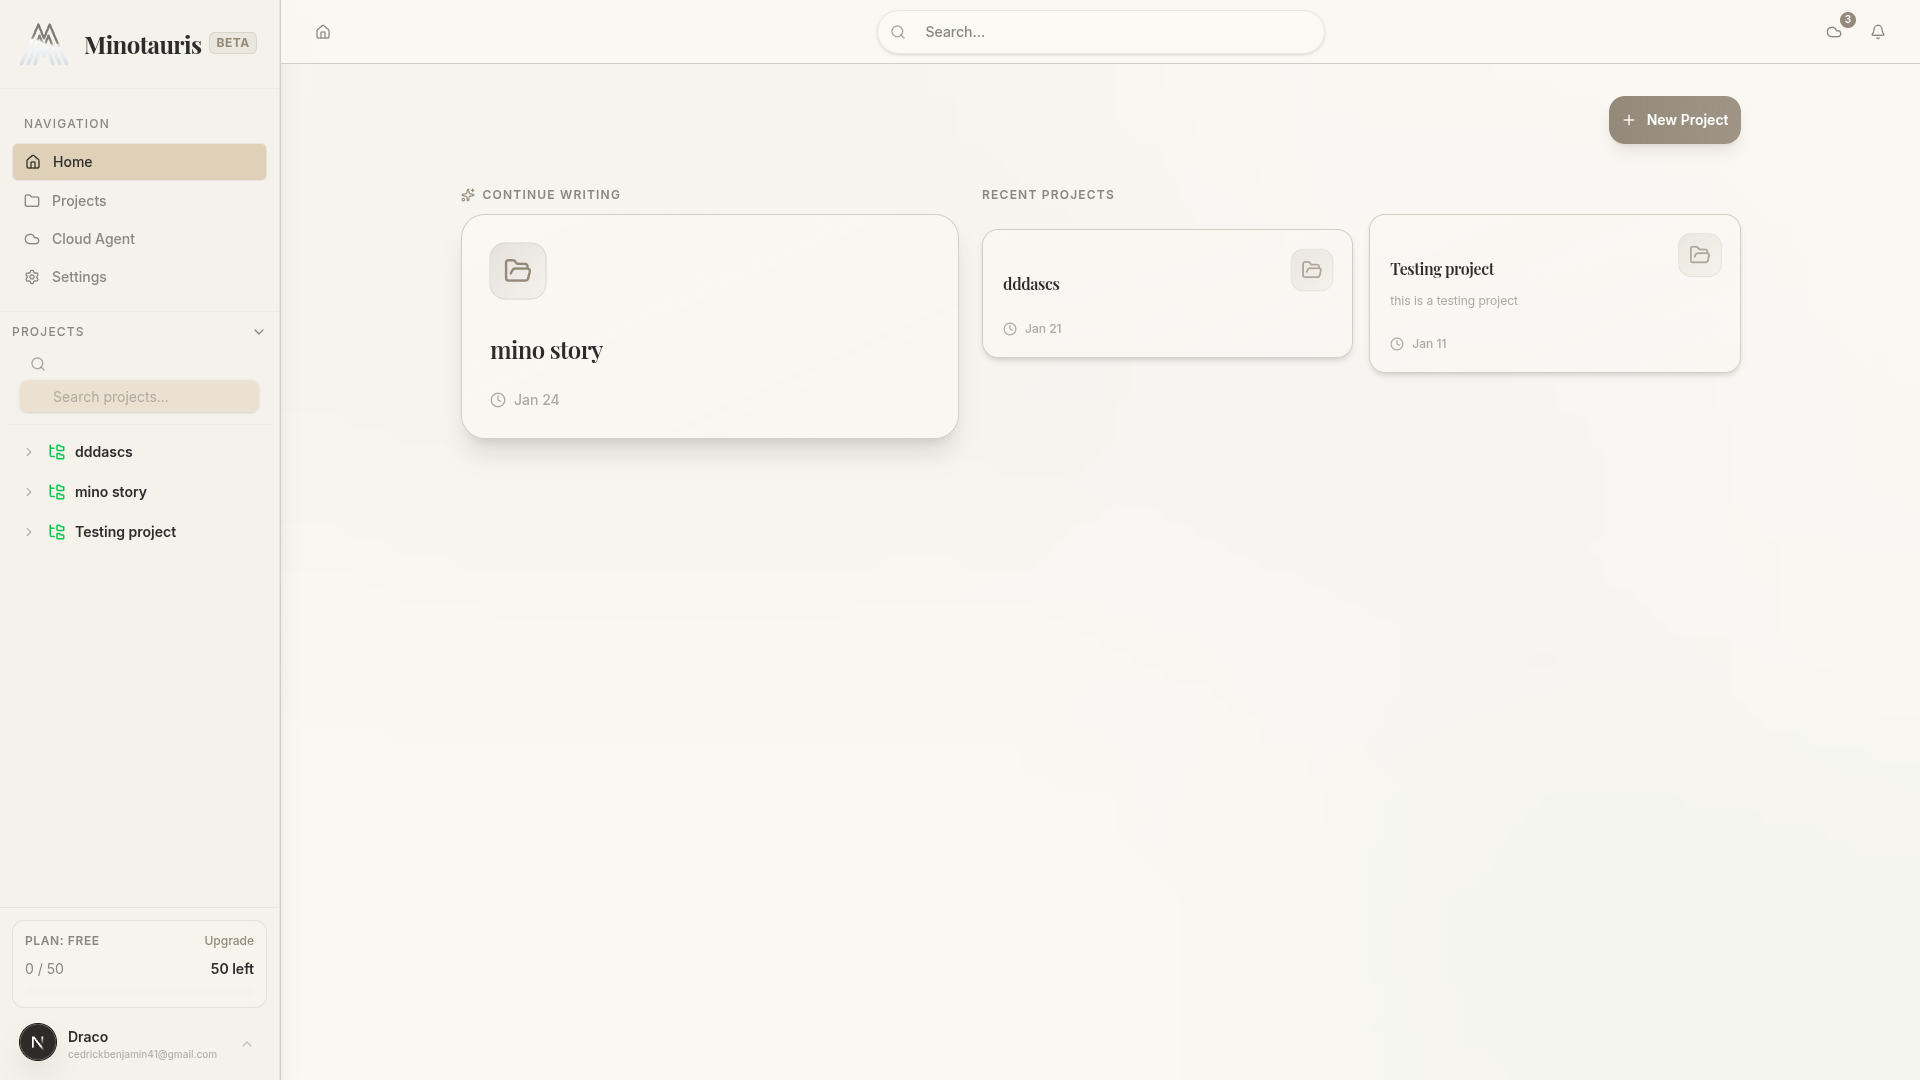
I call it Minotauris. It’s built to run lean but act smart.


Frontend: Next.js 15 (App Router) + Tailwind CSS.

Backend: Supabase (Auth + Database).

The Brain (Smart): deepseek-r1-distill-llama-70b (via Groq) for reasoning/plotting.

The Muscle (Fast): llama-3.1-8b-instant (via Groq) for prose/drafting.

The Orchestrator: A custom TypeScript router that decides which model to use.


🧠 The "Smart Router" (How I save money)


Since I'm 16 and not VC-backed, I can't let users burn $100 in API credits. I built a Traffic Router in Supabase Edge Functions:

TypeScript


// The logic is simple:
// 1. If the task is "Planning" -> Use Expensive Model (70B)
// 2. If the task is "Drafting" -> Use Cheap Model (8B)
// 3. If User > Monthly Limit -> Enforce "Slow Pool" (Artifical Delay)
![ ](https://dev-to-uploads.s3.amazonaws.com/uploads/articles/427v5m4p77pcilttljlg.png)


This lets me offer "Unlimited" basic drafting because Llama 8B on Groq is practically free (~$0.05 per million tokens).

⚡ The Agentic Workflow


Minotauris isn't a chat. It’s an Asynchronous Command Center.


The Lore Index: I vector-embed the user's "Story Bible" (Characters, Locations, Rules).

The Command: User types: "Refactor Chapter 4 to be more suspenseful."

The Sub-Agent: The AI pulls the specific lore needed for Chapter 4, checks the tone of Chapter 1, and rewrites the text in the background.


I also built a Mobile Command Mode. You can send commands from your phone while walking the dog, and the cloud agent executes the heavy lifting on the server.

"Demon Mode" Development


I built the MVP in 2 weeks using v0 for the UI and Cursor for the backend logic.


I’m currently running a closed Alpha because my wallet can't handle the whole internet yet. But if you are a developer who writes (or a writer who devs), I’d love your feedback on the architecture.


The Waitlist is here: 👉 minotauris.app


Let me know in the comments: How are you handling long-context in your own AI apps? RAG? Long-context caching? I need optimization tips before I go broke lol.

1. Sofort-Triage & Abwehrmaßnahmen

SOC Incident Playbook: Remote Code Execution (RCE) Defense
Syntax validiert (0 Fehler)
title: Detect Exploitation - I’m 16, broke, and I built a "Cursor for Writers" using Next.js + Groq ($7 budget)
id: a2110354-1013-4378-8d96-0b847fad05d8
status: experimental
description: Automatisch generierte SIEM-Erkennungsregel basierend auf CTI Intelligence
references:
  - https://tsecurity.de/
author: iShareStuff CTI Automated Detection Engine
date: 2026-09-27
logsource:
  category: network_connection
  product: any
detection:
  selection:
      CommandLine|contains:
        - 'exploit'
  condition: selection
falsepositives:
  - Legitime administrative Zugriffe oder Penetrationstests
level: high
tags:
  - attack.initial_access
Syntax validiert (0 Fehler)
rule CTI_Threat_Indicator {
    meta:
        author = "iShareStuff CTI Automated Detection Engine"
        date = "2026-09-27"
        description = "YARA Signature for "
    strings:
        $str = "I’m 16, broke, and I built a \"" ascii wide
    condition:
        any of them
}
Syntax validiert (0 Fehler)
index=security sourcetype IN ("cisco:asa", "pan:traffic", "zeek_conn", "suricata", "WinEventLog:Security")
("Im 16 broke and I built a Cursor for Wri")
| stats count earliest(_time) as first_seen latest(_time) as last_seen by src_ip, dest_ip, dest_host, signature
| eval first_seen=strftime(first_seen, "%Y-%m-%d %H:%M:%S"), last_seen=strftime(last_seen, "%Y-%m-%d %H:%M:%S")
| sort - count
Syntax validiert (0 Fehler)
message: "*Im 16 broke and I built a Cursor for Wri*"
Syntax validiert (0 Fehler)
CommonSecurityLog
| where Message has "Im 16 broke and I built a Cursor for Wri"
| summarize EventCount = count(), FirstSeen = min(TimeGenerated), LastSeen = max(TimeGenerated) by SourceIP, DestinationIP, DestinationPort, Activity
| extend DetectionRule = "iShareStuff-CTI-Compiled"
| sort by EventCount desc

2. Cyber Threat Intelligence & Forensik

🎯
MITRE ATT&CK Matrix Navigator 14 Taktiken
Reconnaissance
-
Resource Development
-
Initial Access
Execution
Persistence
-
Privilege Escalation
Defense Evasion
Credential Access
-
Discovery
-
Lateral Movement
-
Collection
-
Command and Control
Exfiltration
-
Impact
tsecurity.de Cognitive Threat RAG
Fokus-Vektor:

Analyse für identifizierte Bedrohung auf Basis von Live-CTI (ENISA EUVD): CVSS 0.0 · EPSS 0.0% · CISA KEV: nein. Handlungsableitung aus den verlinkten Hersteller-Quellen.

🛡️ Angriffsfläche & Exposure

Netzwerk/Remote-Zugriff ohne Vorauthentifizierung möglich.

⚡ Empfohlene Sofortmaßnahmen
  • 1. Perimeter-Inspektion: Relevante Portfreigaben und exponierte Endpunkte unverzüglich scannen.
  • 2. Patch-Applikation: Hersteller-Hotfix einspielen oder betroffene Daemons in isolierte DMZ-Segmente überführen.
  • 3. Telemetrie & EDR-Alerts: Prozessaufrufe und Child-Processes auf anomale Shell-Spawns überwachen.
Ähnliche Beiträge
🔍 Verwandte News

Auch interessante Nachrichten I’m 16, broke, and I built a "Cursor for Writers" using Next.js + Groq ($7 budget)

Thematisch verwandte Begriffe: broke, built, Cursor, Writers · 6 Treffer

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

💬 Kommentare werden geladen…
Zum Aktualisieren ziehen
ZERO-DAY CVE-2026-100739 | A vulnerability was detected in mathurvishal CloudClassroom-PHP-Project…
Advisory →
tsecurity.de Icon
Offline-Lesen, Eilmeldungen & 0ms Ladezeit

Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.

Nächster Beitrag