
Zum Hauptinhalt springen
tsecurity.de LIVE
Echtzeit-Radar & Feeds
Alle RSS Feeds
👥 Community & Social
YouTube Security VideosTechLinked: MacOS 27 launch ain't looking so good(23.09.2026 um 21:00 Uhr)
YouTube Security VideosNeil Patel: Don't Just Be Right. Be Repeatable. #shorts(23.09.2026 um 20:04 Uhr)
YouTube Security VideosMicrosoft Mechanics: How to Share a Copilot Agent With Your Team(23.09.2026 um 20:30 Uhr)
Sicherheitslücken (CVE)USN-8806-1: NetworkManager vulnerability(23.09.2026 um 15:24 Uhr)
Sicherheitslücken (CVE)USN-8807-1: Open-iSNS vulnerability(23.09.2026 um 19:07 Uhr)
Unix & Linux ServerUSN-8808-1: SQL parse vulnerabilities(23.09.2026 um 20:19 Uhr)
YouTube Security VideosTechLinked: MacOS 27 launch ain't looking so good(23.09.2026 um 21:00 Uhr)
YouTube Security VideosNeil Patel: Don't Just Be Right. Be Repeatable. #shorts(23.09.2026 um 20:04 Uhr)
YouTube Security VideosMicrosoft Mechanics: How to Share a Copilot Agent With Your Team(23.09.2026 um 20:30 Uhr)
Sicherheitslücken (CVE)USN-8806-1: NetworkManager vulnerability(23.09.2026 um 15:24 Uhr)
Sicherheitslücken (CVE)USN-8807-1: Open-iSNS vulnerability(23.09.2026 um 19:07 Uhr)
Unix & Linux ServerUSN-8808-1: SQL parse vulnerabilities(23.09.2026 um 20:19 Uhr)
Intelligence View
⚡ tsecurity.de Intelligence

OpenAI Responds to Axios npm Supply Chain Attack, Rotates macOS Certificates

The fallout from the Axios npm supply chain attack continues to widen, with OpenAI issuing a detailed response outlining its exposure and remediation steps. The Axios npm supply chain attack, reported by The Cyber Express on April 1,…

0
↗ Quelle (thecyberexpress.com)
Reagiere als Erste:r — dein Feedback zählt!

Axios npm supply chain attack

The fallout from the Axios npm supply chain attack continues to widen, with OpenAI issuing a detailed response outlining its exposure and remediation steps.

The Axios npm supply chain attack, reported by The Cyber Express on April 1, has since been linked to North Korea’s Lazarus Group, significantly expanding the scope and impact of the incident. Attribution was confirmed by Google Threat Intelligence Group, which identified the activity under UNC1069, a financially motivated group active since at least 2018.

OpenAI Confirms Limited Exposure to Axios npm Supply Chain Attack


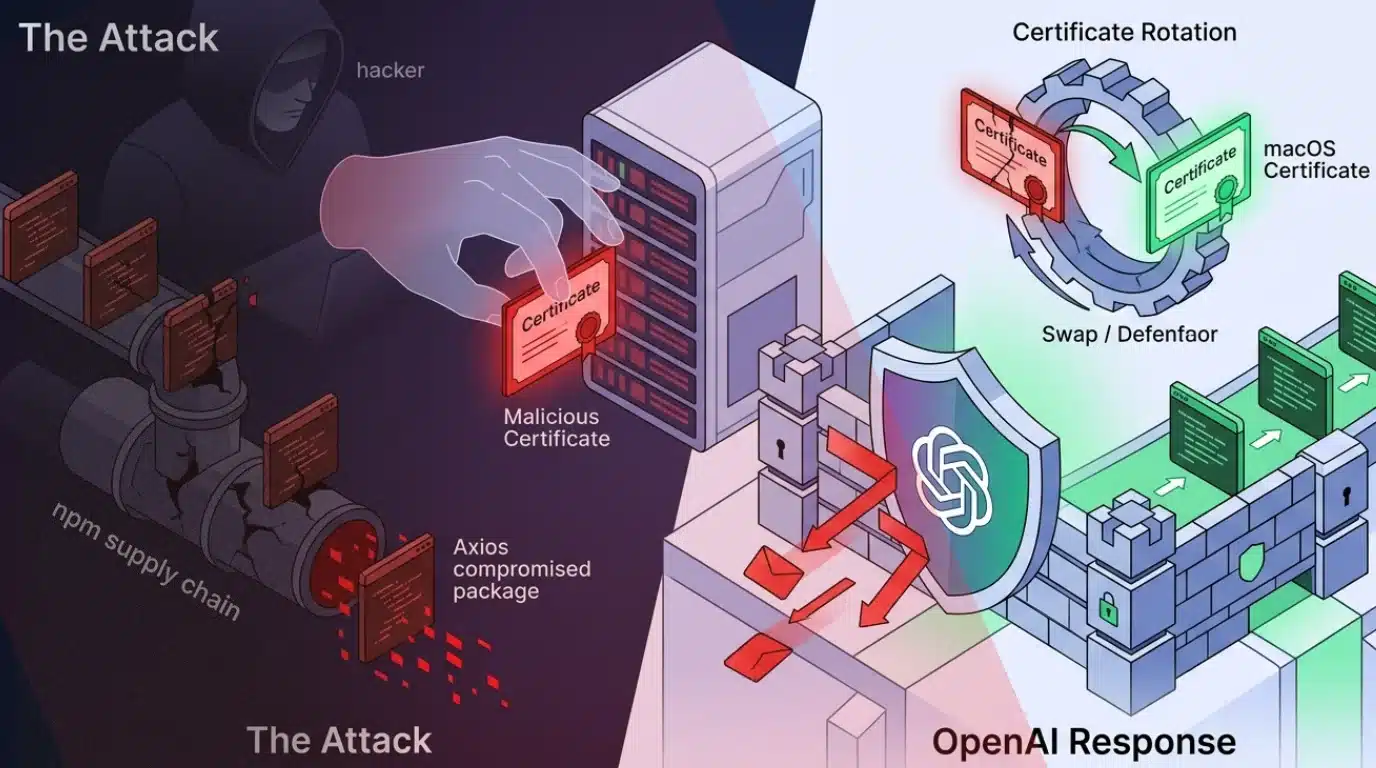
In its official statement, OpenAI said, “We recently identified a security issue involving a third-party developer tool, Axios, that was part of a widely reported, broader industry incident⁠.” The company clarified that while it was affected by the broader Axios npm supply chain attack, there is no evidence of compromise to user data or internal systems.

“We found no evidence that OpenAI user data was accessed, that our systems or intellectual property was compromised, or that our software was altered,” the statement added.

The exposure occurred on March 31, 2026, when a GitHub Actions workflow used in OpenAI’s macOS app-signing process executed a malicious version of Axios (v1.14.1). This workflow had access to sensitive code-signing certificates used for validating OpenAI applications like ChatGPT Desktop, Codex, Codex CLI, and Atlas.

Certificate Rotation and macOS App Updates


As a direct response to the Axios npm supply chain attack, OpenAI has initiated a full rotation of its macOS code-signing certificates. While internal analysis suggests the certificate was likely not exfiltrated, the company is treating it as potentially compromised.

To mitigate any residual risk, OpenAI is requiring users to update their macOS applications. Older versions of affected apps will lose support and functionality after May 8, 2026. Updated versions will carry new certificates to ensure authenticity.

This move is designed to prevent threat actors from distributing malicious software disguised as legitimate OpenAI applications, a known risk in supply chain attacks involving code-signing materials.

Investigation and Security Measures


OpenAI engaged a third-party digital forensics and incident response firm to investigate the impact of the Axios npm supply chain attack. The company also coordinated with Apple to block any new notarization attempts using the old certificate.

Additional steps taken include:

  • Publishing new builds of all affected macOS applications

  • Reviewing all past software notarizations for anomalies

  • Ensuring no unauthorized modifications were made to distributed software


The company confirmed that no malicious applications signed with its certificate have been identified so far.

Root Cause: GitHub Workflow Misconfiguration


The root cause of OpenAI’s exposure to the Axios npm supply chain attack was traced to a misconfiguration in its GitHub Actions workflow. Specifically, the workflow relied on a floating tag instead of a fixed commit hash and lacked a minimum release age for dependencies, both of which increased the risk of pulling compromised packages.

This highlights a broader industry issue where development pipelines remain vulnerable to upstream compromises, especially in open-source ecosystems.

No Impact on User Data or Other Platforms


OpenAI emphasized that the incident is limited strictly to macOS applications. There is no impact on iOS, Android, Windows, Linux, or web-based services.

The company also reassured users:

  • No user data or API keys were compromised

  • No passwords need to be changed

  • No malware signed as OpenAI has been detected


What Happens Next


OpenAI will fully revoke the old certificate on May 8, 2026, after a 30-day transition window. This approach is intended to minimize disruption while ensuring users have adequate time to update their applications.

The company noted that any software signed with the old certificate will be blocked by macOS security protections after revocation, further reducing the risk of misuse.

Growing Impact of Axios npm Supply Chain Attack


The Axios npm supply chain attack highlight the escalating risks tied to third-party software dependencies. With attribution pointing to a state-sponsored group, the incident reflects how supply chain attacks are increasingly being leveraged for financial and strategic objectives.

As organizations continue to rely heavily on open-source libraries, the incident serves as a reminder of the need for stricter dependency management, secure development practices, and continuous monitoring of software pipelines.
CTI Threat Relationship Graph7 Knoten / 6 Relationen
CVE / Incident Software MITRE ATT&CK CWE Weakness IoC
IR-PLAYBOOK-RCE
HIGH
SOC Incident Playbook: Remote Code Execution (RCE) Defense
1-Click Detection Engineering: Sigma & YARA Rules
SOC Ready
title: Detect Exploitation - OpenAI Responds to Axios npm Supply Chain Attack, Rotates macOS Certificates
id: 1a35a6ca-cdf9-4185-b7d0-3971c291e7ac
status: experimental
description: Automatisch generierte SIEM-Erkennungsregel basierend auf CTI Intelligence
references:
  - https://tsecurity.de/
author: iShareStuff CTI Automated Detection Engine
date: 2026-09-23
logsource:
  category: network_connection
  product: any
detection:
  selection:
      CommandLine|contains:
        - 'exploit'
  condition: selection
falsepositives:
  - Legitime administrative Zugriffe oder Penetrationstests
level: high
tags:
  - attack.initial_access
rule CTI_Threat_Indicator {
    meta:
        author = "iShareStuff CTI Automated Detection Engine"
        date = "2026-09-23"
        description = "YARA Signature for "
    strings:
        $str = "OpenAI Responds to Axios npm S" ascii wide
    condition:
        any of them
}
Ähnliche Beiträge
🔍 Verwandte News

Auch interessante Nachrichten OpenAI Responds to Axios npm Supply Chain Attack, Rotates macOS Certificates

Thematisch verwandte Begriffe: OpenAI, Responds, Axios, Supply · 6 Treffer

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Zum Aktualisieren ziehen
ZERO-DAY CVE-2026-90904 | Joomla Extension - joomshaper.com - Broken Access Control (ACL Bypass) i…
Advisory →
TTS Reader • tsecurity.de Voice
tsecurity.de Icon
tsecurity.de App
Offline-Lesen, Eilmeldungen & 0ms Ladezeit

Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.

Nächster Beitrag
Themen-Radar & Intelligence Matrix
Echtzeit-Taxonomie nach Angriffsvektoren & Plattformen

tsecurity.de Live Threat Radar

🔴 LIVE RADAR
MONITORING
AKTIV
CVE-DATENBANK
LIVE
🔍
Community Radar & Live Chat
Sentinel Bot online • Live-Stream
Dein Cluster: Security Explorer
Match:
lädt…
Verbindung zum Community-Stream wird aufgebaut...
Bearbeitungsmodus — Senden überschreibt deine Nachricht
Community-Puls — was gerade passiert
lädt…
Aktivitäten deiner Analysten
lädt…
Neues Thema oder Eilmeldung einreichen

Reiche interessante Links, Zero-Days oder Debatten ein. Die Community entscheidet per Upvote über die Veröffentlichung.

Heiß diskutierte Einreichungen
🔖 Gespeicherte Artikel
📂 Keine gespeicherten Artikel vorhanden.
Zurück Ziehen Vor
Links: vorheriger Artikel Rechts: nächster Artikel unten: schließen
News NIS-2 Frühwarnung Tier-1 Intel TTP ⏱️ 3 Min vor 10 Min
Artikeldaten werden geladen...

Zurück: vorheriger Vor: nächster
↗ Original-Quelle
Social Reaktionen Deine Reaktion zählt
Einstufung & Relevanz-Poll 0 Stimmen
In sozialen Netzwerken teilen 1-Klick