



Cyble Research & Intelligence Labs (CRIL) in its weekly vulnerability report tracked 1,431 bugs last week.
Of these, over 270 vulnerabilities have publicly available Proof-of-Concept (PoC) exploits, significantly accelerating exploitation timelines and increasing real-world attack likelihood.
Additionally, 3 vulnerabilities were actively discussed across underground forums, signaling strong adversarial interest and rapid weaponization.
A total of 130 vulnerabilities were rated critical under CVSS v3.1, while 45 were rated critical under CVSS v4.0, reflecting the severity of disclosed issues.
Furthermore, CISA added 3 vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, confirming active exploitation in the wild.
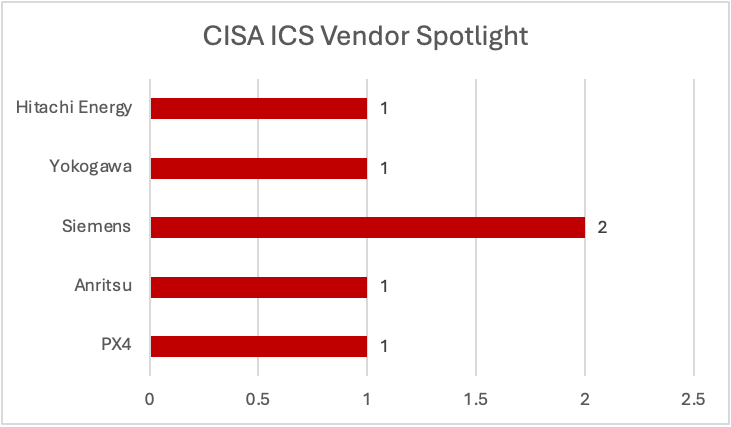
On the industrial front, CISA issued 5 ICS advisories covering 6 vulnerabilities, impacting vendors such as Siemens, Hitachi Energy, and Yokogawa.
Weekly Vulnerability Report’s Top 5 Vulnerabilities
CVE-2026-32213 — Microsoft Azure AI Foundry (Critical)
CVE-2026-32213 is a critical authorization bypass vulnerability in Microsoft Azure AI Foundry.
The flaw exists in the platform’s authorization logic, allowing unauthenticated attackers to bypass security checks and grant themselves administrative privileges. Successful exploitation enables full control over AI environments and associated resources.
CVE-2026-35022 — Claude Code CLI / Agent SDK (Critical)
CVE-2026-35022 is a critical OS command injection vulnerability affecting Anthropic’s Claude Code CLI and Agent SDK.
The vulnerability allows attackers to inject malicious commands into development workflows, resulting in remote code execution and potential compromise of AI pipelines.
CVE-2026-22738 — Spring AI (Critical)
CVE-2026-22738 is a remote code execution vulnerability in Spring AI caused by improper input sanitization in expression evaluation.
Attackers can inject malicious expressions that are executed by the Spring Expression Language, leading to complete application and server compromise.
CVE-2026-4631 — Cockpit (Critical)
CVE-2026-4631 is an unauthenticated remote code execution vulnerability in Cockpit, a web-based Linux server management interface.
The flaw allows attackers to execute arbitrary commands without authentication, potentially leading to full system takeover in enterprise environments.
CVE-2026-35616 — Fortinet FortiClient EMS (Critical)
CVE-2026-35616 is a critical authentication bypass vulnerability in Fortinet FortiClient EMS.
Attackers can bypass authentication and execute arbitrary commands, leading to complete compromise of endpoint management systems.
Vulnerabilities Added to CISA KEV
CISA continues to expand its KEV catalog, reflecting real-world exploitation trends.
Notable addition:
CVE-2026-35616 — Fortinet FortiClient EMS
This vulnerability enables authentication bypass and remote command execution, making it a high-priority remediation target.
The inclusion of enterprise security tools in KEV highlights attackers’ focus on compromising centralized management systems.
Critical ICS Vulnerabilities
CISA issued 5 ICS advisories covering 6 vulnerabilities, many of which impact critical infrastructure environments.
CVE-2026-1579 — PX4 Autopilot (Critical)
A missing authentication vulnerability allowing attackers to execute critical functions without credentials.
This flaw poses risks to autonomous and unmanned systems, potentially enabling unauthorized control.
CVE-2026-3356 — Anritsu Systems (Critical)
This vulnerability involves missing authentication in Anritsu devices, allowing attackers to gain unauthorized access.
CVE-2025-10492 — Hitachi Energy Ellipse (Critical)
A deserialization vulnerability enabling attackers to execute arbitrary code within industrial systems.
Siemens SICAM 8 (Chained Risk)
Two vulnerabilities affecting Siemens SICAM 8 systems—resource exhaustion and out-of-bounds write—can be chained together.
This creates a denial-of-service risk capable of disrupting industrial processes and operational visibility.
CVE-2025-7741 — Yokogawa CENTUM VP (Medium)
A hard-coded password vulnerability that weakens authentication mechanisms and increases risk of unauthorized access.
Critical Infrastructure Sectors Spotlight
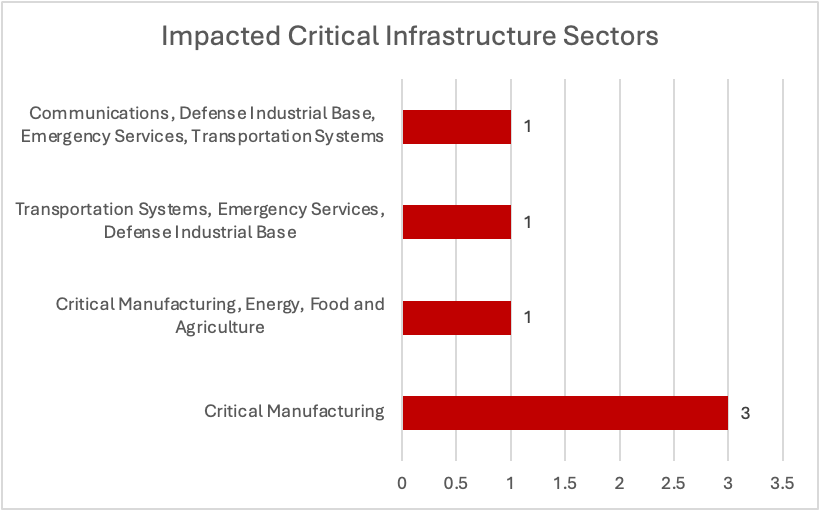
Analysis indicates:
- Critical Manufacturing appears in 66.7% of vulnerabilities
- Cross-sector exposure spans:
- Transportation Systems
- Emergency Services
- Defense Industrial Base
- Communications
This highlights interconnected infrastructure risks, where a single vulnerability can cascade across multiple sectors.
Conclusion
This week’s findings highlight several critical trends:
- Expansion of vulnerabilities into AI and development ecosystems
- Increasing exploitation of enterprise management platforms
- Continued weaknesses in industrial control systems
- Cross-sector risk amplification in critical infrastructure
With 270+ PoCs, KEV-confirmed exploitation, and emerging threats in AI frameworks, organizations face heightened risk across both digital and physical environments.
Key Recommendations
- Prioritize vulnerabilities with PoCs and KEV inclusion
- Secure AI development environments and pipelines
- Patch enterprise management and remote access systems immediately
- Implement strict authentication and access control mechanisms
- Segment IT and OT networks to prevent lateral movement
- Apply compensating controls for unpatched ICS vulnerabilities
- Monitor underground forums and threat intelligence feeds
- Conduct continuous vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations proactively identify risks, prioritize remediation, and detect emerging threats. By integrating intelligence-driven security strategies, organizations can strengthen resilience across enterprise and critical infrastructure environments.
The post The Week in Vulnerabilities: Azure AI, Spring AI, Fortinet, and Critical ICS Exposure appeared first on Cyble.
SOCIAL SHARE CARD GENERATOR