




The activity has been linked to the Russian General Staff Main Intelligence Directorate’s Unit 26165, widely tracked in the cybersecurity community as APT28 or Fancy Bear.
According to the advisory, the Russian GRU cyber campaign has been active since early 2022 and continues to evolve, posing a sustained risk to organizations across multiple sectors.
Security agencies warn that companies involved in transportation, IT services, and defense supply chains should assume they are potential targets and strengthen monitoring and threat detection efforts.
GRU Unit 26165 Expands Logistics Cyber Targeting
The campaign, attributed to GRU Unit 26165, has focused on entities supporting Ukraine through logistics and infrastructure. This includes companies operating across air, sea, and rail transport, as well as IT service providers connected to these operations.
Targets span multiple countries, including the United States, Germany, Poland, France, and Ukraine. The attackers have also exploited trust relationships between organizations, moving from one compromised entity to another to expand access.
[caption id="attachment_111431" align="aligncenter" width="600"]
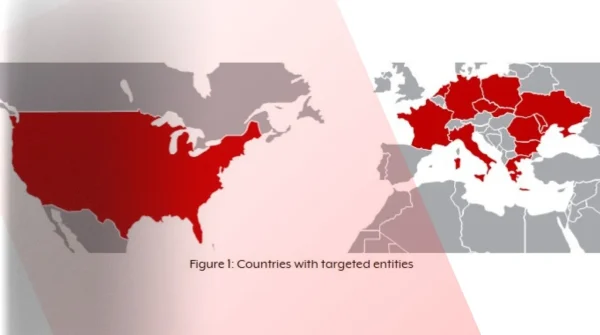 Image source: https://www.cyber.gov.au/[/caption]
Officials noted that the Russian GRU cyber campaign is not limited to direct targets. Organizations with business ties to logistics providers have also been drawn into the attack chain, increasing the overall risk surface.
APT28 Attacks Use Known but Effective Techniques
The advisory highlights that APT28 attacks rely heavily on established tactics, techniques, and procedures. These include credential guessing, brute-force attacks, and spearphishing campaigns designed to steal login details or deploy malware.
Spearphishing remains a key component of the Russian GRU cyber campaign, with emails crafted in the target’s native language and often impersonating government or trusted services. Many of these emails direct victims to fake login pages hosted on compromised devices or free web platforms.
The attackers have also used multi-stage redirect systems to filter victims based on location and device characteristics, making detection more difficult.
CVE Exploitation and Malware Deployment Observed
A significant aspect of the campaign involves the exploitation of known vulnerabilities. The actors have weaponized multiple CVEs, including:
- CVE-2023-23397 in Microsoft Outlook to harvest credentials
- Roundcube vulnerabilities for email server access
- CVE-2023-38831 in WinRAR for remote code execution
These vulnerabilities have enabled attackers to gain initial access and move deeper into targeted networks. The Russian GRU cyber campaign also involves malware such as HEADLACE and MASEPIE, which are used for persistence and data exfiltration.
Post-Compromise Activity Focuses on Sensitive Data
Once inside a network, attackers conduct extensive reconnaissance to identify high-value targets, including employees managing transport operations and cybersecurity teams.
The Russian GRU cyber campaign places particular emphasis on accessing sensitive logistics data. This includes shipment details such as routes, cargo contents, sender and recipient information, and transport schedules.
Attackers use tools like Remote Desktop Protocol and open-source frameworks to move laterally within networks. They also manipulate email permissions to maintain long-term access and collect communications from compromised accounts.
IP Cameras Targeted to Track Aid Movement
In addition to corporate networks, the campaign has extended to internet-connected cameras. The advisory reports that GRU actors have targeted IP cameras located near border crossings, rail stations, and military facilities.
By exploiting weak credentials and unsecured Real Time Streaming Protocol servers, attackers have been able to access live feeds and monitor the movement of aid into Ukraine. A large portion of these attempts has focused on cameras in Ukraine and neighboring countries.
This tactic adds a physical surveillance dimension to the Russian GRU cyber campaign, enabling real-time tracking of logistics operations.
Organizations Urged to Strengthen Defenses
Cybersecurity agencies are urging organizations to take immediate steps to mitigate risks associated with the Russian GRU cyber campaign. Recommended measures include:
- Enforcing multi-factor authentication and strong access controls
- Monitoring for unusual login activity and lateral movement
- Patching known vulnerabilities and securing internet-facing systems
- Limiting access to critical infrastructure and sensitive data
- Auditing logs and deploying endpoint detection tools
Companies are also advised to review their relationships with partners and suppliers, as attackers frequently exploit these connections to expand their reach.
Persistent Threat Expected to Continue
The advisory concludes that the Russian GRU cyber campaign is likely to persist, with continued use of similar tactics and targeting patterns. As geopolitical tensions remain high, logistics and technology sectors are expected to stay at the forefront of cyber espionage activity.
Organizations operating in these sectors are being encouraged to adopt a proactive security posture, recognizing that the threat is ongoing and highly targeted.