
Zum Hauptinhalt springen
Echtzeit-Radar & Feeds
Alle RSS Feeds ➔
👥 Community & Social
Windows Tipps & SecurityCrystal Display Systems übernimmt Assets von Display & Control(29.09.2026 um 13:20 Uhr)
•
Windows Tipps & SecurityDFB und ZVEI veröffentlichen Leitfaden zur Stadionbeschallung(29.09.2026 um 13:30 Uhr)
•
Sicherheitslücken (CVE)DSA-6528-1 linux - security update(29.09.2026 um 02:00 Uhr)
••
Sichere ProgrammierungCronflower: Turn a Spring Boot app into a distributed cron cluster(29.09.2026 um 13:32 Uhr)
•
Sichere ProgrammierungRetry Is Not Recovery: A Practical Failure Model for Odoo Integrations(29.09.2026 um 13:33 Uhr)
•
Sichere ProgrammierungOne Rails App, Multiple Customers(29.09.2026 um 13:33 Uhr)
•
Sichere ProgrammierungHello dev.to! Here is my BenchmarkingRealWork series case 01.(29.09.2026 um 13:34 Uhr)
•
Sichere ProgrammierungHow to Automatically Turn Voice Notes Into To-Dos on Your Mac in 2026(29.09.2026 um 13:36 Uhr)
••
Intelligence View
⚡ tsecurity.de Intelligence

March 2026 Cyber Threat Landscape Fueled by Ransomware, Breaches, and Access Markets

The 2026 threat landscape continued to intensify in March, with ransomware attacks, expanding data breach activity, and a growing underground market for compromised access shaping the global cybersecurity environment. According to analysis …

0
↗ Quelle (thecyberexpress.com)
Reagiere als Erste:r — dein Feedback zählt!

2026 threat landscape

The 2026 threat landscape continued to intensify in March, with ransomware attacks, expanding data breach activity, and a growing underground market for compromised access shaping the global cybersecurity environment. According to analysis from CRIL (Cyble Research & Intelligence Labs), organizations worldwide faced a highly active and coordinated threat ecosystem throughout the month. 

CRIL’s findings point to a cybercriminal landscape driven by financial extortion, credential theft, and operational disruption. Attackers consistently targeted industries that rely heavily on uptime or store large volumes of sensitive data, reinforcing the urgency for stronger defensive strategies. 

Ransomware Attacks Dominate the 2026 Threat Landscape 
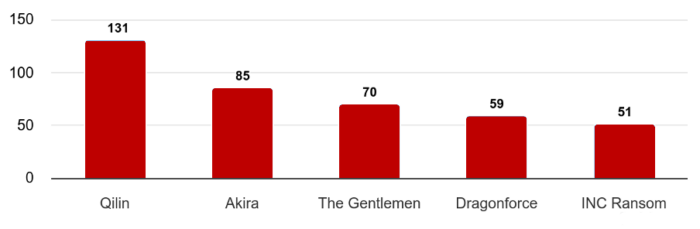

Top five ransomware actors (Data Source: Cyble Blaze AI)

One of the most defining aspects of the March 2026 threat landscape was the scale of ransomware attacks. CRIL recorded 702 ransomware incidents globally, underscoring the continued dominance of ransomware as a primary attack vector. 

Among the most active threat groups were Qilin, Akira, The Gentlemen, Dragonforce, and INC Ransom. Collectively, these actors were responsible for over 56% of all observed ransomware activity, reflecting their operational maturity and extensive affiliate networks. 

Industries most affected by ransomware attacks included: 

  • Construction  

  • Professional Services  

  • Manufacturing  

  • Healthcare  

  • Energy & Utilities  


Attackers frequently employed double-extortion tactics, combining data theft with system disruption to increase pressure on victims. Geographically, the United States remained the primary target, influenced in part by ongoing geopolitical tensions, including those involving Iran. 

Rise of Access Brokers in the CRIL Threat Analysis 


Another notable trend in the 2026 threat landscape, as identified by CRIL, was the continued growth of the compromised access market. During March, 20 separate incidents involving the sale of unauthorized network access were tracked across cybercrime forums. 

The most targeted sectors for access sales were: 

  • Professional Services (25%)  

  • Retail (20%)  

  • IT & ITES  

  • Manufacturing  


A small group of threat actors, vexin, holyduxy, and algoyim, dominated this space, accounting for more than 55% of observed listings. These access brokers play a critical upstream role, enabling ransomware attacks, espionage campaigns, and financial fraud operations. 

Data Breaches and Leak Markets Stay Active 


CRIL also documented 54 significant data breach and leak incidents in March, further highlighting the scale of data exposure risks in the current 2026 threat landscape. 

The most targeted sectors for data breaches included: 

  • Government & Law Enforcement  

  • Retail  

  • Technology  


Several incidents stood out: 

  • A threat actor known as “nightly” claimed to have stolen over 5TB of data from Hospitality Holdings, including biometric data, CCTV footage, and financial records. 

  • Another actor, XP95, advertised 3.8TB of allegedly stolen South African government data for sale.  

  • A separate breach exposed more than 95,000 travel-related records, including passport and payment information.  


Exploitation of Critical Vulnerabilities Accelerates 


The 2026 threat landscape also saw increased exploitation of critical vulnerabilities, particularly those listed in CISA’s Known Exploited Vulnerabilities (KEV) catalog. 

Key vulnerabilities targeted included: 

  • CVE-2026-20131 (Cisco Secure Firewall Management Center)  

  • CVE-2025-53521 (F5 BIG-IP APM)  

  • CVE-2026-20963 (Microsoft SharePoint Server)  

  • CVE-2026-33017 (Langflow AI)  

  • CVE-2021-22681 (Rockwell Automation ICS)  


CRIL observed attackers exploiting both newly disclosed zero-day vulnerabilities and older, unpatched flaws. This trend reflects persistent gaps in patch management and exposure mitigation across organizations. 

Emerging Threat Developments in March 2026 


Beyond ransomware attacks and data breaches, CRIL identified several strategic developments shaping the 2026 threat landscape: 

  • AI-Driven Attacks: Threat actors reportedly leveraged an open-source framework called CyberStrikeAI to target Fortinet FortiGate devices across 55 countries, compromising more than 600 systems. 

  • Supply Chain Risks: North Korean-linked actors were associated with 26 malicious npm packages distributing remote access trojans (RATs) via infrastructure hosted on Pastebin and Vercel. 

  • Geopolitical Cyber Activity: Iran-linked cyber operations are expected to increase, with potential ransomware attacks and hacktivist campaigns targeting organizations in the Middle East. 

2. Cyber Threat Intelligence & Forensik

IoC Intelligence (5 Indikatoren)
CVE-2026-20131CVE-2025-53521CVE-2026-20963CVE-2026-33017CVE-2021-22681
CTI Threat Relationship Graph8 Knoten / 7 Relationen
CVE / Incident Software MITRE ATT&CK CWE Weakness IoC
Exploit & Remediation Lifecycle Timeline
CVE-2021-22681
Entdeckung & Meldung
Schwachstelle identifiziert & registriert
Sicherheits-Advisory
Offizielle Warnung & CVE-Zuweisung
Exploit / PoC
Bislang kein öffentlicher Exploit
In-the-Wild Ausnutzung
Aktive Angriffe beobachtet (CISA KEV / EPSS)
Patch & Schutzmaßnahmen
Upstream-Patch-Referenz vorhanden (Commit-/Advisory-Link)
Exploit Weaponization & Public PoC Radar
CRITICAL WEAPONIZED · Index 75/100
Exploit-DB
Kein EDB-Eintrag
Interaktion
0-Click
Authentifizierung
Nicht erforderlich

3. Compliance, SLA & Vendor Adherence

CVSS 9.8CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H
Impact: 5.87 | Exploitability: 3.89
AVN
Netzwerk (Remote)
Aus der Ferne über das Internet ohne Vorbedingungen exploitbar.
ACL
Niedrig (Low)
Wiederholbar und deterministisch ohne spezielle Race Conditions ausnutzbar.
PRN
Keine (Unauthenticated)
Vollständig unauthentifiziert ohne Benutzerkonto exploitbar.
UIN
Keine (Zero-Click)
Autonom ohne menschliches Zutun ausführbar (Zero-Click Exploitation).
SU
Unverändert (Scope Unchanged)
Auswirkungen verbleiben isoliert in der angreifbaren Anwendungskomponente.
CH
Hoch (Totaler Abfluss)
Vollständiger Zugriff auf alle sensiblen Datenbank- und Speicherinhalte.
IH
Hoch (Volle Manipulation)
Vollständige Modifikation von Dateien, Parametern oder Ausführung von Code.
AH
Hoch (Totaler Ausfall / DoS)
Dienst oder Server wird komplett unbrauchbar (Denial of Service).
CISA-SSVC-Triage (vulnrichment)CVE-2026-20131
Exploitation: active (Aktiv ausgenutzt)Automatable: yes (Automatisierbar)Technical Impact: total (Vollständig)
Quelle: CISA-ADP vulnrichment · Stand 2026-03-19T15:44:02.644612Z · CISA Coordinator
Advisory Radar

Hersteller-Sicherheitsmeldungen & Patch-Status

Offizielles Hersteller-Update verfügbar
Handlungsempfehlung für Administratoren

Hersteller hat ein verifiziertes Patch-Release herausgegeben. Sofortiges Rollout auf Test- und Produktivsystemen empfohlen.

Referenzen aus der Primärquelle („Verifiziert" nur bei Hersteller-Domäne):
Ähnliche Beiträge
🔍 Verwandte News

Auch interessante Nachrichten March 2026 Cyber Threat Landscape Fueled by Ransomware, Breaches, and Access Markets

Thematisch verwandte Begriffe: March, 2026, Cyber, Threat · 6 Treffer

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

💬 Kommentare werden geladen…
Zum Aktualisieren ziehen
ZERO-DAY CVE-2026-102247 | A vulnerability was detected in FastAdmin 1.6.1.20250430/1.6.5.20260602…
Advisory →
tsecurity.de Icon
Offline-Lesen, Eilmeldungen & 0ms Ladezeit

Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.

Nächster Beitrag