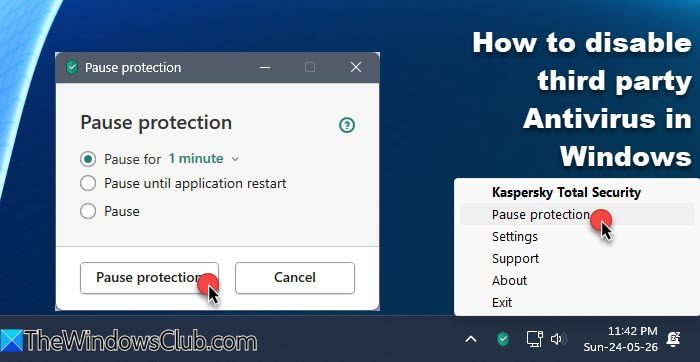
How to disable third party Antivirus in Windows 11
In this guide, we will show you how to disable popular third-party antivirus software in Windows 11, like McAfee, Norton, Avast, AVG, Quick Heal, Avira, Bitdefender, Kaspersky, Eset, Trend Micro, Malwarebytes and K7 Computing. Antivirus…
In this guide, we will show you how to disable popular third-party antivirus software in Windows 11, like McAfee, Norton, Avast, AVG, Quick Heal, Avira, Bitdefender, Kaspersky, Eset, Trend Micro, Malwarebytes and K7 Computing. Antivirus protection is essential for protecting your computer from malware, ransomware, and other online threats. However, antivirus software may sometimes flag […]
title: Detect Exploitation - How to disable third party Antivirus in Windows 11
id: a472a695-08ed-4b16-b680-57ed5a1ab433
status: experimental
description: Automatisch generierte SIEM-Erkennungsregel basierend auf CTI Intelligence
references:
  - https://tsecurity.de/
author: iShareStuff CTI Automated Detection Engine
date: 2026-09-26
logsource:
  category: network_connection
  product: any
detection:
  selection:
      CommandLine|contains:
        - 'exploit'
  condition: selection
falsepositives:
  - Legitime administrative Zugriffe oder Penetrationstests
level: high
tags:
  - attack.initial_access
  - attack.t1486
Syntax validiert (0 Fehler)
rule CTI_Threat_Indicator {
    meta:
        author = "iShareStuff CTI Automated Detection Engine"
        date = "2026-09-26"
        description = "YARA Signature for "
    strings:
        $str = "How to disable third party Ant" ascii wide
    condition:
        any of them
}
Syntax validiert (0 Fehler)
index=security sourcetype IN ("cisco:asa", "pan:traffic", "zeek_conn", "suricata", "WinEventLog:Security")
("How to disable third party Antivirus in ")
| stats count earliest(_time) as first_seen latest(_time) as last_seen by src_ip, dest_ip, dest_host, signature
| eval first_seen=strftime(first_seen, "%Y-%m-%d %H:%M:%S"), last_seen=strftime(last_seen, "%Y-%m-%d %H:%M:%S")
| sort - count
Syntax validiert (0 Fehler)
message: "*How to disable third party Antivirus in *"
Syntax validiert (0 Fehler)
CommonSecurityLog
| where Message has "How to disable third party Antivirus in "
| summarize EventCount = count(), FirstSeen = min(TimeGenerated), LastSeen = max(TimeGenerated) by SourceIP, DestinationIP, DestinationPort, Activity
| extend DetectionRule = "iShareStuff-CTI-Compiled"
| sort by EventCount desc
Kognitive Analyse für identifizierte Bedrohung: Erhöhte Bedrohungslage im Bereich How to disable third party Antivirus in .... Basierend auf 368k Vektor-Korrelationen werden sofortige Isolationsmaßnahmen für betroffene Endpunkte empfohlen.
🛡️ Angriffsfläche & Exposure
Netzwerk/Remote-Zugriff ohne Vorauthentifizierung möglich.
⚡ Empfohlene Sofortmaßnahmen
1. Perimeter-Inspektion: Relevante Portfreigaben und exponierte Endpunkte unverzüglich scannen.
2. Patch-Applikation: Hersteller-Hotfix einspielen oder betroffene Daemons in isolierte DMZ-Segmente überführen.
3. Telemetrie & EDR-Alerts: Prozessaufrufe und Child-Processes auf anomale Shell-Spawns überwachen.
🔗 Semantisch verwandte Zero-DaysMariaDB 11.7 VEC
Synthetische RAG-Antwort
EDB-ID 51234
CVE-ADVISORY
RISK: HIGH
⚠️DEFANGED SANDBOX VIEW (tsecurity.de): Alle Netzwerkindikatoren und URLs wurden neutralisiert (2 Indikatoren entschärft). Nur zur defensiven Analyse!
Video von heise & c't auf YouTube: Wollt ihr auch unabhängig von Google Maps werden? In diesem Video stellen wir euch drei Alternativen vor. ► Zum Artikel…
Video von heise & c't auf YouTube: Wollt ihr auch unabhängig von Google Maps werden? In diesem Video stellen wir euch drei Alternativen vor. ► Zum Artikel…



 In this guide, we will show you how to disable popular third-party antivirus software in Windows 11, like McAfee, Norton, Avast, AVG, Quick Heal, Avira, Bitdefender, Kaspersky, Eset, Trend Micro, Malwarebytes and K7 Computing. Antivirus protection is essential for protecting your computer from malware, ransomware, and other online threats. However, antivirus software may sometimes flag […]