
The FIFA World Cup 2026 kicks off on June 11, and the world's biggest sporting event is drawing more than just fans — it is already attracting a wave of cybercriminals targeting ticket buyers, job seekers, streaming viewers, and corporate brands alike.
The FBI has issued a formal Public Service Announcement warning that threat actors are creating fraudulent versions of FIFA-affiliated websites to steal personal information, conduct financial fraud, and sell fake products and services. Cyble researchers independently analyzed the domains flagged by the FBI and confirmed that many remained active and operational at the time of publishing this report.
With 48 teams, 16 host cities across the United States, Canada, and Mexico, and an estimated global audience of billions, the FIFA World Cup 2026 is set to be the largest men's World Cup in history. That scale is precisely why cybercriminals are prying on it — and why the threat is arriving earlier and more aggressively than in previous tournaments.
How FIFA World Cup 2026 Scams Work
The FBI warns that threat actors are building fraudulent versions of FIFA's official website, www.fifa.com, designed to closely mimic the legitimate experience. These sites are engineered to collect personally identifiable information (PII), including full names, home addresses, phone numbers, email addresses, banking information, and payment card details.
The same fraudulent infrastructure is used to run a range of operations simultaneously: FIFA ticket scams, fake hospitality package sales, fraudulent job listings, and other forms of financial fraud.
The most common technical method is typosquatting — registering domains with subtle spelling changes or different extensions that trick users into believing they have landed on an official page. A single missing letter, a swapped extension, or a hyphenated variant can be enough to deceive even vigilant users, especially when the site is dressed with FIFA branding, tournament schedules, and professional-looking navigation menus.
The FBI flagged the following domains as fraudulent FIFA-related sites:
| www.fifa[.]cab | www.fifa[.]pink |
| www.fifa[.]blue | www.fifa[.]pub |
| FIFA[.]city | Fifa[.]bio |
| fifa[.]beer | fifa[.]click |
| fifa[.]cam | fifa[.]ceo |
| fifa[.]help | filfa[.]org |
| fifa-online[.]com | https://fifa-2026[.]xyz |
| jobs-fifa[.]com | fifa-hr[.]com |
| fifa-careerhub[.]com | fifaworldcup-careers[.]com |
| fifa-hiring[.]com | fifahiring[.]com |
| fifa-ticket[.]live | fifastore.us[.]com |
| fifaworldcup26[.]sale | fifaworldcup26.xcover-staging[.]com |
| worldcup2026-tickets.com[.]mx | worldcup26ticket[.]com |
| 2026fifaworldcuptickets[.]online | fwc2026[.]net |
| fwc2026.web[.]app | www.fifa2026p[.]com |
| fifa2026fworldcup[.]com | wvvw-fifa[.]com |
| ww-fifa[.]com | fifa-com[.]com |
| www.fifa-com[.]services | quiniela-fifa-2026.pages[.]dev |
Source: FBI PSA — Domains defanged for safety
Cyble researchers tracked these domains and confirmed that many were still operational at the time of publishing. Notably, even when a malicious domain is taken down, new ones tend to appear almost instantaneously. The fraudulent infrastructure is not a one-time campaign — it is continuously regenerating.
Fake FIFA Hospitality, Ticket, and Sale Sites
One of the most convincing examples identified by Cyble researchers was ww-fifa[.]com — a classic typosquatting attack that removes a single "w" from the legitimate FIFA URL. The site presents itself as an official FIFA World Cup 2026 portal, complete with tournament branding, navigation menus, ticket information, and hospitality package offers.
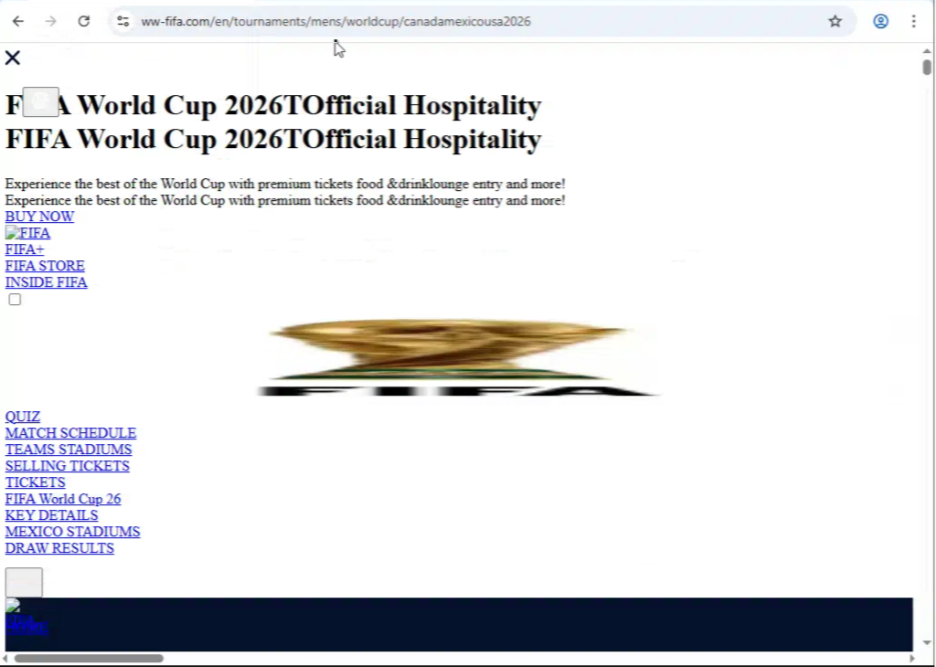
Visitors to this site are encouraged to purchase premium packages that include tickets, food, beverages, lounge access, and related services — all fraudulent.
Cyble researchers identified several indicators that expose the site as illegitimate:
- Duplicate page titles appearing twice in the browser tab
- Missing or broken images throughout the site
- Navigation links leading to attacker-controlled pages
- Ticket purchase prompts requesting personal and financial information with no legitimate payment processing
What makes these sites especially dangerous is the sophistication of the presentation. Unlike the crude phishing pages of a decade ago, modern FIFA 2026 scam sites replicate the visual design of official sports portals convincingly enough to pass a casual inspection.
Security Vendors Have Already Flagged FIFA-Related Domains
Cyble researchers analyzed the domain fifa[.]help using VirusTotal and found that, at the time of analysis, 15 out of 92 security vendors had classified it as malicious. Vendor classifications included phishing, fraud, and related threat categories.
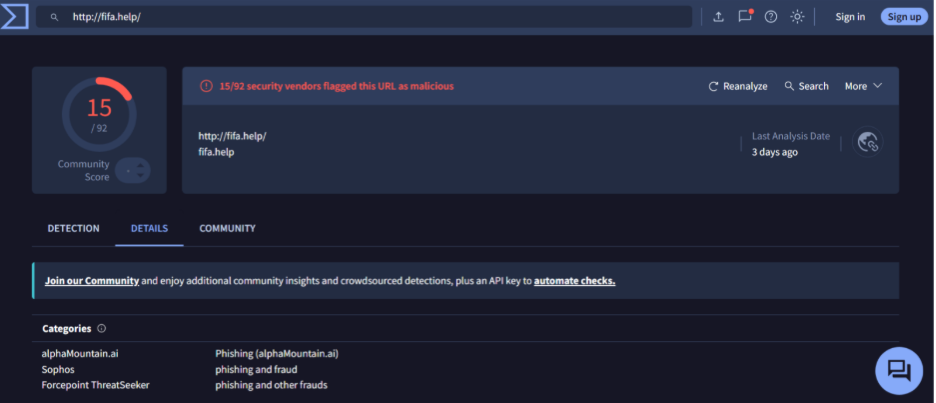
While a detection rate of 15/92 may seem modest, it represents significant early-stage flagging. Many security vendors lag in classifying newly registered domains, so the fact that multiple established providers had already flagged this domain confirms a credible threat.
As these domains age and accumulate more malicious activity reports, detection rates will rise — but by then, victims will already have been targeted.
Fake FIFA Recruitment Sites Are Also Active
Not all FIFA World Cup 2026 scams target ticket buyers or fans. Cyble researchers identified an entirely separate fraud vector targeting job seekers: the domain fifaworldcup-careers[.]com, which presents itself as a FIFA employment portal for World Cup-related positions.

VirusTotal data revealed:
- www.fifaworldcup-careers[.]com was flagged by 8 out of 91 vendors
- The root domain was flagged by 14 out of 91 vendors
- The domain resolved to multiple IP addresses, including 3.71.180.249, 13.249.91.65, and 13.249.91.101
The use of multiple IP addresses suggests the domain may be operating behind content delivery or load-balancing infrastructure, which makes takedowns significantly more difficult to execute.
WHOIS data shows the domain was registered and updated in mid-to-late April 2026, with the registrant's identity hidden behind a privacy shield. Two SSL certificates were also issued on April 15 and April 16, including a wildcard certificate covering *.fifaworldcup-careers[.]com — a sign of deliberate, technically capable infrastructure setup rather than an opportunistic amateur operation.
Why this matters: Job seekers searching for World Cup-related employment — hospitality roles, security staff, event coordinators, media positions — are a highly vulnerable and largely overlooked audience. These individuals are not on guard for ticket scams; they are in application mode, and they will willingly submit full personal information, resumes, and even government ID to what they believe is a legitimate employer.
How to Avoid FIFA World Cup 2026 Ticket Scams
As fans search for how to watch the FIFA World Cup 2026 or purchase tickets, the FBI recommends the following precautions:
- Type fifa.com directly into your browser's address bar — never rely on search results or links in messages
- Avoid sponsored search results, which can be purchased by attackers to appear above legitimate results
- Confirm that the URL is exactly www.fifa.com before entering any information
- Use saved bookmarks or browser favorites when revisiting FIFA websites
- Access FIFA subdomains only through the official homepage, not by typing them directly
- Be cautious of websites with broken graphics, poor-quality branding, or duplicate content
- Do not provide sensitive information unless the site's legitimacy has been independently verified
- Review URLs carefully before clicking any advertisements
These steps are especially important for avoiding FIFA 2026 ticket price scams, where attackers create a false sense of urgency through fake discounts, exclusive hospitality offers, or limited-time deals that pressure users into making fast payment decisions.
How to Watch FIFA World Cup 2026 Safely
Scammers are targeting not only ticket buyers but viewers as well. Fraudulent streaming platforms are expected to proliferate as the tournament approaches, exploiting the high demand for match access — particularly from fans in regions where official broadcasts are expensive or limited.
To reduce risk when looking for FIFA World Cup 2026 streaming options:
- Use only official FIFA channels and licensed regional broadcasters for tournament information
- Watch matches exclusively through broadcasters licensed for your region
- Avoid streaming links shared through unsolicited emails, social media messages, or WhatsApp groups
- Verify URLs carefully before creating accounts or entering any payment information
- Be cautious of websites offering heavily discounted subscription packages or "exclusive" access to all matches
Many fake streaming platforms use the same tactics seen in FIFA ticket scams: they exploit demand for tournament content to harvest personal and financial information, either immediately or through credential-stuffing attacks down the line.
What To Do If You Become a Victim of a FIFA World Cup 2026 Scam
The FBI expects additional spoofed domains to appear throughout the tournament period — before, during, and after matches. If you encounter a suspected FIFA World Cup 2026 scam, document as much information as possible before the site disappears, including:
- The fraudulent domain name
- Screenshots of the website
- Any communication records (emails, SMS, chat logs)
- Payment details if a transaction occurred
- Cryptocurrency wallet addresses, if applicable
Victims can file a complaint with the Internet Crime Complaint Center (IC3) at ic3.gov and should include the fake domain involved, details of all interactions with the site, information submitted to the scammers, payment records, receiving financial institution information, and any cryptocurrency transaction details.
Reporting promptly not only helps your case but also contributes to the broader effort to get these domains flagged and taken down faster.
Protect Your Brand from Fake FIFA World Cup 2026 Phishing Campaigns
Major global events like the FIFA World Cup create a concentrated window of opportunity for cybercriminals to launch phishing campaigns, register fraudulent domains, and impersonate trusted brands. As the active FIFA-related scam infrastructure identified by Cyble researchers demonstrates, this is not a theoretical risk — it is a live and expanding threat landscape.
Organizations operating in travel, hospitality, ticketing, media, and any sector adjacent to the FIFA World Cup 2026 need proactive brand protection measures in place now — not after the first incident.
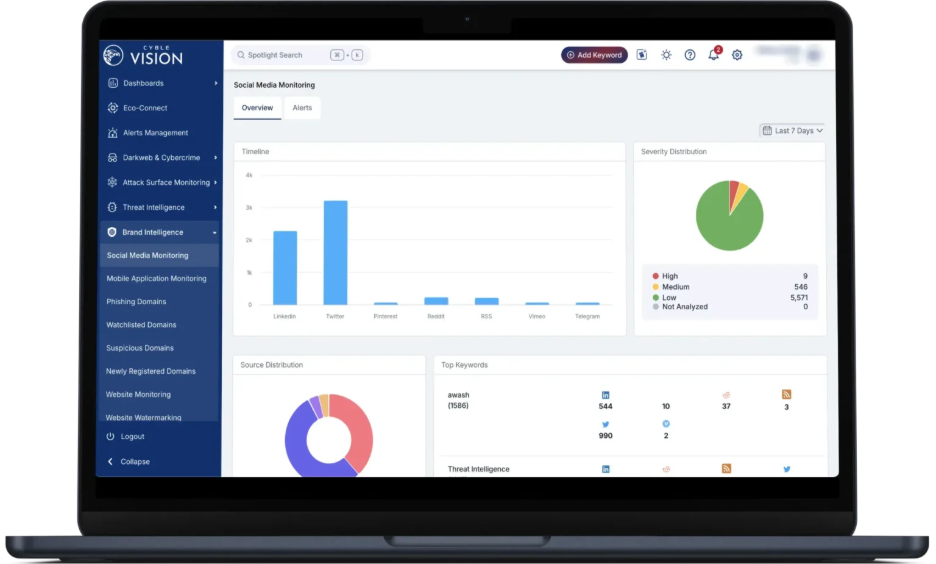
Cyble's Brand Intelligence solution helps organizations detect malicious domains, phishing websites, brand impersonation attempts, and other forms of digital abuse in real time. Combined with Dark Web and Cyber Crime Monitoring and Takedown & Disruption services, security teams can identify threats early, investigate malicious activity, and accelerate the removal of fraudulent infrastructure before it causes financial or reputational damage.
Don't react — deploy now.
Check out how Cyble helps organizations detect, monitor, and disrupt phishing campaigns, fraudulent domains, and brand abuse before they lead to financial loss or reputational damage.
Frequently Asked Questions
1. How do I know if a FIFA World Cup 2026 ticket website is legitimate?
2. Are FIFA World Cup 2026 jobs being posted on fake websites?
3. What should I do if I accidentally visited a fake FIFA site?
4. Can I safely use Google to search for FIFA World Cup 2026 tickets?
5. How many fake FIFA 2026 domains are there?
The post FIFA World Cup 2026 Scams Are Already Active: Fake Domains, Phishing Sites, and How to Stay Safe appeared first on Cyble.
SOCIAL SHARE CARD GENERATOR