



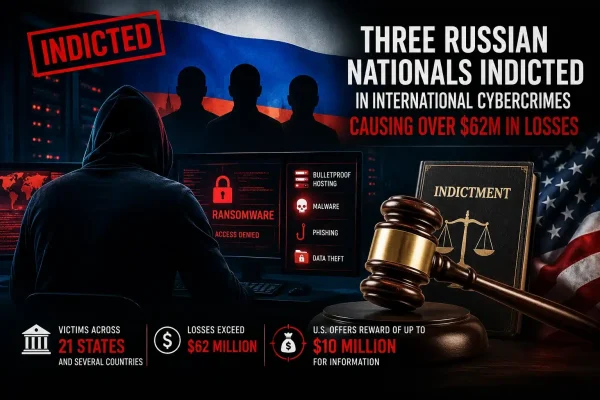
Three Russian nationals have been charged in a sweeping Russian cybercrime indictment tied to an alleged bulletproof hosting operation that U.S. authorities say enabled ransomware, malware, phishing, and other cybercriminal activities, resulting in more than $62 million in losses to victims across the United States and several other countries.
The U.S. Attorney's Office for the Northern District of Ohio announced the unsealing of the indictment following a seven-year investigation. Alongside the criminal charges, the U.S. Department of State is offering a reward of up to $10 million for information on foreign government-linked associates connected to the operation.
Three Russian Nationals and Two Companies Indicted
A federal grand jury returned the indictment in December 2024 against:
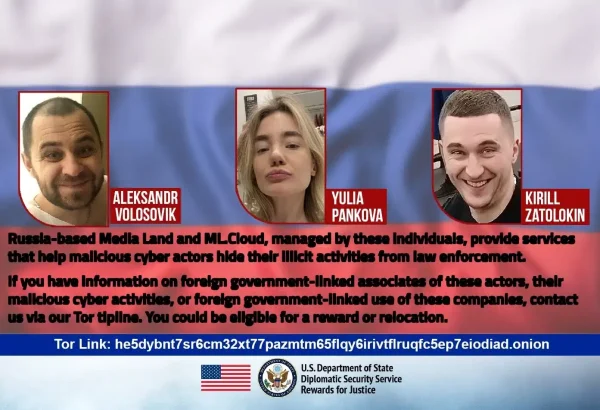
- Alexander Alexandrovich Volosovik, 43, of St. Petersburg, Russia
- Kirill Andreevich Zatolokin, 34, of St. Petersburg, Russia
- Yulia Vladimirovna Pankova, 29, of St. Petersburg, Russia
- Media Land LLC
- ML.Cloud LLC
The defendants face charges including conspiracy to commit computer fraud, wire fraud, money laundering, and aiding cybercriminal activities.
Assistant Attorney General A. Tysen Duva said the defendants allegedly operated criminal infrastructure from overseas that supported attacks against U.S. critical institutions and placed the public at risk.
Bulletproof Hosting Allegedly Enabled Cybercrime Operations
According to court documents, Media Land, owned by Volosovik, and ML.Cloud, owned by Pankova, provided internet infrastructure and server hosting services designed to help cybercriminals evade law enforcement.
Authorities allege the companies operated from St. Petersburg while maintaining infrastructure in multiple countries, including China, Finland, the Netherlands, and the United States.
The businesses allegedly offered bulletproof hosting services that enabled criminal clients to deploy malware and ransomware, extort victims for money and cryptocurrency, register fraudulent domains, operate criminal marketplaces, and launch phishing and brute-force attacks.
Investigators said the companies also provided technical support to cybercriminal customers, allowing malicious campaigns to continue while avoiding detection.
Victims Spanned Critical Sectors Across 21 States
Officials said the operation targeted dozens of organizations across 21 U.S. states as well as multiple countries.
Victims included:
- Banks
- Schools
- Government entities
- Hospitals
- Media companies
Communities affected in Ohio included Akron, Brookfield, Canton, Cleveland, Elyria, Medina, Findlay, Solon, and Valley View.
Additional affected states included California, Florida, Georgia, Illinois, Louisiana, Maryland, Massachusetts, Michigan, Minnesota, New Hampshire, New York, North Carolina, Pennsylvania, Tennessee, Texas, Utah, Virginia, Washington, Wisconsin, and Delaware.
International victims were identified in Australia, Canada, the European Union, the United Arab Emirates, and the United Kingdom.
FBI Cyber Division Assistant Director Brett Leatherman said Media Land enabled malicious activity that caused tens of millions of dollars in losses while impacting victims across multiple countries.
Russian Cybercrime Indictment Prompts $10 Million Reward Offer
The U.S. Department of State's Rewards for Justice program announced a reward of up to $10 million for actionable information regarding foreign government-linked associates of the indicted individuals, their malicious cyber activities, or foreign government-linked use of Media Land or ML.Cloud.
The program also noted that relocation assistance may be available for qualifying information.
International Sanctions Expand Pressure
The indictment follows coordinated international action against the alleged operators. In November 2025, the U.S. Department of the Treasury's Office of Foreign Assets Control, together with authorities from the United Kingdom and Australia, sanctioned Media Land for facilitating global ransomware operations, distributed denial-of-service attacks, and other malicious cyber activities.
The sanctions also targeted Volosovik, Zatolokin, and Pankova individually, along with Media Land subsidiaries Media Land Technology (MLT), Data Center Kirishi (DC Kirishi), and sister company ML Cloud.
On July 13, the European Union also announced sanctions against the companies and key individuals as part of broader efforts to disrupt cybercrime infrastructure.
International Agencies Back the Investigation
The investigation was led by the FBI Cleveland Division with support from the Cybersecurity and Infrastructure Security Agency (CISA) and the Office of Foreign Assets Control.
Authorities also received assistance from the National Police of the Netherlands, the Public Prosecutor's Office of the Netherlands, the United Kingdom's National Crime Agency, the United Kingdom Foreign Commonwealth and Development Office, the Australian Department of Foreign Affairs and Trade, and the Australian Federal Police.
Officials from CISA and partner agencies said disrupting bulletproof hosting providers remains essential because these services form a critical part of the cybercriminal ecosystem by enabling ransomware, phishing, malware, and other malicious operations while helping threat actors remain anonymous.
SOCIAL SHARE CARD GENERATOR