Zum Hauptinhalt springen
tsecurity.de LIVE
Echtzeit-Radar & Feeds
Alle RSS Feeds
👥 Community & Social
YouTube Security VideosRackspace maximizes data center space and compute power with AMD(24.09.2026 um 16:00 Uhr)
Podcasts & Audio BriefingsTechLinked: Android Laptops Are Here…(22.09.2026 um 02:45 Uhr)
Podcasts & Audio BriefingsTechLinked: They’re Really Doing It…(24.09.2026 um 02:56 Uhr)
Podcasts & Audio Briefings9to5Google: Googlebook Hands-On: Android's biggest step in years.(21.09.2026 um 15:00 Uhr)
Podcasts & Audio Briefings9to5Google: 30 days with Pixel 11: What we learned.(22.09.2026 um 17:45 Uhr)
AI & KI NachrichtenNeil Patel: 300 Reviews at 4.2 Beats 15 at 5.0 #shorts(21.09.2026 um 20:03 Uhr)
AI & KI NachrichtenNeil Patel: Google Just Quietly Killed Your Clicks #shorts(22.09.2026 um 20:01 Uhr)
YouTube Security VideosRackspace maximizes data center space and compute power with AMD(24.09.2026 um 16:00 Uhr)
Podcasts & Audio BriefingsTechLinked: Android Laptops Are Here…(22.09.2026 um 02:45 Uhr)
Podcasts & Audio BriefingsTechLinked: They’re Really Doing It…(24.09.2026 um 02:56 Uhr)
Podcasts & Audio Briefings9to5Google: Googlebook Hands-On: Android's biggest step in years.(21.09.2026 um 15:00 Uhr)
Podcasts & Audio Briefings9to5Google: 30 days with Pixel 11: What we learned.(22.09.2026 um 17:45 Uhr)
AI & KI NachrichtenNeil Patel: 300 Reviews at 4.2 Beats 15 at 5.0 #shorts(21.09.2026 um 20:03 Uhr)
AI & KI NachrichtenNeil Patel: Google Just Quietly Killed Your Clicks #shorts(22.09.2026 um 20:01 Uhr)
Intelligence View
⚡ tsecurity.de Intelligence

React2Shell Exploited in Mass Credential Harvesting Campaign Targeting 700+ Hosts

React2Shell Exploited in Mass Credential Harvesting Campaign Targeting 700+ Hosts Post Views:…

0
↗ Quelle (blackhatethicalhacking.com)
Reagiere als Erste:r — dein Feedback zählt!


React2Shell Exploited in Mass Credential Harvesting Campaign Targeting 700+ Hosts


Join our Patreon Channel and Gain access to 70+ Exclusive Walkthrough Videos.


Patreon


Reading Time: 3 Minutes


React2Shell Vulnerability Exploited in Large-Scale Credential Harvesting Campaign


Cybersecurity researchers have uncovered a widespread credential harvesting operation exploiting the React2Shell vulnerability to compromise systems and extract sensitive data at scale.


The campaign, attributed by Cisco Talos to a threat cluster tracked as UAT-10608, has resulted in the compromise of at least 766 hosts across multiple regions and cloud environments. The attackers are leveraging the vulnerability to gain initial access and deploy a sophisticated data collection framework.


Targeting Next.js Applications for Initial Access


The operation primarily targets Next.js applications vulnerable to CVE-2025-55182, a critical flaw in React Server Components and Next.js App Router that enables remote code execution.


Researchers believe the attackers are using automated scanning techniques to identify exposed systems, likely relying on services such as Shodan, Censys, or custom-built scanners to locate vulnerable deployments.


Once a target is identified, the attackers deploy a dropper that initiates a multi-stage infection chain.


Multi-Stage Malware Deploys NEXUS Listener Framework


Following successful exploitation, the attackers deploy a collection framework known as NEXUS Listener, currently observed in its third iteration.


The malware uses automated scripts to systematically harvest sensitive data from compromised systems. This includes:


  • Environment variables and runtime configurations

  • SSH private keys and authorized_keys files

  • Shell command history

  • Kubernetes service account tokens

  • Docker configurations and container details

  • API keys and authentication tokens

  • Cloud credentials from AWS, Google Cloud, and Microsoft Azure

  • Running processes and system metadata


The breadth of data collection highlights a clear objective: to gather as much intelligence as possible about the compromised environment.
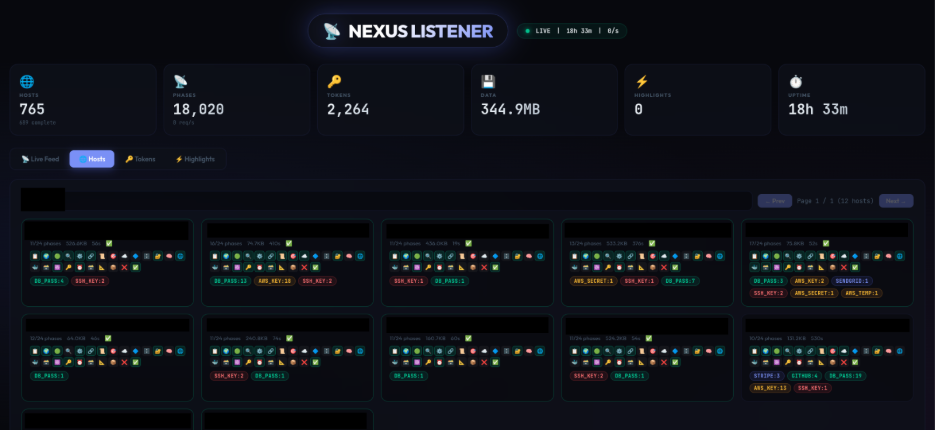

NEXUS Listener victims list.


See Also: So, you want to be a hacker?

Offensive Security, Bug Bounty Courses


Cloud Metadata Services Abused to Extract Credentials


A notable aspect of the campaign is the abuse of cloud instance metadata services to extract temporary credentials.


The malware queries metadata endpoints associated with AWS, Azure, and Google Cloud, allowing attackers to obtain IAM role-based credentials without requiring direct access to secrets stored in code.


This technique enables attackers to expand their reach beyond the initial compromised host and pivot deeper into cloud environments.


Stolen Data Aggregated in Web-Based Control Panel


All harvested data is transmitted to a centralized command-and-control system featuring a web-based interface called NEXUS Listener GUI.


The platform provides attackers with:


  • Searchable access to stolen credentials

  • Statistical insights on compromised hosts

  • Categorization of extracted data

  • Real-time monitoring of campaign activity


Researchers who accessed an exposed instance of the platform found a wide range of sensitive data, including Stripe API keys, GitHub and GitLab tokens, Telegram bot credentials, webhook secrets, database connection strings, and keys for AI platforms such as OpenAI and Anthropic.


Automated and Indiscriminate Targeting Strategy


The scale and diversity of victims suggest the campaign is largely automated, with attackers scanning for any publicly accessible vulnerable systems rather than targeting specific organizations.


This opportunistic approach allows threat actors to rapidly expand their footprint while collecting a broad dataset of credentials and infrastructure information.


Stolen Data Enables Follow-On Attacks


Beyond immediate credential theft, the collected data provides attackers with a detailed blueprint of victim environments.


This includes insights into:


  • Infrastructure architecture

  • Cloud provider usage

  • Third-party integrations

  • Security configurations


Such information can be leveraged to conduct follow-on attacks, including lateral movement, targeted phishing campaigns, or selling access to other threat actors.


Mitigation and Defensive Measures


Organizations are urged to take immediate action to mitigate the risks associated with this campaign. Recommended steps include:


  • Patching vulnerable React and Next.js applications

  • Rotating all potentially exposed credentials

  • Enforcing least privilege access controls

  • Enabling secret scanning across repositories

  • Avoiding reuse of SSH keys

  • Enforcing IMDSv2 on AWS instances


Are u a security researcher? Or a company that writes articles about Cyber Security, Offensive Security (related to information security in general) that match with our specific audience and is worth sharing? If you want to express your idea in an article contact us here for a quote: [email protected]


Sources: thehackernews.com, blog.talosintelligence.com


Source Link


Merch


Offensive Security & Ethical Hacking Course


Begin the learning curve of hacking now!


Information Security Solutions


Find out how Pentesting Services can help you.


Join our Community


The post React2Shell Exploited in Mass Credential Harvesting Campaign Targeting 700+ Hosts first appeared on Black Hat Ethical Hacking.
IoC Intelligence (1 Indikatoren)
CVE-2025-55182
CTI Threat Relationship Graph8 Knoten / 7 Relationen
CVE / Incident Software MITRE ATT&CK CWE Weakness IoC
SOC Incident Playbook: Remote Code Execution (RCE) Defense
title: Detect Exploitation - React2Shell Exploited in Mass Credential Harvesting Campaign Targeting 700+ Hosts
id: cdd65b7e-10d7-4b1d-81e1-a57fe6f6242e
status: experimental
description: Automatisch generierte SIEM-Erkennungsregel basierend auf CTI Intelligence
references:
  - https://tsecurity.de/
author: iShareStuff CTI Automated Detection Engine
date: 2026-09-24
logsource:
  category: network_connection
  product: any
detection:
  selection:
      CommandLine|contains:
        - 'exploit'
  condition: selection
falsepositives:
  - Legitime administrative Zugriffe oder Penetrationstests
level: high
tags:
  - attack.initial_access
  - attack.t1190
rule CTI_Threat_Indicator {
    meta:
        author = "iShareStuff CTI Automated Detection Engine"
        date = "2026-09-24"
        description = "YARA Signature for "
    strings:
        $str = "React2Shell Exploited in Mass " ascii wide
    condition:
        any of them
}
tsecurity.de Cognitive Threat RAG
Fokus-Vektor:

Kognitive Analyse für identifizierte Bedrohung: Erhöhte Bedrohungslage im Bereich React2Shell Exploited in Mass Credential.... Basierend auf 368k Vektor-Korrelationen werden sofortige Isolationsmaßnahmen für betroffene Endpunkte empfohlen.

🛡️ Angriffsfläche & Exposure

Netzwerk/Remote-Zugriff ohne Vorauthentifizierung möglich.

Empfohlene Sofortmaßnahmen
  • 1. Perimeter-Inspektion: Relevante Portfreigaben und exponierte Endpunkte unverzüglich scannen.
  • 2. Patch-Applikation: Hersteller-Hotfix einspielen oder betroffene Daemons in isolierte DMZ-Segmente überführen.
  • 3. Telemetrie & EDR-Alerts: Prozessaufrufe und Child-Processes auf anomale Shell-Spawns überwachen.
🔗 Semantisch verwandte Zero-Days MariaDB 11.7 VEC
Ähnliche Beiträge
🔍 Verwandte News

Auch interessante Nachrichten React2Shell Exploited in Mass Credential Harvesting Campaign Targeting 700+ Hosts

Thematisch verwandte Begriffe: React2Shell, Exploited, Mass, Credential · 6 Treffer

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Laden...

Beiträge werden geladen ...

Laden...

Videos werden geladen ...

Zum Aktualisieren ziehen
ZERO-DAY CVE-2026-97360 | HFS2 version 2.4.0 and earlier contains an unauthenticated arbitrary fil…
Advisory →
TTS Reader • tsecurity.de Voice
tsecurity.de Icon
tsecurity.de App
Offline-Lesen, Eilmeldungen & 0ms Ladezeit

Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.

Nächster Beitrag
Themen-Radar & Intelligence Matrix
Echtzeit-Taxonomie nach Angriffsvektoren & Plattformen

tsecurity.de Live Threat Radar

🔴 LIVE RADAR
MONITORING
AKTIV
CVE-DATENBANK
LIVE
🔍
Community Radar & Live Chat
Sentinel Bot online • Live-Stream
Dein Cluster: Security Explorer
Match:
lädt…
Verbindung zum Community-Stream wird aufgebaut...
Bearbeitungsmodus — Senden überschreibt deine Nachricht
Community-Puls — was gerade passiert
lädt…
Aktivitäten deiner Analysten
lädt…
Neues Thema oder Eilmeldung einreichen

Reiche interessante Links, Zero-Days oder Debatten ein. Die Community entscheidet per Upvote über die Veröffentlichung.

Heiß diskutierte Einreichungen
🔖 Gespeicherte Artikel
📂 Keine gespeicherten Artikel vorhanden.
Zurück Ziehen Vor
Links: vorheriger Artikel Rechts: nächster Artikel unten: schließen
News NIS-2 Frühwarnung Tier-1 Intel TTP ⏱️ 3 Min vor 10 Min
Artikeldaten werden geladen...

Zurück: vorheriger Vor: nächster
↗ Original-Quelle
Social Reaktionen Deine Reaktion zählt
Einstufung & Relevanz-Poll 0 Stimmen
In sozialen Netzwerken teilen 1-Klick