Executive Summary
Cyble Research and Intelligence Labs (CRIL) has identified a novel Android banking trojan, dubbed OverlayPhantom, actively distributed in the wild via malicious URLs.
The with the capability and intent to conduct large-scale fraud across Western markets.
Key Takeaways
- OverlayPhantom is a sophisticated Android banking trojan distributed via phishing URLs that impersonate high-trust applications.
- The malware deploys via a dropper application that simulates a fake Google Play service update and guides victims to enable the Accessibility Service.
- It abuses Android's Accessibility Service to silently monitor foreground app activity, intercept user input, simulate gestures, and maintain persistent control over the infected device.
- The malware currently targets over 180 banking, finance, and cryptocurrency applications across 10 countries using embedded WebView-based HTML phishing overlays that are visually indistinguishable from the legitimate apps they impersonate.
- C&C communication is handled over three dedicated non-standard ports — 9091 for command dispatch, 9092 for device status reporting, and 9090 for screen streaming.
- OverlayPhantom supports over 30 remote commands, enabling the threat actor to perform automated gestures, manipulate clipboard content, lock the device screen, display fake notifications, and capture PIN or password input via custom overlay windows.
- A built-in JPEG-based screen streaming capability, powered by Android's MediaProjection API, grants the threat actor near real-time visual access to the victim's device screen with minimal bandwidth overhead.
Overview
During an investigation into government-themed URL impersonation, Cyble Research and Intelligence Labs (CRIL) uncovered a previously undocumented Android banking trojan, dubbed OverlayPhantom.
The malware is being actively distributed in the wild through malicious URLs and masquerades as legitimate, high-trust applications to deceive users into installing it. CRIL’s analysis indicates that OverlayPhantom has been active since early May 2025.
The initial sample discovered was hosted at hxxps://bitlrewards-app[.]com/api/download/IDAustria, distributing a malicious APK masquerading as ID Austria — the official Austrian government digital identity application.
The choice of this lure is significant, as impersonating a government identity service creates a strong pages bundled directly into the APK's resources.
These pages are meticulously crafted to impersonate legitimate banking and financial applications, deceiving victims into submitting their credentials or payment card details.
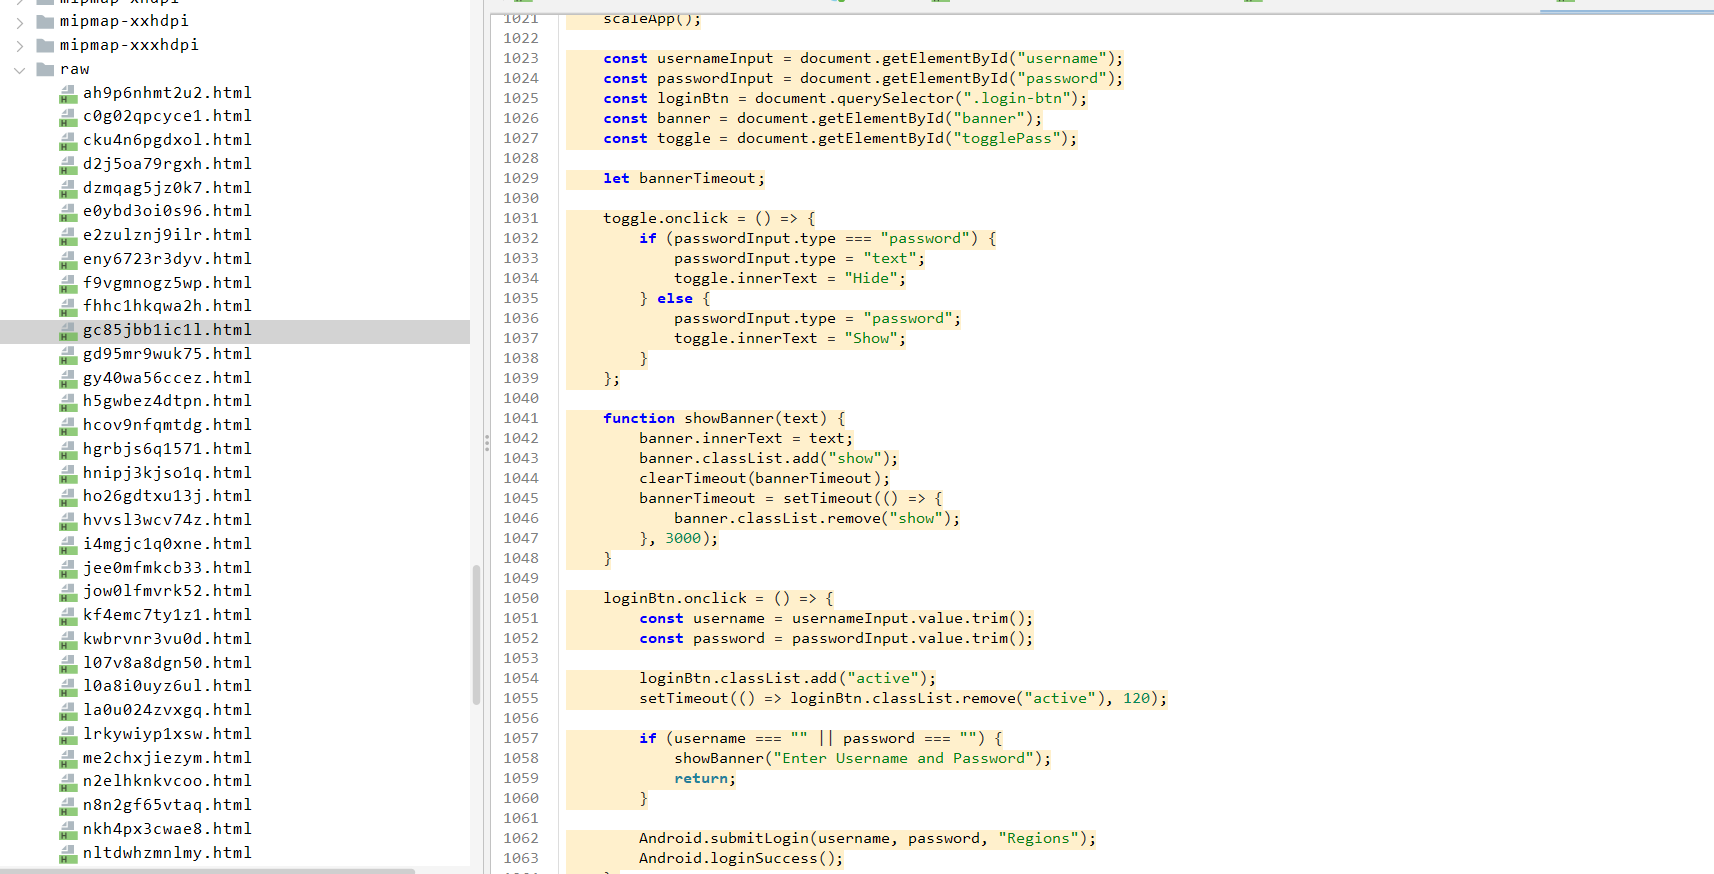
When the victim launches a banking or financial application, OverlayPhantom silently checks whether the application's package name is present in its target list.
Upon a positive match, the malware retrieves the corresponding phishing page from its internal resources, renders it in an embedded WebView, and displays it as a seamless overlay window directly above the legitimate application. From the victim's perspective, the experience is indistinguishable from interacting with the genuine application.
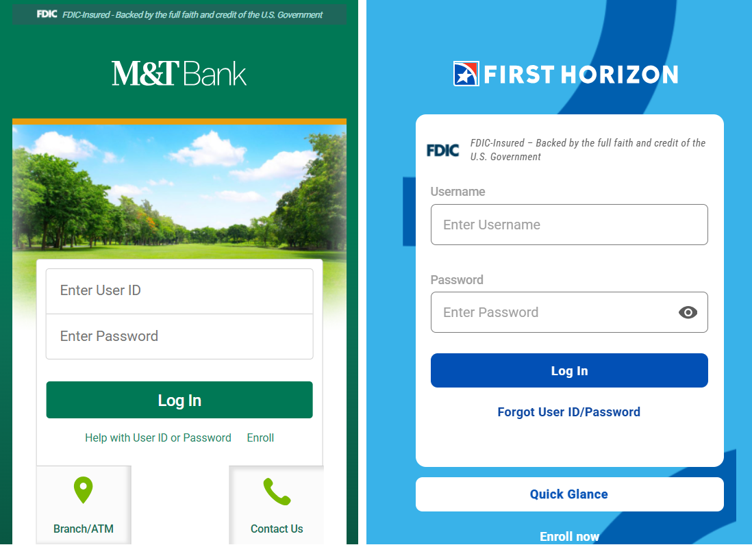
Once the victim enters their credentials into the fraudulent overlay, OverlayPhantom harvests the submitted username, password, or card details and silently exfiltrates the stolen data to the C&C server, completing the credential theft cycle without raising any visible indication of compromise on the device.
Screen Streaming
OverlayPhantom provides real-time screen streaming via JPEG, which can be controlled remotely via the startStreamJpeg and stopStreamJpeg commands.
Upon receiving the startStreamJpeg command, the malware initiates a screen capture using Android's MediaProjection API, creating a VirtualDisplay instance named jpeg-stream and attaching it to an ImageReader to continuously capture the device's screen.
The output is resized to a fixed width of 540 pixels, with the height dynamically calculated to preserve the victim device's native screen aspect ratio.
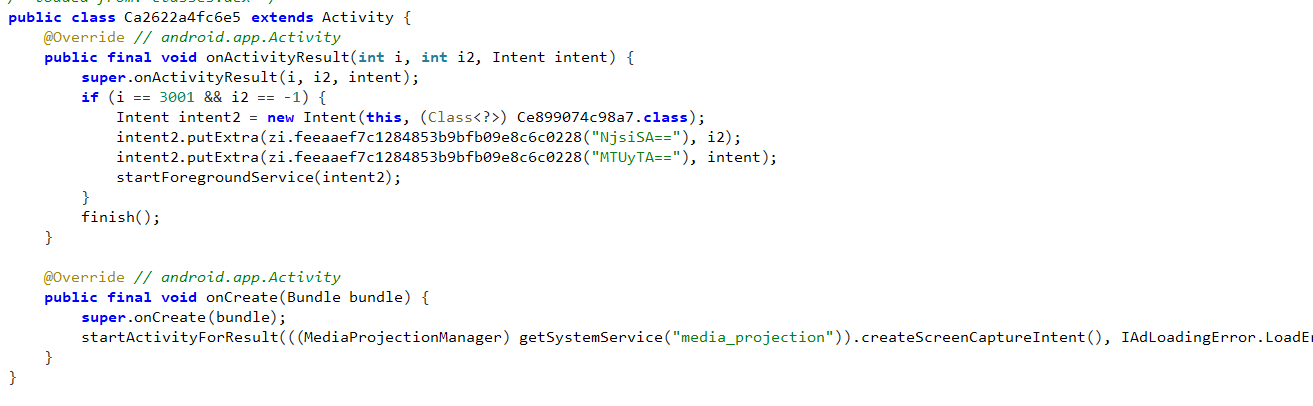
While screen capture is active, the malware establishes a TCP connection to the C&C server on port 9090. Before transmitting any frames, it sends a bot and session identifier, derived from the malware's configured Bot ID and the device ID, to register the streaming session with the operator.
The malware then enters a continuous capture loop, calling acquireLatestImage() to fetch the latest screen frame, converting it into a Bitmap, compressing it as a JPEG, and writing the resulting bytes directly to the socket.
This provides the threat actor with near-real-time visibility into the victim's screen activity while keeping bandwidth consumption lower than that of raw frame transmission.
The streaming loop incorporates resilience logic to handle interruptions gracefully. If no frame is available, the malware briefly sleeps and resumes polling. In the event of a socket failure, it increments a retry counter, pauses for approximately two seconds, closes the active stream and socket, and attempts to re-establish the connection.
Once the retry threshold is exceeded, the streaming flag is disabled to prevent an indefinite number of reconnection attempts. The operator can terminate the stream at any time by issuing the stopStreamJpeg command, which flips the streaming state and invokes the corresponding service logic to cleanly shut down the capture session.
Conclusion
OverlayPhantom represents a mature and methodically engineered Android banking threat. From its deceptive dropper stage — which exploits user trust in the Google Play ecosystem — to its abuse of the Accessibility Service, multi-port C&C architecture, overlay-based credential harvesting, and real-time screen streaming, the malware demonstrates a high degree of operational sophistication.
Its broad targeting scope, encompassing over 180 banking, financial, and cryptocurrency applications across 10 countries at the time of this analysis, further underscores the scale of the threat actor's ambitions. Based on the observed functionality, we anticipate the threat actor’s targeting scope and potential blast radius will continue to expand.
The techniques employed by OverlayPhantom are not novel in isolation, but their combination, particularly the use of government and consumer application lures, hardcoded phishing overlays, and granular remote-control capabilities, reflects a threat actor with both the technical capability and the strategic intent to conduct large-scale financial fraud across multiple regions.
Organizations and individuals operating in the targeted geographies should treat this threat with a high degree of urgency.
Our Recommendations
We have listed some essential . Avoid third-party app stores or links received via SMS, social media, or email.
Never grant permissions and install an application unless you're certain of an app's legitimacy.
Always verify the URL and avoid suspicious links and websites that ask for sensitive information.
Use MFA for banking and financial apps to add an extra layer of protection, even if credentials are compromised.
If you suspect you've been targeted or infected, report the incident to your bank and local authorities immediately. If necessary, reset your credentials and perform a factory reset.
Install a mobile security application that includes real-time scanning.
Ensure your Android OS and apps are updated regularly. Security patches often address vulnerabilities exploited by malware.
MITRE ATT&CK® Techniques
| Tactic | Technique ID | Procedure | |||||||
| Initial Access () | OverlayPhantom is distributed via phishing sites | ||||||||
| Persistence () | Hide Artifacts: Suppress Application Icon () | Obfuscated Files or Information () | Masquerading: Match Legitimate Name or Location () | Abuse Accessibility Features () | Software Discovery () | Screen Capture () | Application Layer Protocol () | Non-Standard Port () | Exfiltration Over C2 Channel ( appeared first on Cyble. Vollständiges Original-Advisory Ausführliche Details, Exploit-Analyse & Hersteller-Stellungnahme auf cyble.com. Wie bewertest du diesen Beitrag? 1 Klick Feedback Teilen mit Netzwerk & Team: Community-Analysen & Experten-Meinungen 0Verfasse deine eigene Analyse, teile Workarounds oder diskutiere diesen Vorfall im Blog. Noch keine Community-Analyse verfasst. Markiere einen Textabschnitt oder klicke oben auf „ Eigene Analyse verfassen“! Community Pulse: Relevanz-Einschätzung 1 Klick Experten-Votum 🔴 Akute Relevanz 0% 🟡 In Evaluierung 0% 🟢 Keine Auswirkung 0% Spannende Innovation 0% Verwandte Story-Cluster & Quellen (Vektor-KI) Tipp: Mit Pfeiltasten [ ← ] und [ → ] blättern  Ähnliche Beiträge
🔍 Verwandte News
Auch interessante Nachrichten OverlayPhantom: The Android Banking Trojan Hiding in Plain SightThematisch verwandte Begriffe: OverlayPhantom, Android, Banking, Trojan · 6 Treffer 🤖 Android Tipps SmartDroid.de Mega-Upate für Google Pixel: Android 17 QPR1 bringt euch 25+ Neuerungen und 20 Fixes 🔧 Programmierung DEV Community The Realpolitik of Tech: Navigating the Machiavellian Reality of People Management
Laden...
Videos werden geladen ...
Laden...
Beiträge werden geladen ...
Laden...
Videos werden geladen ...
Laden...
Beiträge werden geladen ...
Laden...
Videos werden geladen ...
Laden...
Beiträge werden geladen ...
Laden...
Videos werden geladen ...
Laden...
Beiträge werden geladen ...
Laden...
Videos werden geladen ...
🔖 Gespeicherte Artikel
📂
Keine gespeicherten Artikel vorhanden.
News
⏱️ 3 Min
vor 10 Min
Artikeldaten werden geladen...
tsecurity.de AppOffline-Lesen, Eilmeldungen & 0ms Ladezeit
Installiere tsecurity.de direkt auf deinen Home-Bildschirm für das ultimative Vollbild-Magazinerlebnis ohne Browser-Leisten.
Nächster Beitrag
Community Radar & Live Chat
Sentinel Bot online • Live-Stream
Dein Cluster:
Security Explorer
Match:
lädt…
Aktivitäten deiner Analystenlädt…
Neues Thema oder Eilmeldung einreichenReiche interessante Links, Zero-Days oder Debatten ein. Die Community entscheidet per Upvote über die Veröffentlichung. Heiß diskutierte Einreichungen |
SOCIAL SHARE CARD GENERATOR