
Zum Hauptinhalt springen
•••
YouTube Security VideosAtlassian: How to Find GitHub Pull Requests Ready to Merge with Rovo(30.10.2026 um 04:11 Uhr)
•••
YouTube Security VideosGoogle Workspace: Last-minute Halloween costumes ideas! 🎃🦇 #Shorts(30.10.2026 um 01:46 Uhr)
•
YouTube Security VideosMicrosoft Mechanics: How Conditional Access Plans and Rules Work(30.10.2026 um 02:15 Uhr)
•
Windows Tipps & SecurityDDR5-RAM mit CUDIMM: So holen Sie mehr Tempo aus Ihrem Arbeitsspeicher(30.10.2026 um 08:00 Uhr)
•••••
YouTube Security VideosAtlassian: How to Find GitHub Pull Requests Ready to Merge with Rovo(30.10.2026 um 04:11 Uhr)
•••
YouTube Security VideosGoogle Workspace: Last-minute Halloween costumes ideas! 🎃🦇 #Shorts(30.10.2026 um 01:46 Uhr)
•
YouTube Security VideosMicrosoft Mechanics: How Conditional Access Plans and Rules Work(30.10.2026 um 02:15 Uhr)
•
Windows Tipps & SecurityDDR5-RAM mit CUDIMM: So holen Sie mehr Tempo aus Ihrem Arbeitsspeicher(30.10.2026 um 08:00 Uhr)
••
Intelligence View
⚡ tsecurity.de Intelligence

Microsoft Mechanics: How Conditional Access Plans and Rules Work

HD Video
How Conditional Access Plans and Rules Work
Video abspielen

Video von Microsoft Mechanics auf YouTube: How do you stop rebuilding the same users and conditions in every Conditional Access policy? In a Microsoft Entra…

Beitrag
0
Seite
0
↗ Quelle (Microsoft Mechanics)
Social ReaktionenReagiere als Erste:r — dein Feedback zählt!

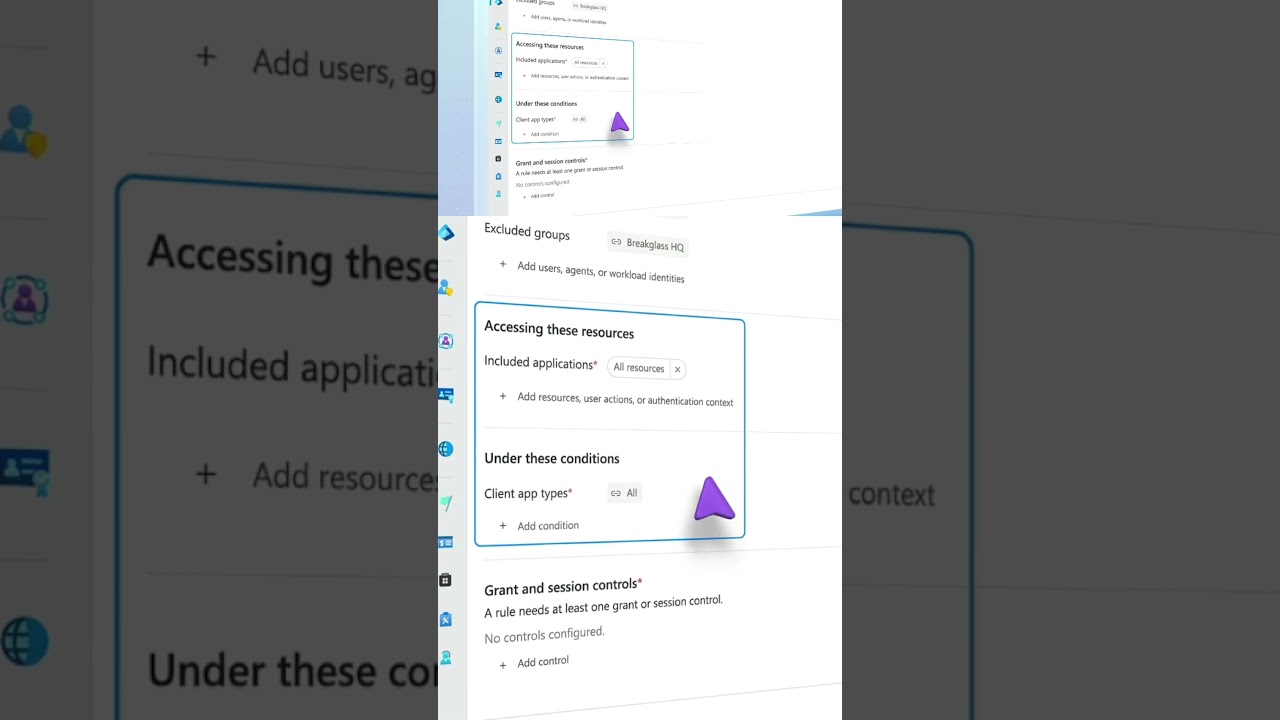
How do you stop rebuilding the same users and conditions in every Conditional Access policy? In a Microsoft Entra policy plan, you define identities, resources, user actions, authentication context and shared conditions like risk levels, devices, network locations and client app types once. Every rule inherits them automatically and adds its own conditions and grant or session controls. Each plan also has its own name, description, owner and tags.


▶ Full video: https://youtu.be/BUI5LZPoHAs

▶ Learn more: https://aka.ms/ConditionalAccessPolicyPlans


#Shorts #ConditionalAccess #MicrosoftEntra #ZeroTrust #IdentitySecurity
🔍 CTI & Forensik

Cyber Threat Intelligence & Forensik

ATT&CK-Navigator · IoC-Radar · Exploit-Belege
CTI Threat Relationship Graph
Akteure · Techniken · Beziehungen
2 Knoten · 1 Relationen
CVE / Incident Threat Actor Software MITRE ATT&CK CWE Weakness IoC
Intelligence Digest — kostenlos Täglich die wichtigsten Security-News · jederzeit abbestellbar
Community Rating & Social Proof
⭐ Leser-Wertung
–
Ø / 5.0
Noch keine Leser-Bewertungen
War diese Seite hilfreich?
0
Jetzt Bewertung abgeben
🟢 Niedrig (1-3.9) 🟡 Mittel (4.0-6.9) 🔴 Hoch (7.0-8.9) Kritisch (9.0-10.0)
Zum Aktualisieren ziehen
Nächster Beitrag