
Zum Hauptinhalt springen
•
IT Security ToolsTails 7.16(30.10.2026 um 01:00 Uhr)
•
IT Security ToolsNew Release: Tails 7.16(30.10.2026 um 01:00 Uhr)
•
IT Security ToolsWhatPatchguardProtects(30.10.2026 um 08:52 Uhr)
•
IT Security NachrichtenTop 10 Best UEBA Tools in 2026 [Ranked & Scored](30.10.2026 um 08:37 Uhr)
••••
Sicherheitslücken (CVE)CISA Warns of GitLab Integer Overflow Vulnerability Exploited in Attacks(30.10.2026 um 09:28 Uhr)
•••
IT Security ToolsTails 7.16(30.10.2026 um 01:00 Uhr)
•
IT Security ToolsNew Release: Tails 7.16(30.10.2026 um 01:00 Uhr)
•
IT Security ToolsWhatPatchguardProtects(30.10.2026 um 08:52 Uhr)
•
IT Security NachrichtenTop 10 Best UEBA Tools in 2026 [Ranked & Scored](30.10.2026 um 08:37 Uhr)
••••
Sicherheitslücken (CVE)CISA Warns of GitLab Integer Overflow Vulnerability Exploited in Attacks(30.10.2026 um 09:28 Uhr)
••
Intelligence View
⚡ tsecurity.de Intelligence

Microsoft Mechanics: How Conditional Access Plans and Rules Work

HD Video
How Conditional Access Plans and Rules Work
Video abspielen

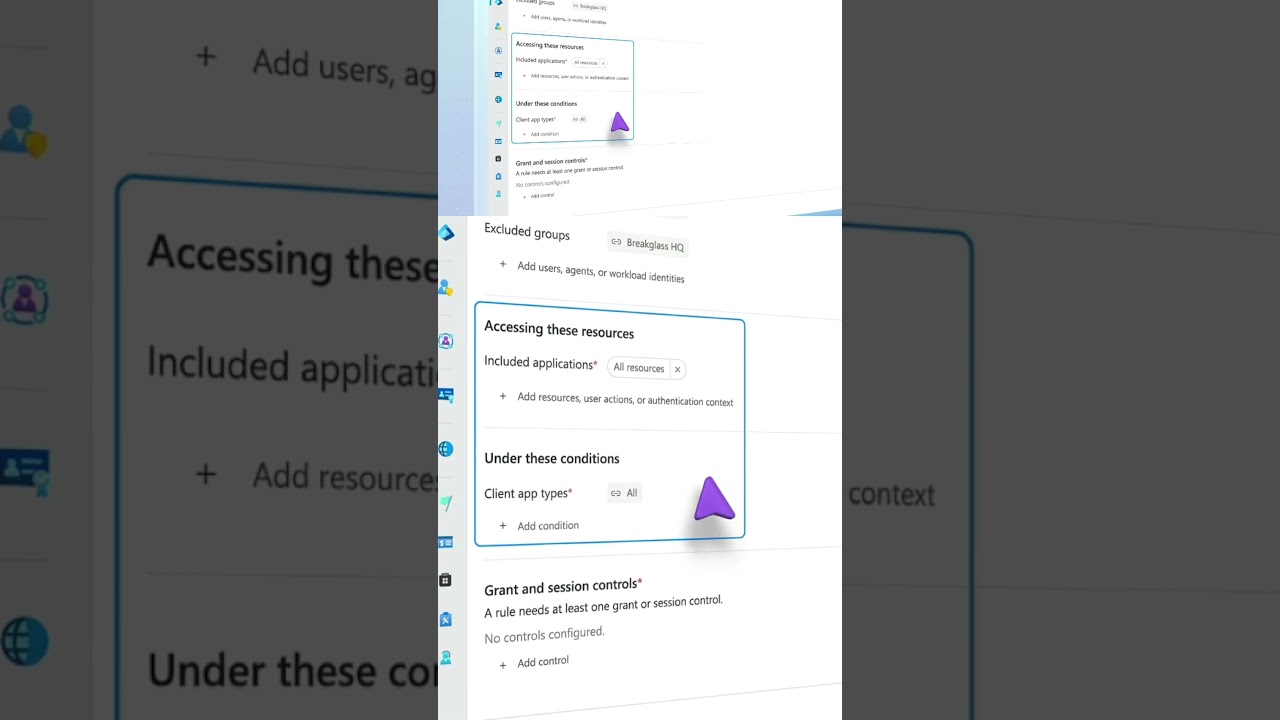
Video von Microsoft Mechanics auf YouTube: How do you stop rebuilding the same users and conditions in every Conditional Access policy? In a Microsoft Entra…

Beitrag
0
Seite
0
↗ Quelle (Microsoft Mechanics)
Social ReaktionenReagiere als Erste:r — dein Feedback zählt!

How do you stop rebuilding the same users and conditions in every Conditional Access policy? In a Microsoft Entra policy plan, you define identities, resources, user actions, authentication context and shared conditions like risk levels, devices, network locations and client app types once. Every rule inherits them automatically and adds its own conditions and grant or session controls. Each plan also has its own name, description, owner and tags.


▶ Full video: https://youtu.be/BUI5LZPoHAs

▶ Learn more: https://aka.ms/ConditionalAccessPolicyPlans


#Shorts #ConditionalAccess #MicrosoftEntra #ZeroTrust #IdentitySecurity
🔍 CTI & Forensik

Cyber Threat Intelligence & Forensik

ATT&CK-Navigator · IoC-Radar · Exploit-Belege
CTI Threat Relationship Graph
Akteure · Techniken · Beziehungen
2 Knoten · 1 Relationen
CVE / Incident Threat Actor Software MITRE ATT&CK CWE Weakness IoC
Intelligence Digest — free The top security news daily · unsubscribe anytime
Community Rating & Social Proof
⭐ Leser-Wertung
–
Ø / 5.0
No reader ratings yet
Was this page helpful?
0
Jetzt Bewertung abgeben
🟢 Niedrig (1-3.9) 🟡 Mittel (4.0-6.9) 🔴 Hoch (7.0-8.9) Kritisch (9.0-10.0)

Related story clusters & sources (vector AI)

Pull to refresh
Nächster Beitrag