
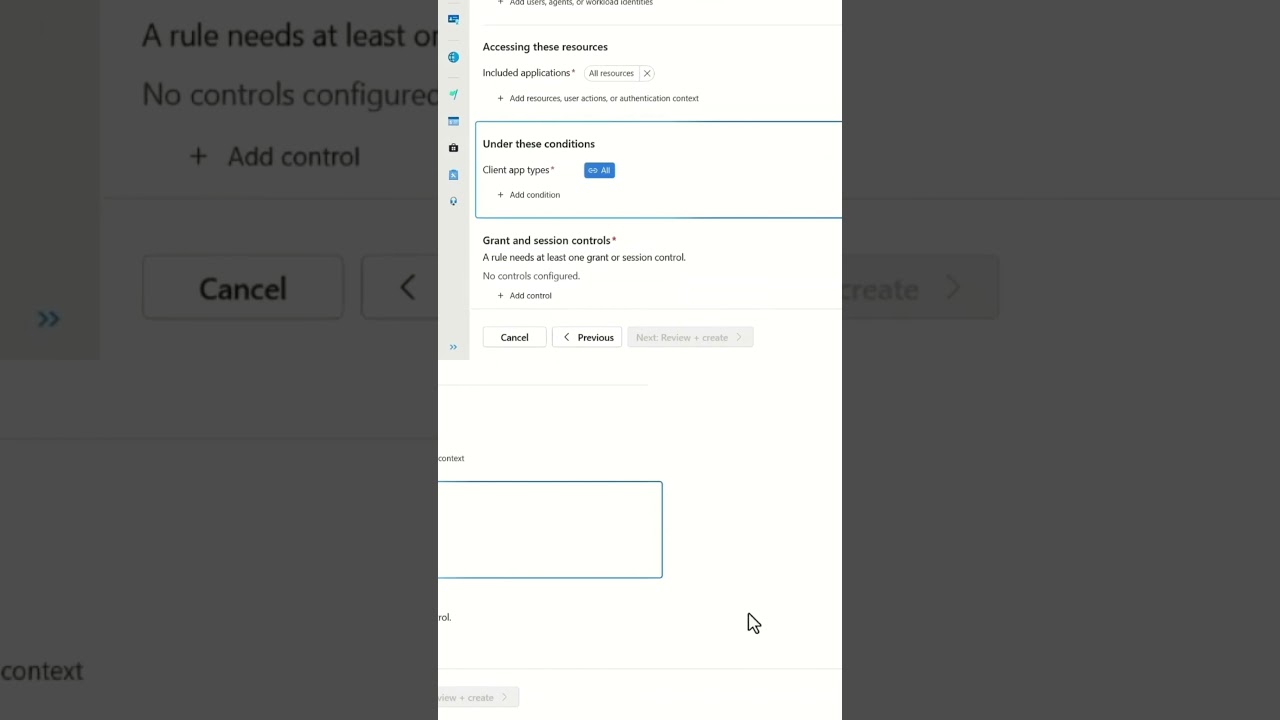
Can you add a phishing-resistant MFA requirement without re-entering included and excluded groups? In a Microsoft Entra Conditional Access policy plan, the new rule inherits the plan's HQ users and break-glass exclusion. You assign all resources, then grant access only when the user meets the Phishing-resistant MFA authentication strength, so every headquarters user has to meet it for everything they access.
▶ Full video: https://youtu.be/BUI5LZPoHAs
▶ Learn more: https://aka.ms/ConditionalAccessPolicyPlans
#Shorts #ConditionalAccess #MicrosoftEntra #ZeroTrust #IdentitySecurity
▶ Full video: https://youtu.be/BUI5LZPoHAs
▶ Learn more: https://aka.ms/ConditionalAccessPolicyPlans
#Shorts #ConditionalAccess #MicrosoftEntra #ZeroTrust #IdentitySecurity