
Zum Hauptinhalt springen
•••
Unix & Linux ServerUSN-8994-1: libvips vulnerabilities(03.11.2026 um 18:39 Uhr)
•
Sicherheitslücken (CVE)USN-8996-1: APT vulnerability(04.11.2026 um 14:37 Uhr)
•
Sicherheitslücken (CVE)USN-8997-1: Net-SNMP vulnerability(04.11.2026 um 16:25 Uhr)
•
Sicherheitslücken (CVE)USN-8998-1: Squid vulnerability(04.11.2026 um 16:32 Uhr)
•
Sicherheitslücken (CVE)USN-8999-1: Pillow vulnerabilities(04.11.2026 um 16:49 Uhr)
•
Sicherheitslücken (CVE)USN-9000-1: Twisted vulnerability(04.11.2026 um 17:24 Uhr)
•••••
Unix & Linux ServerUSN-8994-1: libvips vulnerabilities(03.11.2026 um 18:39 Uhr)
•
Sicherheitslücken (CVE)USN-8996-1: APT vulnerability(04.11.2026 um 14:37 Uhr)
•
Sicherheitslücken (CVE)USN-8997-1: Net-SNMP vulnerability(04.11.2026 um 16:25 Uhr)
•
Sicherheitslücken (CVE)USN-8998-1: Squid vulnerability(04.11.2026 um 16:32 Uhr)
•
Sicherheitslücken (CVE)USN-8999-1: Pillow vulnerabilities(04.11.2026 um 16:49 Uhr)
•
Sicherheitslücken (CVE)USN-9000-1: Twisted vulnerability(04.11.2026 um 17:24 Uhr)
••
Intelligence View
⚡ tsecurity.de Intelligence

Microsoft Mechanics: Phishing-Resistant MFA with Conditional Access Authentication Strength

HD Video
Phishing-Resistant MFA with Conditional Access Authentication Strength
Video abspielen

Video von Microsoft Mechanics auf YouTube: Can you add a phishing-resistant MFA requirement without re-entering included and excluded groups? In a Microsoft…

Beitrag
0
Seite
0
↗ Quelle (Microsoft Mechanics)
Social ReaktionenReagiere als Erste:r — dein Feedback zählt!

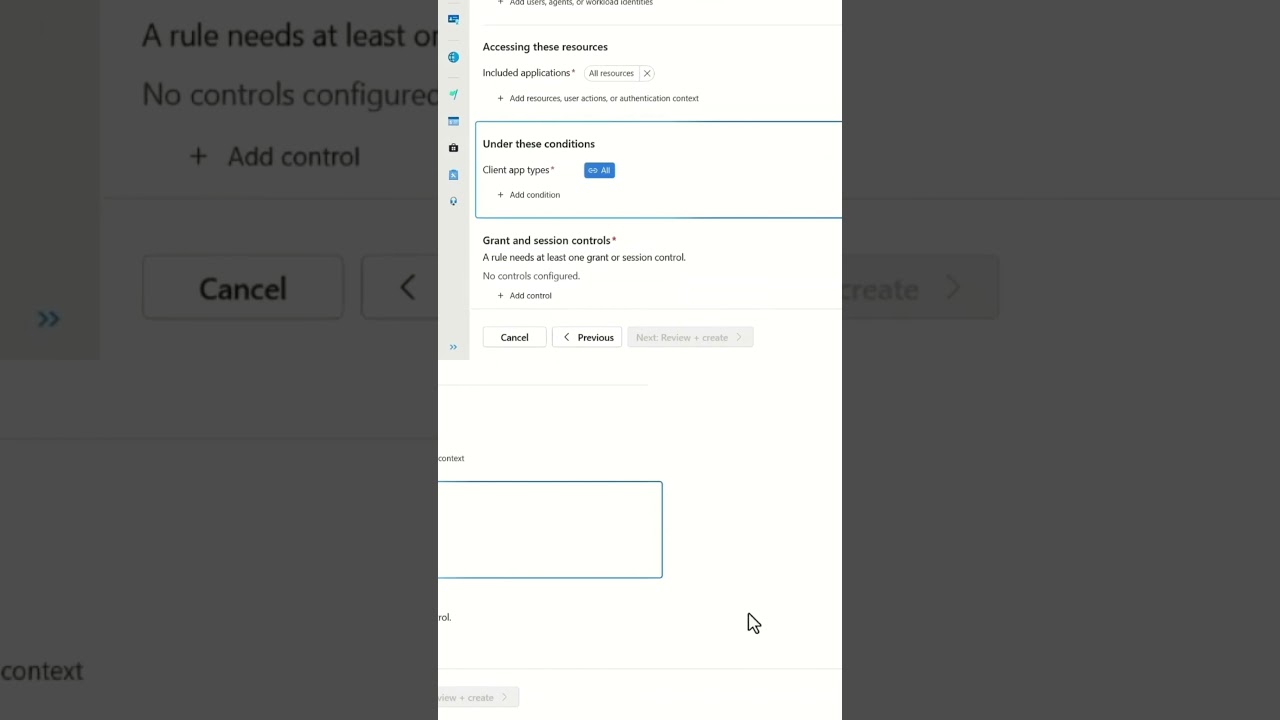
Can you add a phishing-resistant MFA requirement without re-entering included and excluded groups? In a Microsoft Entra Conditional Access policy plan, the new rule inherits the plan's HQ users and break-glass exclusion. You assign all resources, then grant access only when the user meets the Phishing-resistant MFA authentication strength, so every headquarters user has to meet it for everything they access.


▶ Full video: https://youtu.be/BUI5LZPoHAs

▶ Learn more: https://aka.ms/ConditionalAccessPolicyPlans


#Shorts #ConditionalAccess #MicrosoftEntra #ZeroTrust #IdentitySecurity
🔍 CTI & Forensik

Cyber Threat Intelligence & Forensik

ATT&CK-Navigator · IoC-Radar · Exploit-Belege
MITRE ATT&CK Matrix Navigator
1 belegte Technik
T1566TA0001 · Initial Access
Phishing
Mitigation: M1054 User Training & Email Gateway Filtering
Quelle: Kontext-Klassifikation des Artikeltextes · Konfidenz 75%
Napęd szkolenia świadomości, sprawdzić filtrowanie bramy poczty, zweryfikować SPF / DKIM / DMARC.
Initial Access
CTI Threat Relationship Graph
Akteure · Techniken · Beziehungen
4 Knoten · 3 Relationen
CVE / Incident Threat Actor Software MITRE ATT&CK CWE Weakness IoC
Intelligence Digest - bezpłatnie Codziennie najważniejsze wiadomości bezpieczeństwa · można pobrać w każdej chwili
Community Rating & Social Proof
⭐ Leser-Wertung
–
Ø / 5.0
Brak recenzji czytelników
Czy ta strona była pomocna?
0
Jetzt Bewertung abgeben
🟢 Niedrig (1-3.9) 🟡 Mittel (4.0-6.9) 🔴 Hoch (7.0-8.9) Kritisch (9.0-10.0)

Powiązany klaster opowieści i źródła (wektor AI)

Rysunek do aktualizacji
Nächster Beitrag